
FAMAUTH CDAT – Reno, NV April 23-25, 2024 New URL:
KL
Published · 18 slides · 0 views

1 / 1
Description
FAMAUTH CDAT Reno, NV April 23-25, 2024 New URL: https:famauth.wildfire.gov Tile View FAMAuth - REQUEST NEW ACCOUNT Sign in to the Wildland Fire Application Portal at https:famauth.wildfire.gov. Select the application you need access
Related Topics
Share
Embed code
Download this presentation From Below
"FAMAUTH CDAT – Reno, NV April 23-25, 2024 New URL:" is the property of its rightful owner. Permission is granted to download and print the materials on this website for personal, non-commercial use only, and to display it on your personal computer provided you do not modify the materials and that you retain all copyright notices contained in the materials. By downloading content from our website, you accept the terms of this agreement.
Presentation Transcript
01
FAMAUTH CDAT – Reno, NV
April 23-25, 2024<br>
April 23-25, 2024<br>
02
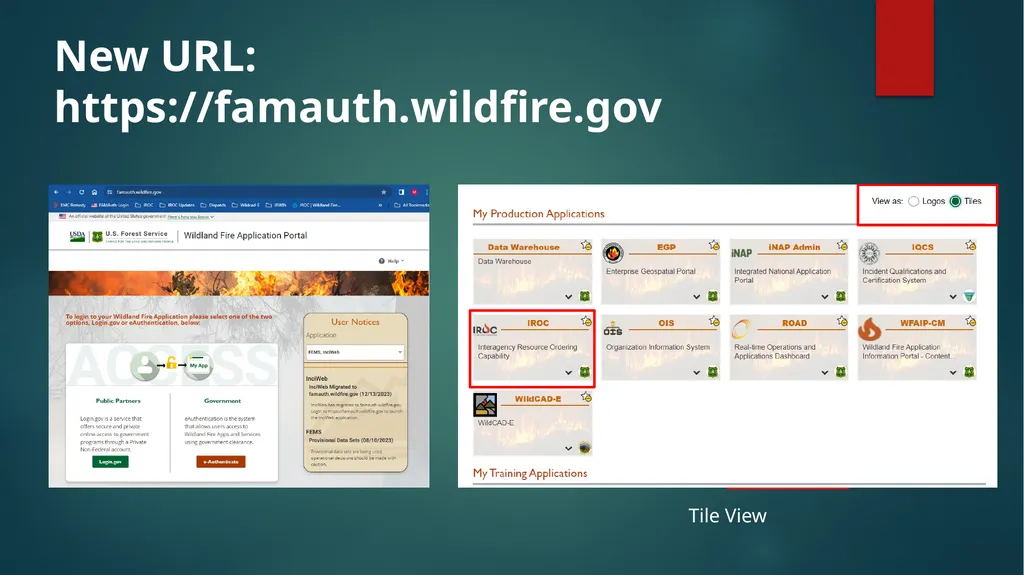
New URL: https://famauth.wildfire.gov Tile View<br>
03
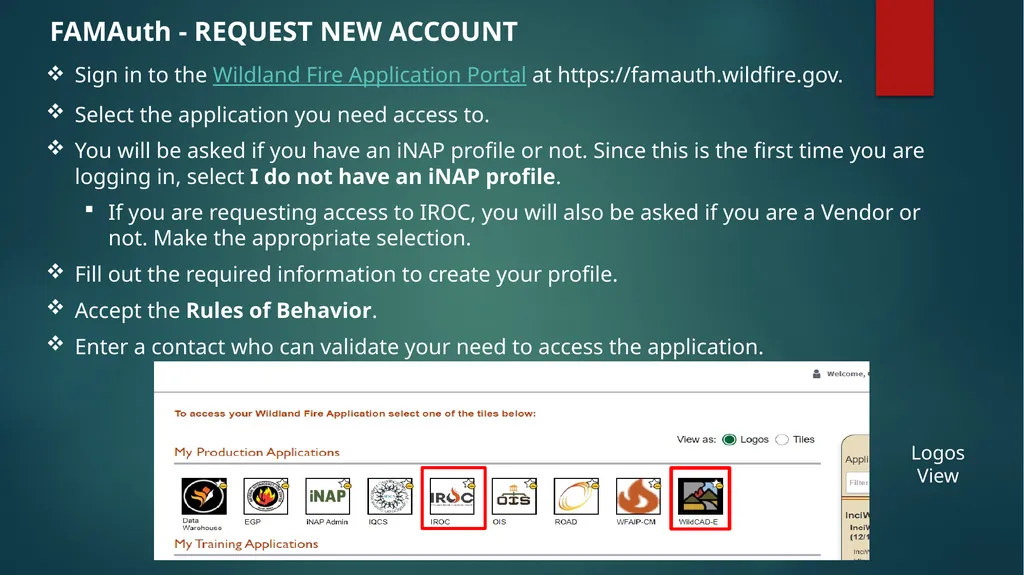
FAMAuth - REQUEST NEW ACCOUNT Sign in to the Wildland Fire Application Portal at https://famauth.wildfire.gov.
Select the application you need access to.
You will be asked if you have an iNAP profile or not. Since this is the first time you are logging in, select I do not have an iNAP profile.
If you are requesting access to IROC, you will also be asked if you are a Vendor or not. Make the appropriate selection.
Fill out the required information to create your profile.
Accept the Rules of Behavior.
Enter a contact who can validate your need to access the application. Logos View<br>
04
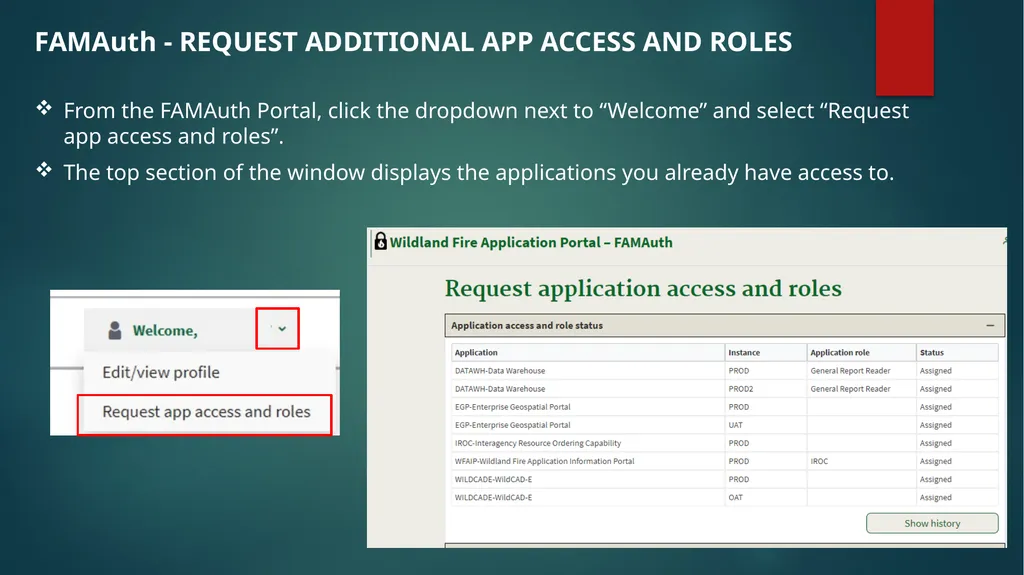
From the FAMAuth Portal, click the dropdown next to “Welcome” and select “Request app access and roles”.
The top section of the window displays the applications you already have access to. FAMAuth - REQUEST ADDITIONAL APP ACCESS AND ROLES<br>
The top section of the window displays the applications you already have access to. FAMAuth - REQUEST ADDITIONAL APP ACCESS AND ROLES<br>
05
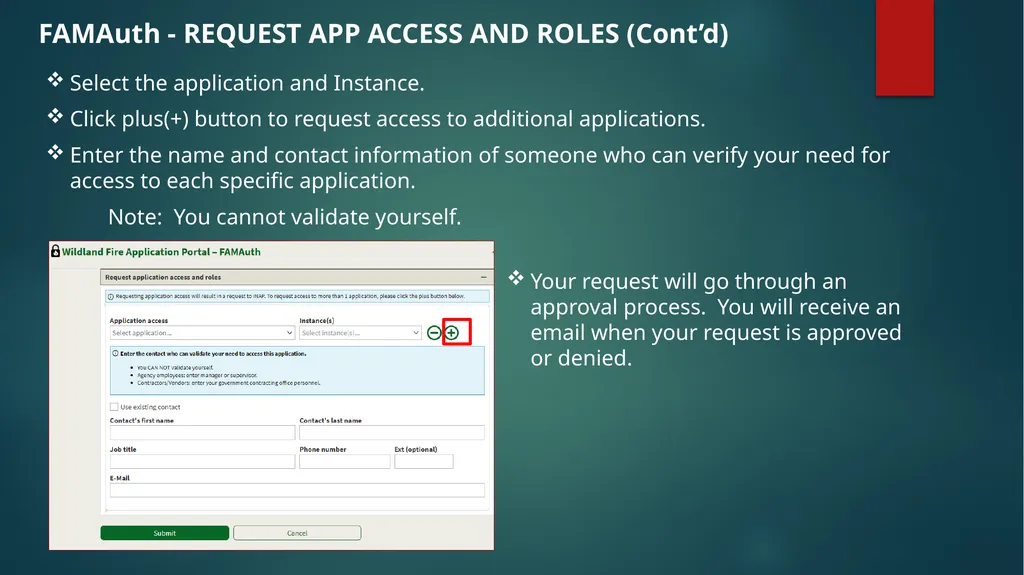
Select the application and Instance.
Click plus(+) button to request access to additional applications.
Enter the name and contact information of someone who can verify your need for access to each specific application.
Note: You cannot validate yourself. FAMAuth - REQUEST APP ACCESS AND ROLES (Cont’d) Your request will go through an approval process. You will receive an email when your request is approved or denied.<br>
06
FAMAuth-NEW TERMS: PASSWORD USER vs NON-PASSWORD USER Password Users
Users have access to apps requiring a username and password to sign in, such as FTP (WinSCP) and ICBS.
Expired Password: After 60 days of not authorizing to any application.
Disabled: After 180 days
Removed: After 330 days (access to applications is also removed).
Non-Password Users
Most FAM Applications no longer use iNAP for authentication and therefore, no longer require a password.
Inactive: 60 days of not authorizing to any application
Note: Users can still self-reactivate their profile and maintain access to their apps.
Removed: After 330 days (access to applications is also removed).
Note: Users with Expired Password, Disabled, or Removed profile status must contact the IIA Help Desk to have their profile reactivated.<br>
07
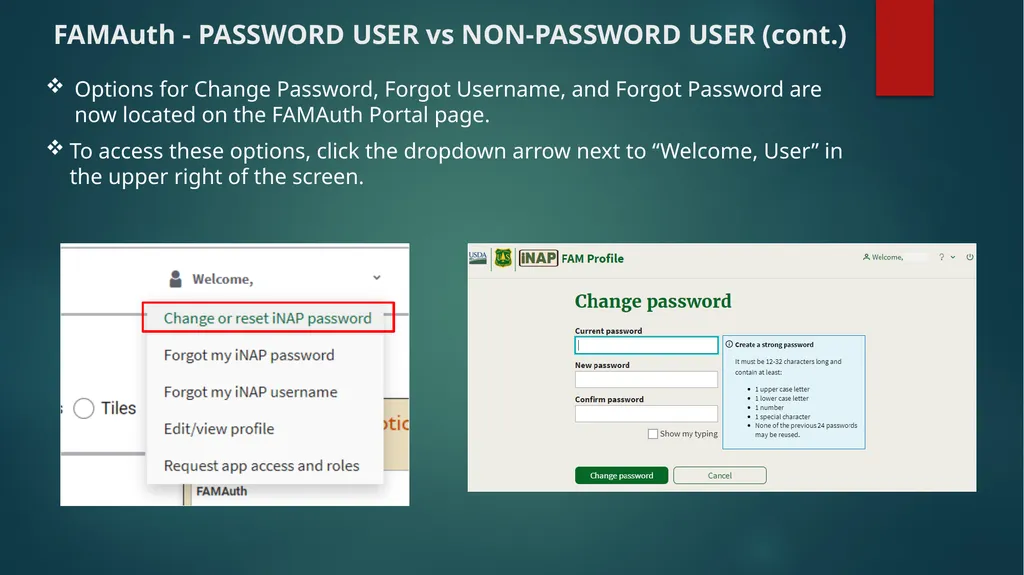
FAMAuth - PASSWORD USER vs NON-PASSWORD USER (cont.) Options for Change Password, Forgot Username, and Forgot Password are now located on the FAMAuth Portal page.
To access these options, click the dropdown arrow next to “Welcome, User” in the upper right of the screen.<br>
To access these options, click the dropdown arrow next to “Welcome, User” in the upper right of the screen.<br>
08
FAMAuth - self reactivate ability Users that haven’t signed into any applications in the past 60 days can self-reactivate their profile.
Self-Reactivation can occur between 60 and 330 days of no authorization to any applications.
Access to applications is maintained.
After 330 days of not signing in, the profile is placed in a Removed status and access to apps is removed. Users must contact IIA Help Desk to have it reactivated.
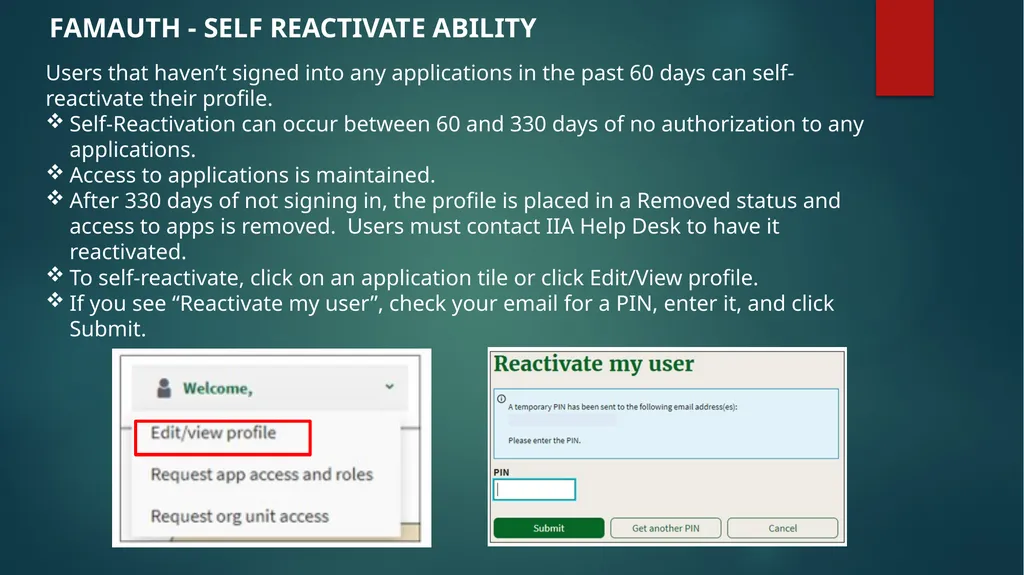
To self-reactivate, click on an application tile or click Edit/View profile.
If you see “Reactivate my user”, check your email for a PIN, enter it, and click Submit.<br>
09
Requesting WildCAD-E Access https://famauth.wildfire.gov Select your authentication method: Login.gov or e-Auth.
If you do not have access to the application, you will request access. FAMAuth will automatically re-direct you to the iNAP screen to request access.
This request will need to be approved by a WildCAD-E SME to give you the access to WildCAD-E.<br>
If you do not have access to the application, you will request access. FAMAuth will automatically re-direct you to the iNAP screen to request access.
This request will need to be approved by a WildCAD-E SME to give you the access to WildCAD-E.<br>
10
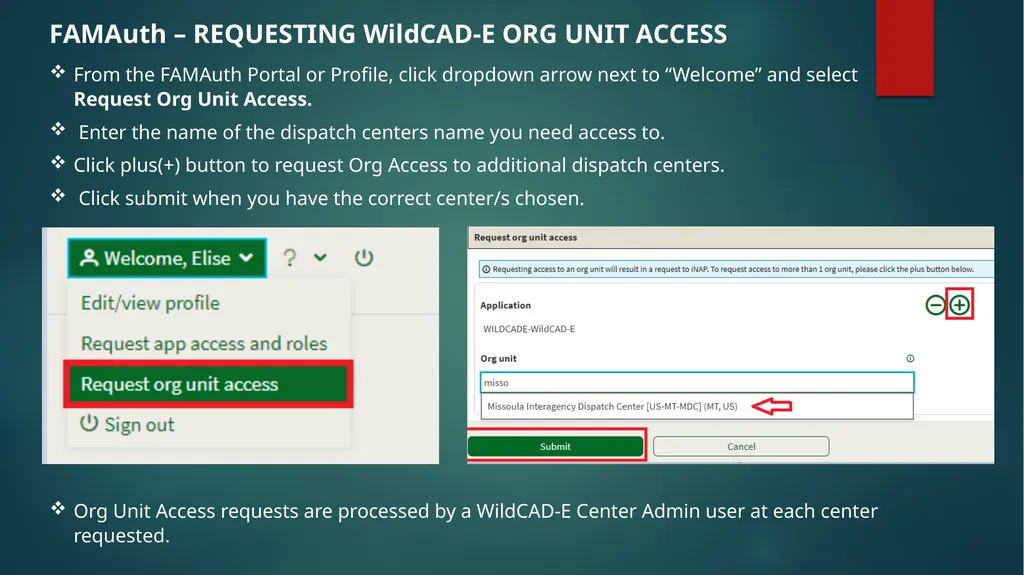
From the FAMAuth Portal or Profile, click dropdown arrow next to “Welcome” and select Request Org Unit Access.
Enter the name of the dispatch centers name you need access to.
Click plus(+) button to request Org Access to additional dispatch centers.
Click submit when you have the correct center/s chosen. Org Unit Access requests are processed by a WildCAD-E Center Admin user at each center requested. FAMAuth – REQUESTING WildCAD-E ORG UNIT ACCESS<br>
11
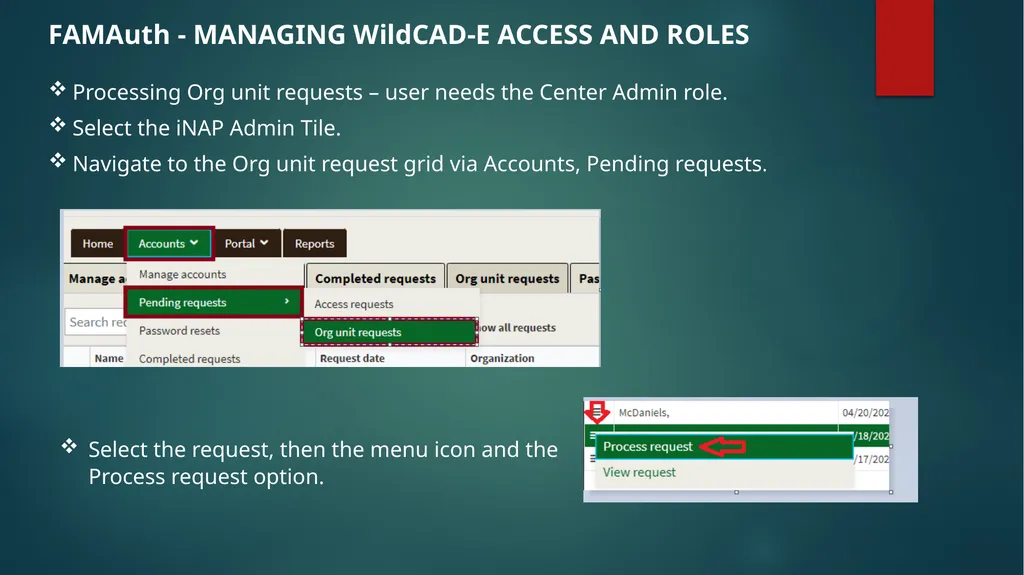
Processing Org unit requests – user needs the Center Admin role.
Select the iNAP Admin Tile.
Navigate to the Org unit request grid via Accounts, Pending requests. FAMAuth - MANAGING WildCAD-E ACCESS AND ROLES Select the request, then the menu icon and the Process request option.<br>
Select the iNAP Admin Tile.
Navigate to the Org unit request grid via Accounts, Pending requests. FAMAuth - MANAGING WildCAD-E ACCESS AND ROLES Select the request, then the menu icon and the Process request option.<br>
12
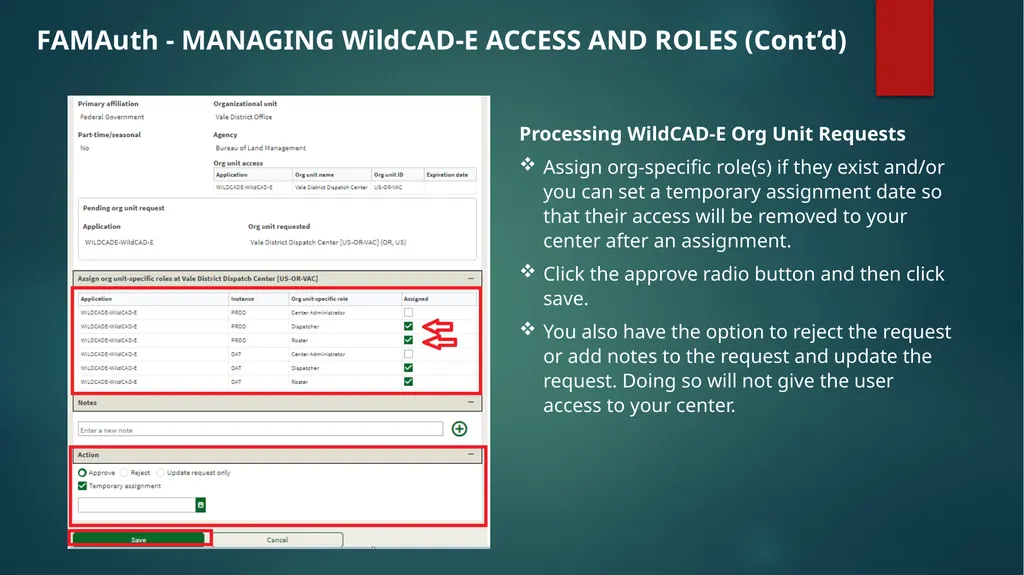
FAMAuth - MANAGING WildCAD-E ACCESS AND ROLES (Cont’d) Processing WildCAD-E Org Unit Requests
Assign org-specific role(s) if they exist and/or you can set a temporary assignment date so that their access will be removed to your center after an assignment.
Click the approve radio button and then click save.
You also have the option to reject the request or add notes to the request and update the request. Doing so will not give the user access to your center.<br>
13
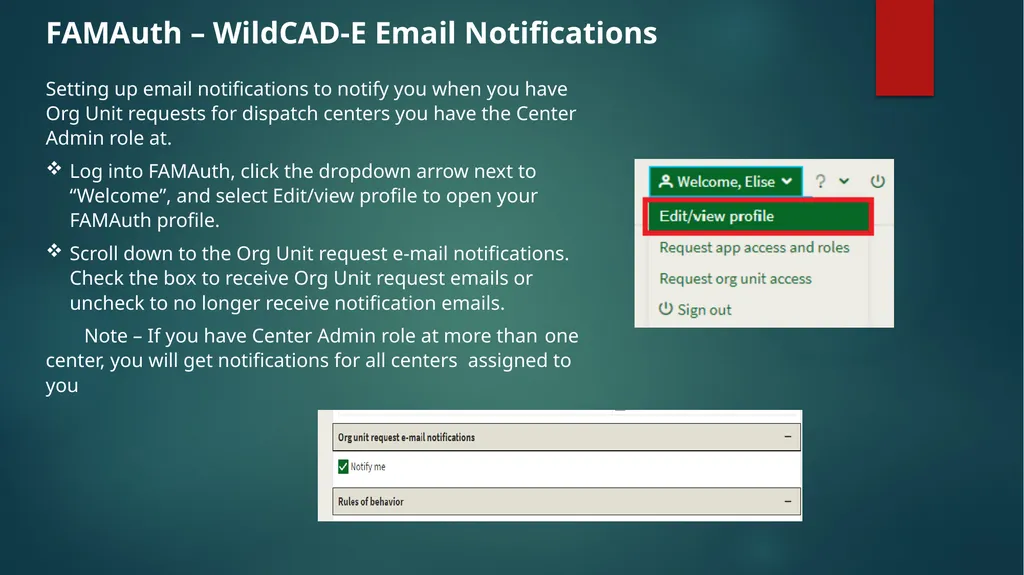
Setting up email notifications to notify you when you have Org Unit requests for dispatch centers you have the Center Admin role at.
Log into FAMAuth, click the dropdown arrow next to “Welcome”, and select Edit/view profile to open your FAMAuth profile.
Scroll down to the Org Unit request e-mail notifications. Check the box to receive Org Unit request emails or uncheck to no longer receive notification emails.
Note – If you have Center Admin role at more than one center, you will get notifications for all centers assigned to you FAMAuth – WildCAD-E Email Notifications<br>
14
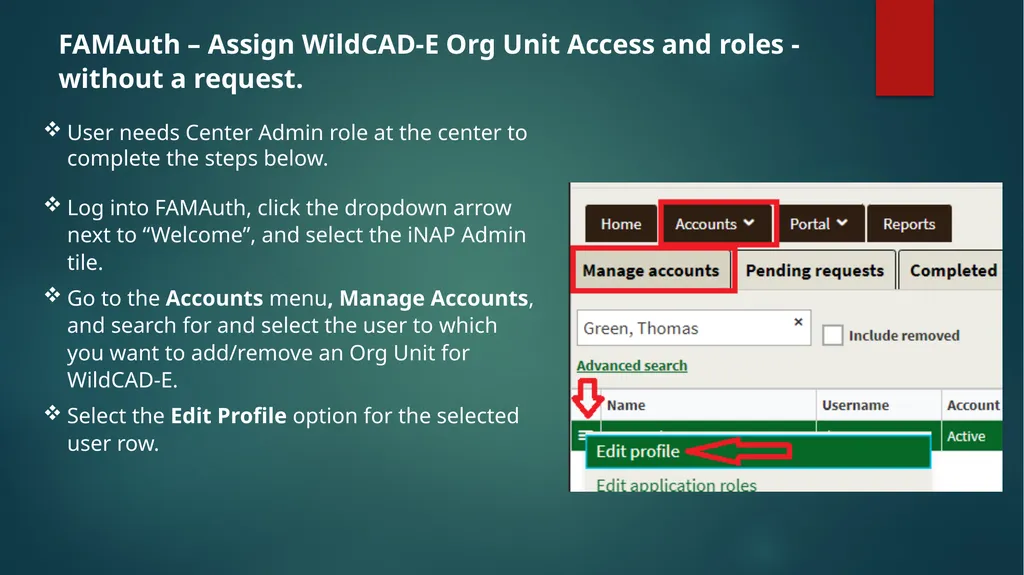
Log into FAMAuth, click the dropdown arrow next to “Welcome”, and select the iNAP Admin tile.
Go to the Accounts menu, Manage Accounts, and search for and select the user to which you want to add/remove an Org Unit for WildCAD-E.
Select the Edit Profile option for the selected user row. FAMAuth – Assign WildCAD-E Org Unit Access and roles - without a request. User needs Center Admin role at the center to complete the steps below.<br>
15
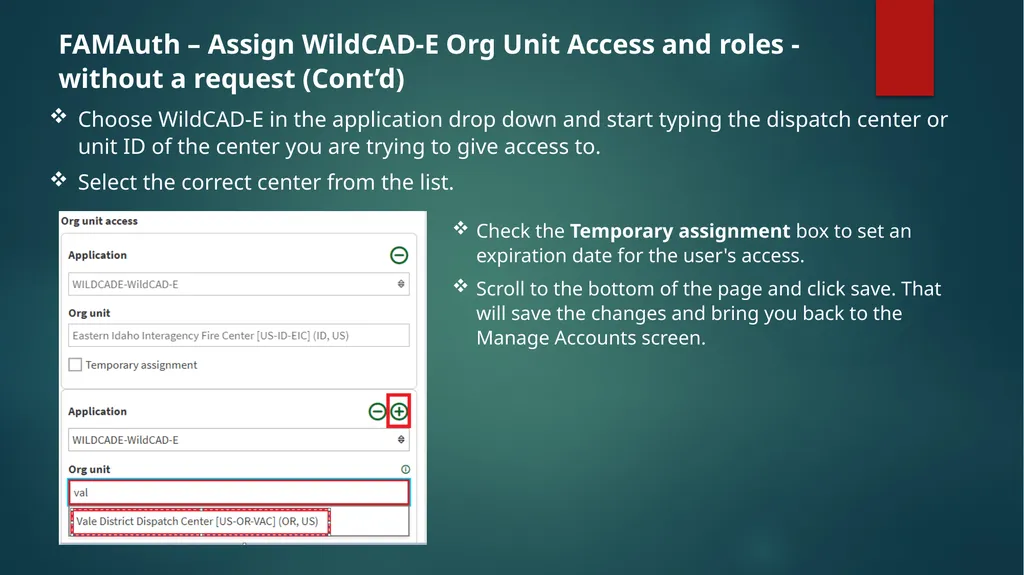
Choose WildCAD-E in the application drop down and start typing the dispatch center or unit ID of the center you are trying to give access to.
Select the correct center from the list. Check the Temporary assignment box to set an expiration date for the user's access.
Scroll to the bottom of the page and click save. That will save the changes and bring you back to the Manage Accounts screen. FAMAuth – Assign WildCAD-E Org Unit Access and roles - without a request (Cont’d)<br>
16
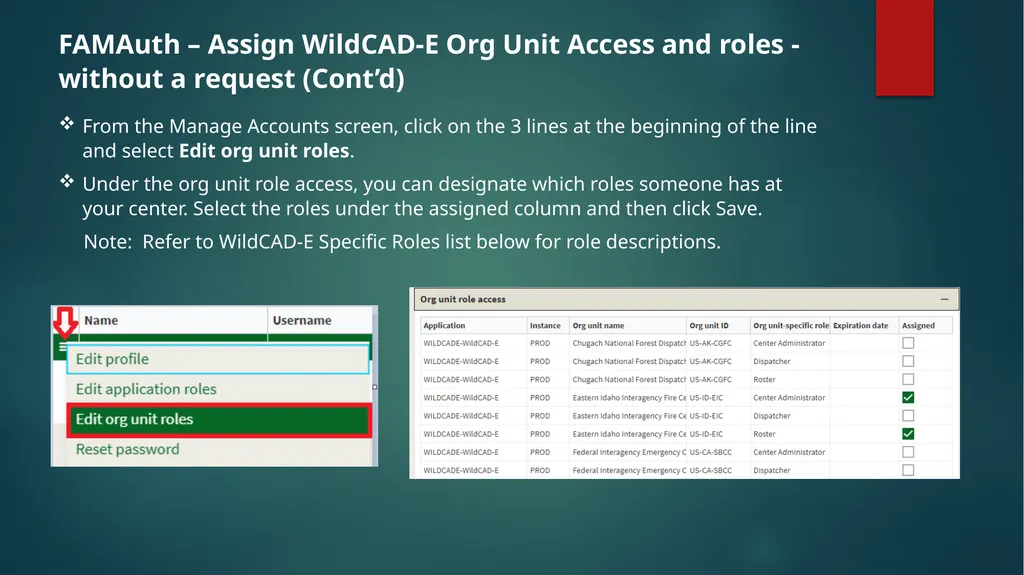
From the Manage Accounts screen, click on the 3 lines at the beginning of the line and select Edit org unit roles.
Under the org unit role access, you can designate which roles someone has at your center. Select the roles under the assigned column and then click Save.
Note: Refer to WildCAD-E Specific Roles list below for role descriptions. FAMAuth – Assign WildCAD-E Org Unit Access and roles - without a request (Cont’d)<br>
17
Center Administrator: Admin access for single designated dispatch center in WildCAD-E and Allows a user to give “org unit” access to other users in iNAP.
Dispatcher: Allows user to complete normal dispatch duties within assigned center.
Notes:
A dispatcher needs either Center Administrator or Dispatcher and Roster, they do not need all three roles.
A resource or FMO type only needs the roster role. FAMAuth - WILDCAD-E SPECIFIC ROLES Roster: Allows user to use roster functionality in WildCAD-E. Users with Center Admin and Dispatcher will need this role in addition to be able to work on rosters within WildCAD-E. This is the role that is needed for resources or fire management to status and roster resources.<br>
18
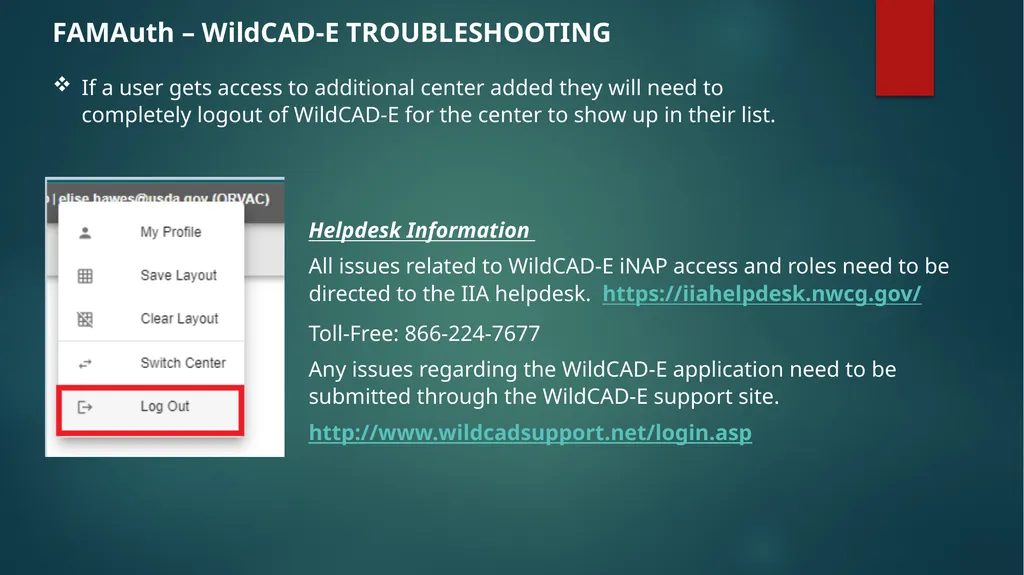
If a user gets access to additional center added they will need to completely logout of WildCAD-E for the center to show up in their list. FAMAuth – WildCAD-E TROUBLESHOOTING Helpdesk Information
All issues related to WildCAD-E iNAP access and roles need to be directed to the IIA helpdesk. https://iiahelpdesk.nwcg.gov/
Toll-Free: 866-224-7677
Any issues regarding the WildCAD-E application need to be submitted through the WildCAD-E support site.
http://www.wildcadsupport.net/login.asp<br>
All issues related to WildCAD-E iNAP access and roles need to be directed to the IIA helpdesk. https://iiahelpdesk.nwcg.gov/
Toll-Free: 866-224-7677
Any issues regarding the WildCAD-E application need to be submitted through the WildCAD-E support site.
http://www.wildcadsupport.net/login.asp<br>
19
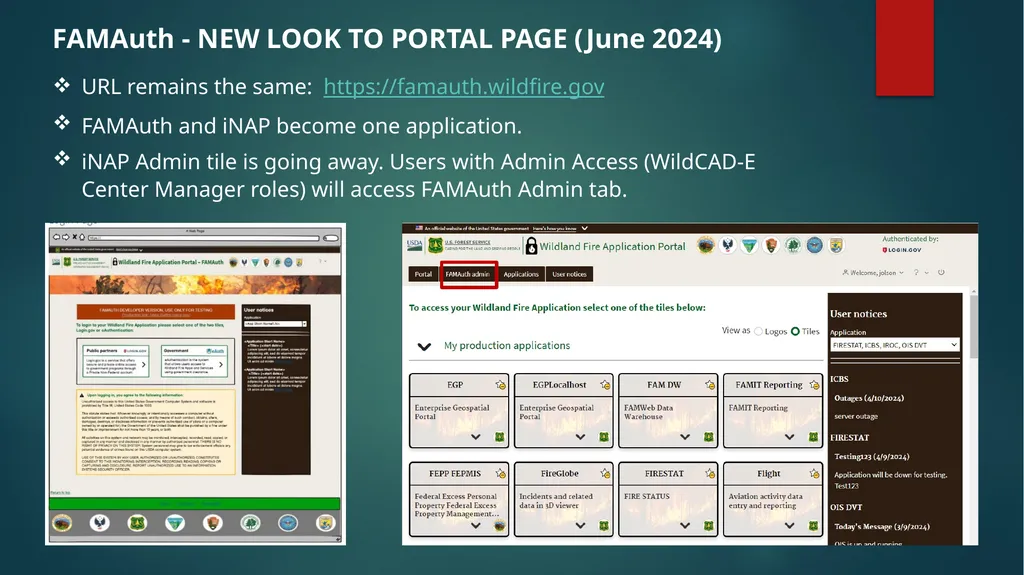
URL remains the same: https://famauth.wildfire.gov
FAMAuth and iNAP become one application.
iNAP Admin tile is going away. Users with Admin Access (WildCAD-E Center Manager roles) will access FAMAuth Admin tab. FAMAuth - NEW LOOK TO PORTAL PAGE (June 2024)<br>
FAMAuth and iNAP become one application.
iNAP Admin tile is going away. Users with Admin Access (WildCAD-E Center Manager roles) will access FAMAuth Admin tab. FAMAuth - NEW LOOK TO PORTAL PAGE (June 2024)<br>