
Overview on the activities of the UN Informal


Description: Overview on the activities of the UN Informal Working Group on Cyber Security and Over-the-air Issues Informal Working Group Cyber Security and Software UpdateOver-the-Air issues Start of activity: 21 December 2016 (kickoff meeting at UK
Related Topics
Download Presentation
"Overview on the activities of the UN Informal" is the property of its rightful owner. Permission is granted to download and print the materials on this website for personal, non-commercial use only, and to display it on your personal computer provided you do not modify the materials and that you retain all copyright notices contained in the materials. By downloading content from our website, you accept the terms of this agreement.
Presentation Transcript
slide1. Overview on the activities of the UN Informal Working Group on Cyber Security and Over-the-air Issues<br>
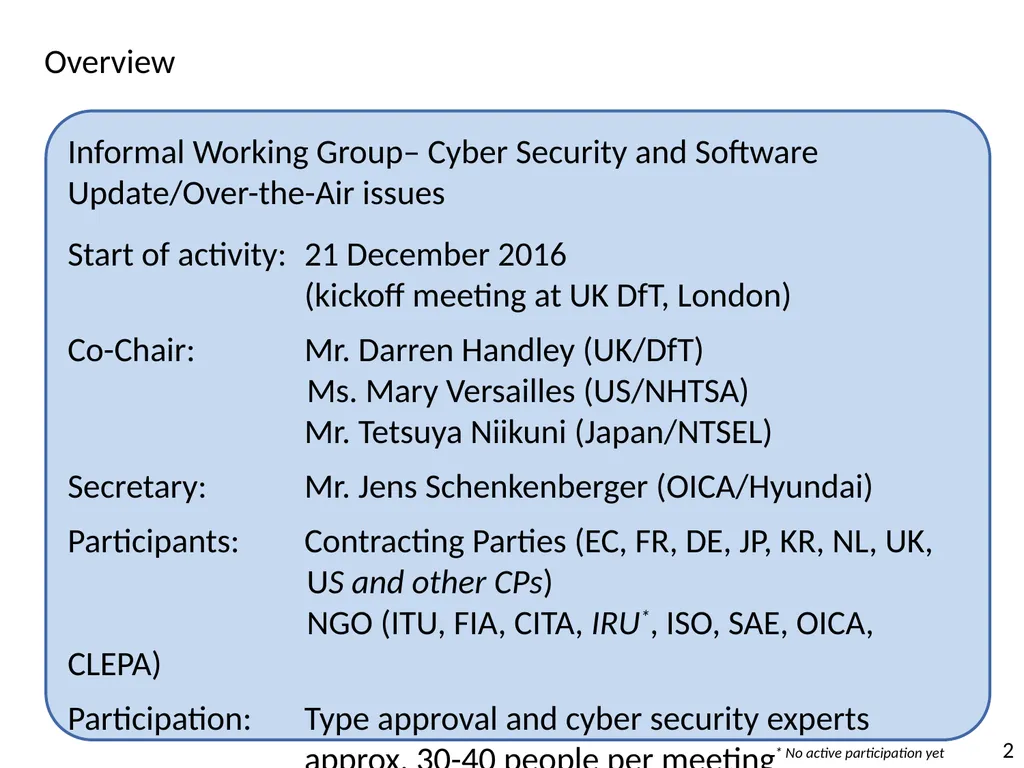
slide2. Informal Working Group– Cyber Security and Software Update/Over-the-Air issues
Start of activity: 21 December 2016 (kickoff meeting at UK DfT, London)
Co-Chair: Mr. Darren Handley (UK/DfT)
Ms. Mary Versailles (US/NHTSA)
Mr. Tetsuya Niikuni (Japan/NTSEL)
Secretary: Mr. Jens Schenkenberger (OICA/Hyundai)
Participants: Contracting Parties (EC, FR, DE, JP, KR, NL, UK,
US and other CPs)
NGO (ITU, FIA, CITA, IRU*, ISO, SAE, OICA, CLEPA)
Participation: Type approval and cyber security experts approx. 30-40 people per meeting Overview * No active participation yet<br>
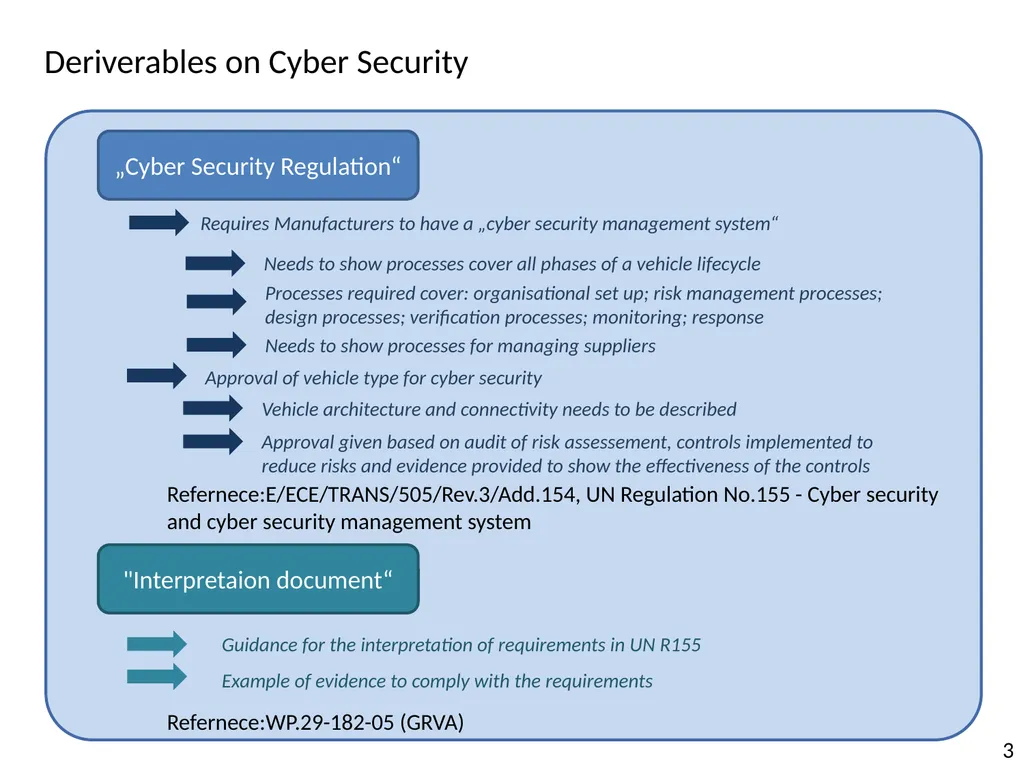
slide3. „Cyber Security Regulation“ Requires Manufacturers to have a „cyber security management system“ Approval of vehicle type for cyber security Deriverables on Cyber Security Needs to show processes cover all phases of a vehicle lifecycle Processes required cover: organisational set up; risk management processes; design processes; verification processes; monitoring; response Needs to show processes for managing suppliers Vehicle architecture and connectivity needs to be described Approval given based on audit of risk assessement, controls implemented to reduce risks and evidence provided to show the effectiveness of the controls Guidance for the interpretation of requirements in UN R155 "Interpretaion document“ Refernece:E/ECE/TRANS/505/Rev.3/Add.154, UN Regulation No.155 - Cyber security and cyber security management system Refernece:WP.29-182-05 (GRVA) Example of evidence to comply with the requirements<br>
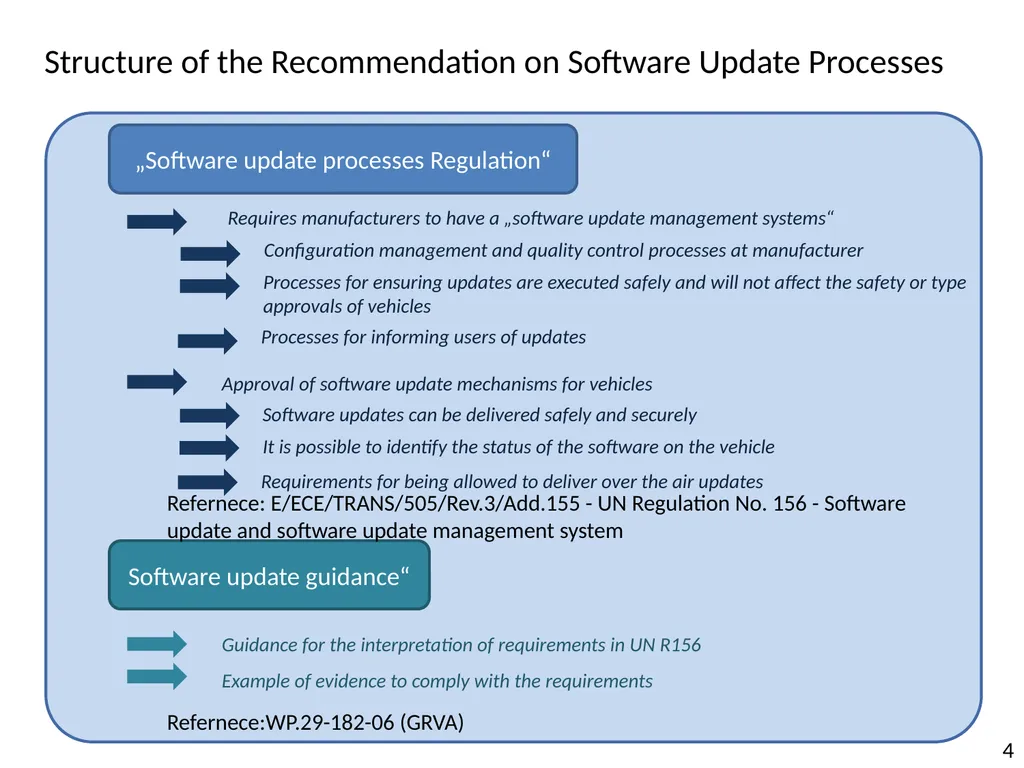
slide4. „Software update processes Regulation“ Requires manufacturers to have a „software update management systems“ Approval of software update mechanisms for vehicles Software update guidance“ Structure of the Recommendation on Software Update Processes Configuration management and quality control processes at manufacturer Processes for ensuring updates are executed safely and will not affect the safety or type approvals of vehicles Processes for informing users of updates Software updates can be delivered safely and securely It is possible to identify the status of the software on the vehicle Requirements for being allowed to deliver over the air updates Guidance for the interpretation of requirements in UN R156 Refernece:WP.29-182-06 (GRVA) Example of evidence to comply with the requirements Refernece: E/ECE/TRANS/505/Rev.3/Add.155 - UN Regulation No. 156 - Software update and software update management system<br>
slide5. The group is developing guidance for Contracting Parties to the 1998 Agreement that they may use when formulating national legislation on cyber security for automotive vehicles and/or legislation regarding software updates and the processes for updating vehicle’s software.
The aim of the guidance is to enable a harmonized approach to the adoption of such legislation for contracting parties to both the 1998 and 1958 Geneva Conventions. Current activity– Development of technical requirement for 98 agreement mumber states<br>
slide6. This approach is suggested as it should enable contracting parties to the 1998 Agreement to formulate national regulation/legislation that is equivalent to UN Regulations Nos. 155 and 156, permitting a harmonised approach.
The guidance lists technical requirements for the vehicle and technical requirements for management systems. The technical requirements for the management systems list requirements that are external to the vehicle but need to be in place to effectively manage the cyber security of a vehicle over its lifecycle and to ensure software updates will be sufficiently appraised and protected before they are sent to a vehicle. Next step – Development of technical requirement for 98 agreement mumber states<br>
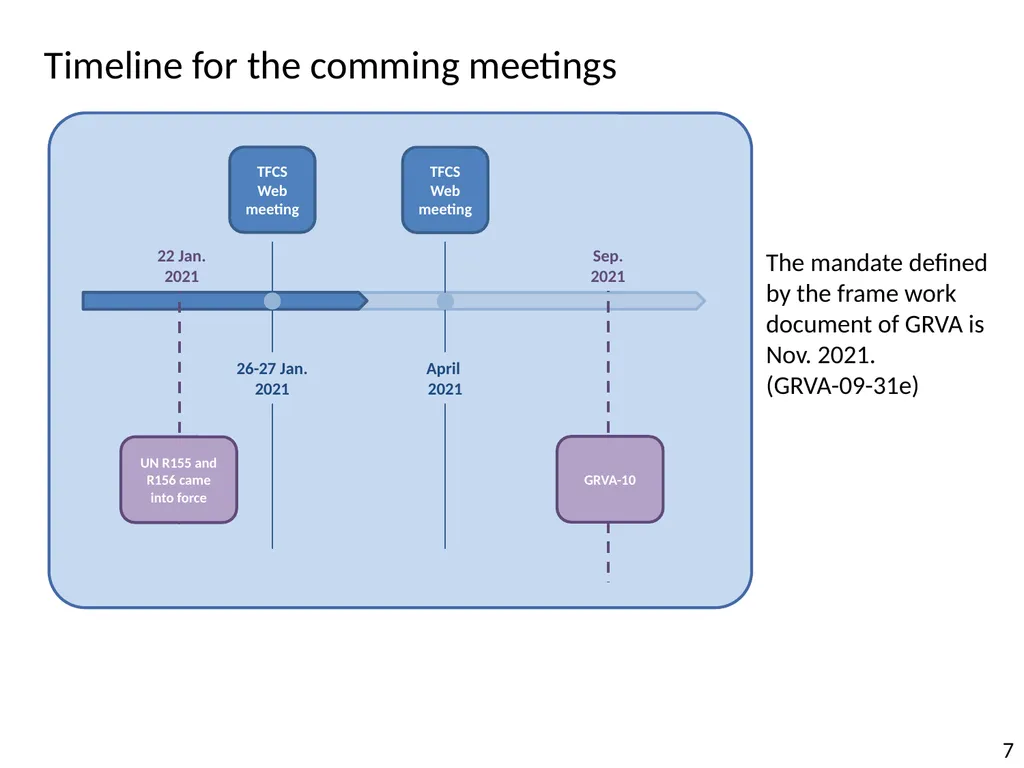
slide7. Timeline for the comming meetings The mandate defined by the frame work document of GRVA is Nov. 2021.
(GRVA-09-31e)<br>
slide8. For more information
UNECE wiki page for the IWG is:
https://wiki.unece.org/pages/viewpage.action?pageId=40829521<br>
slide2. Informal Working Group– Cyber Security and Software Update/Over-the-Air issues
Start of activity: 21 December 2016 (kickoff meeting at UK DfT, London)
Co-Chair: Mr. Darren Handley (UK/DfT)
Ms. Mary Versailles (US/NHTSA)
Mr. Tetsuya Niikuni (Japan/NTSEL)
Secretary: Mr. Jens Schenkenberger (OICA/Hyundai)
Participants: Contracting Parties (EC, FR, DE, JP, KR, NL, UK,
US and other CPs)
NGO (ITU, FIA, CITA, IRU*, ISO, SAE, OICA, CLEPA)
Participation: Type approval and cyber security experts approx. 30-40 people per meeting Overview * No active participation yet<br>
slide3. „Cyber Security Regulation“ Requires Manufacturers to have a „cyber security management system“ Approval of vehicle type for cyber security Deriverables on Cyber Security Needs to show processes cover all phases of a vehicle lifecycle Processes required cover: organisational set up; risk management processes; design processes; verification processes; monitoring; response Needs to show processes for managing suppliers Vehicle architecture and connectivity needs to be described Approval given based on audit of risk assessement, controls implemented to reduce risks and evidence provided to show the effectiveness of the controls Guidance for the interpretation of requirements in UN R155 "Interpretaion document“ Refernece:E/ECE/TRANS/505/Rev.3/Add.154, UN Regulation No.155 - Cyber security and cyber security management system Refernece:WP.29-182-05 (GRVA) Example of evidence to comply with the requirements<br>
slide4. „Software update processes Regulation“ Requires manufacturers to have a „software update management systems“ Approval of software update mechanisms for vehicles Software update guidance“ Structure of the Recommendation on Software Update Processes Configuration management and quality control processes at manufacturer Processes for ensuring updates are executed safely and will not affect the safety or type approvals of vehicles Processes for informing users of updates Software updates can be delivered safely and securely It is possible to identify the status of the software on the vehicle Requirements for being allowed to deliver over the air updates Guidance for the interpretation of requirements in UN R156 Refernece:WP.29-182-06 (GRVA) Example of evidence to comply with the requirements Refernece: E/ECE/TRANS/505/Rev.3/Add.155 - UN Regulation No. 156 - Software update and software update management system<br>
slide5. The group is developing guidance for Contracting Parties to the 1998 Agreement that they may use when formulating national legislation on cyber security for automotive vehicles and/or legislation regarding software updates and the processes for updating vehicle’s software.
The aim of the guidance is to enable a harmonized approach to the adoption of such legislation for contracting parties to both the 1998 and 1958 Geneva Conventions. Current activity– Development of technical requirement for 98 agreement mumber states<br>
slide6. This approach is suggested as it should enable contracting parties to the 1998 Agreement to formulate national regulation/legislation that is equivalent to UN Regulations Nos. 155 and 156, permitting a harmonised approach.
The guidance lists technical requirements for the vehicle and technical requirements for management systems. The technical requirements for the management systems list requirements that are external to the vehicle but need to be in place to effectively manage the cyber security of a vehicle over its lifecycle and to ensure software updates will be sufficiently appraised and protected before they are sent to a vehicle. Next step – Development of technical requirement for 98 agreement mumber states<br>
slide7. Timeline for the comming meetings The mandate defined by the frame work document of GRVA is Nov. 2021.
(GRVA-09-31e)<br>
slide8. For more information
UNECE wiki page for the IWG is:
https://wiki.unece.org/pages/viewpage.action?pageId=40829521<br>