02
A Year in a slide Conferences attended:
Flagship: TCC 2016-B, Eurocrypt 2017.
Domain-specific: TPMPC.
Smaller Meetings: ECRYPT collaborative writing workshop, HEAT, Lattice Meeting (ENS Lyon).
Talks given: TCC 2016-B, Lattice Meeting:
More Efficient Constant-Round Multi-Party Computation from BMR and SHE.
3. Research visits: Thales UK, Bar-Ilan University.
4. Outreach: Digimakers (coming on 11th November, 2017) Eduardo Soria-Vázquez<br>
04
Low Cost Constant Round MPC Combining BMR and Oblivious Transfer Carmit Hazay, Peter Scholl, Eduardo Soria Vázquez
October 11, 2017<br>
05
Overview What is MPC?
Garbled Circuits: 2PC (Yao) vs MPC (BMR)
Results:
A compiler from binary MPC to BMR
Robustness of Garbling in BMR
Optimized Garbling with TinyOT
Conclusion 5 Eduardo Soria-Vázquez<br>
06
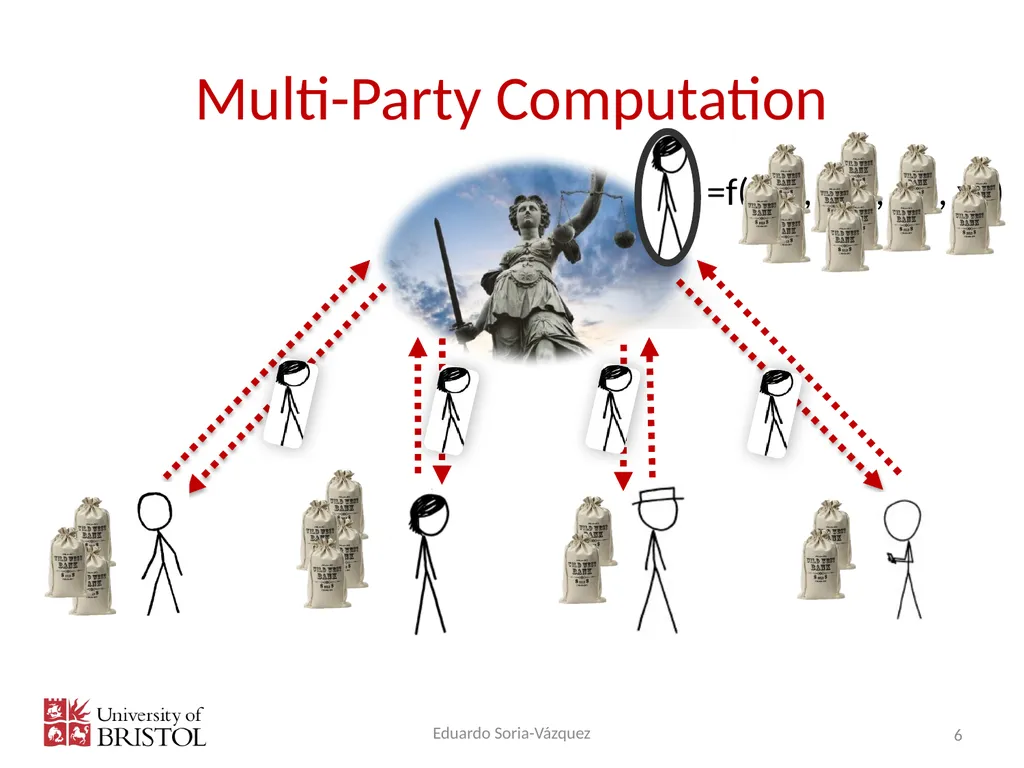
=f( x1 , x2 , x3 , x4 ) Multi-Party Computation Eduardo Soria-Vázquez 6<br>
07
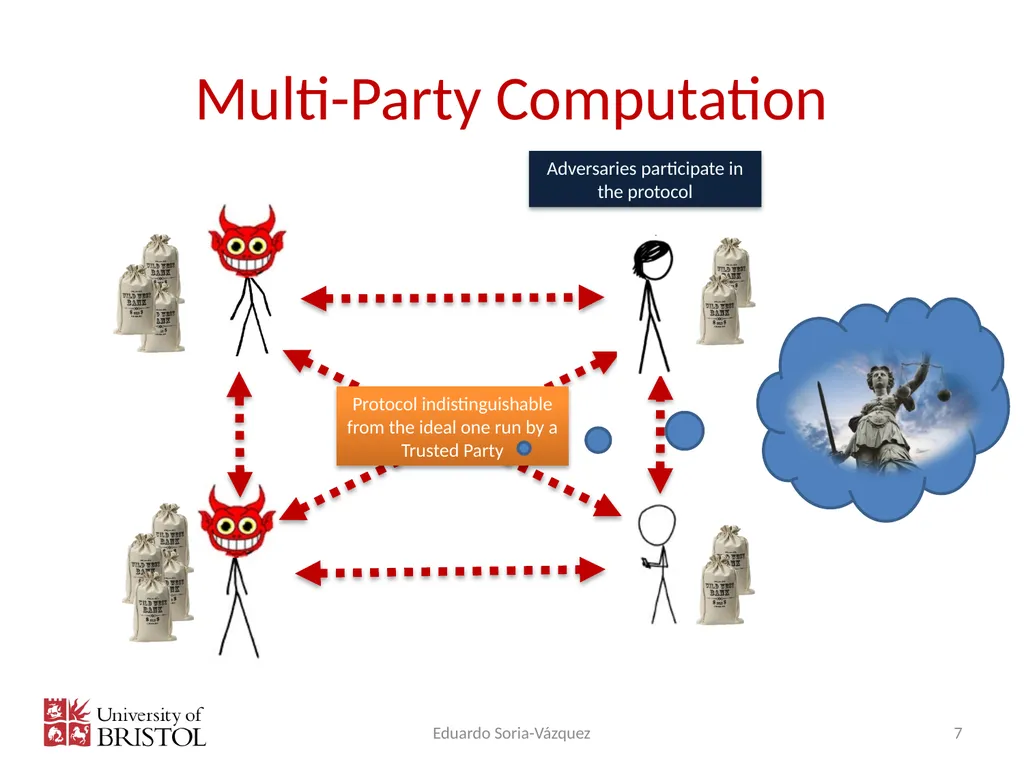
Protocol indistinguishable from the ideal one run by a Trusted Party Adversaries participate in the protocol Multi-Party Computation Eduardo Soria-Vázquez 7<br>
08
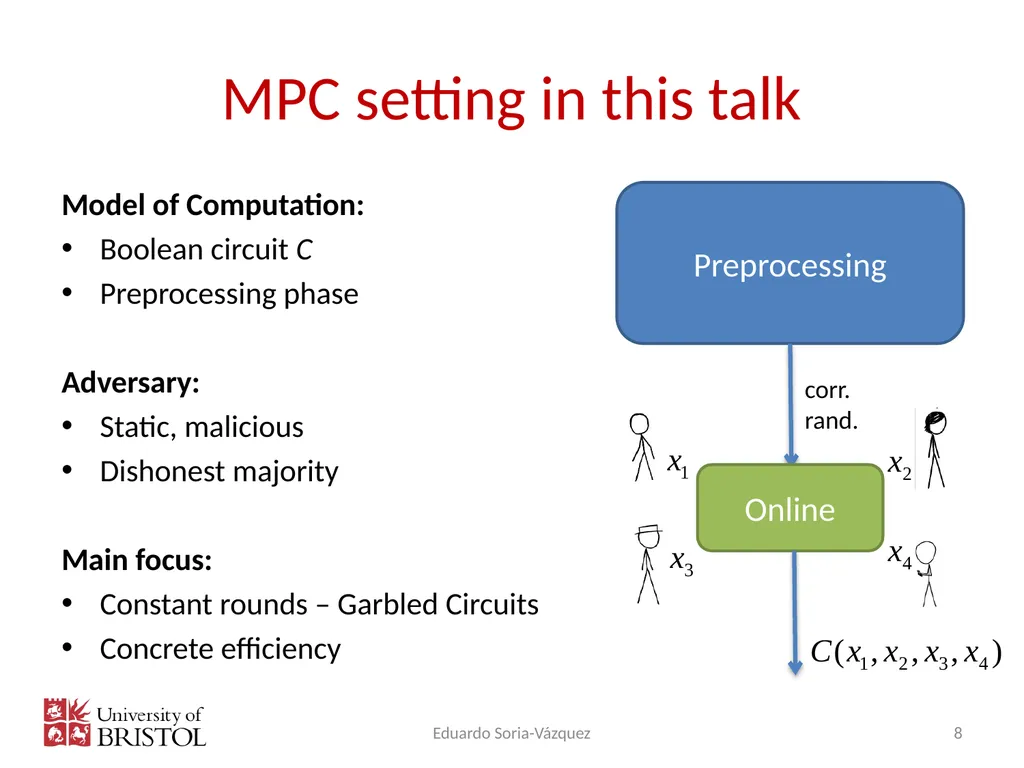
MPC setting in this talk Model of Computation:
Boolean circuit C
Preprocessing phase
Adversary:
Static, malicious
Dishonest majority
Main focus:
Constant rounds – Garbled Circuits
Concrete efficiency Preprocessing Online corr.
rand. 8 Eduardo Soria-Vázquez<br>
09
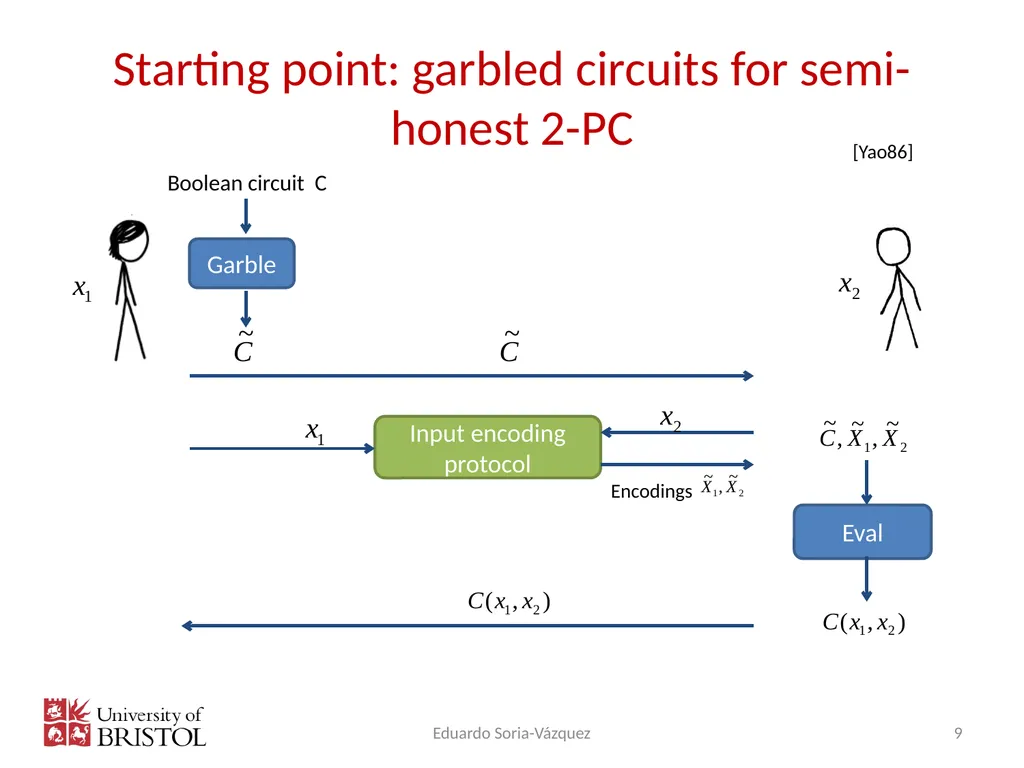
Starting point: garbled circuits for semi-honest 2-PC Boolean circuit C Eduardo Soria-Vázquez 9 Garble Input encoding protocol Eval Encodings [Yao86]<br>
10
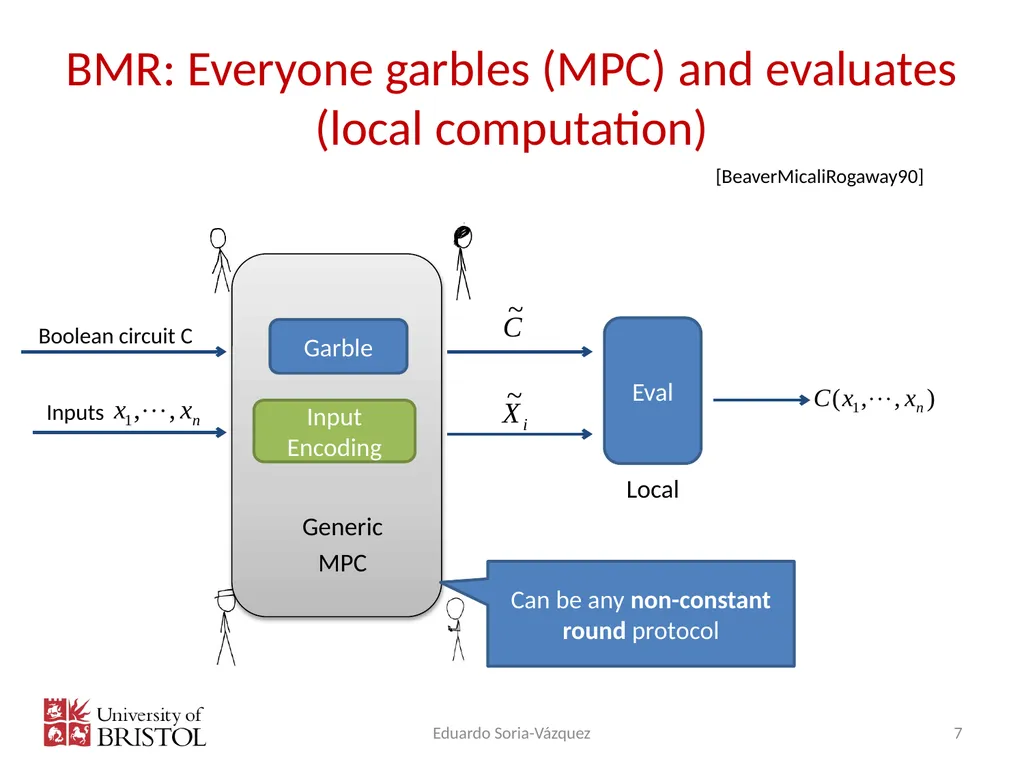
BMR: Everyone garbles (MPC) and evaluates (local computation) Boolean circuit C Eduardo Soria-Vázquez 7 Garble Input Encoding Inputs Eval Generic
MPC [BeaverMicaliRogaway90] Can be any non-constant round protocol Local<br>
11
Challenge in BMR: evaluate Garbling step in MPC, efficiently Eduardo Soria-Vázquez 11<br>
12
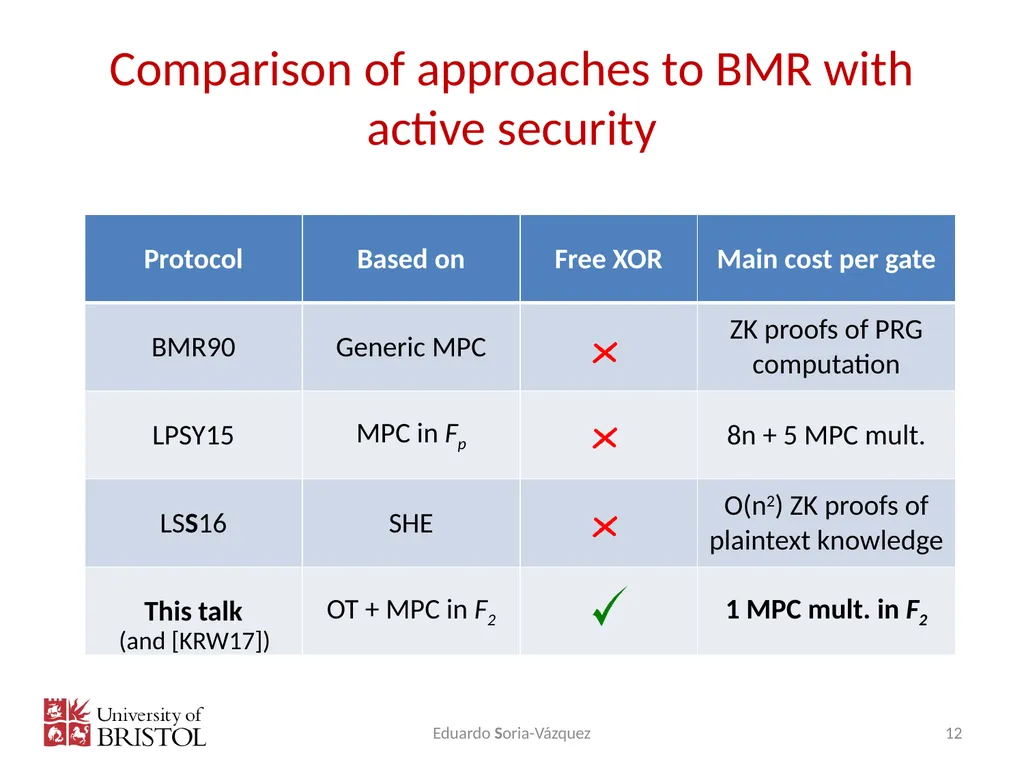
Comparison of approaches to BMR with active security Eduardo Soria-Vázquez 12 (and [KRW17])<br>
13
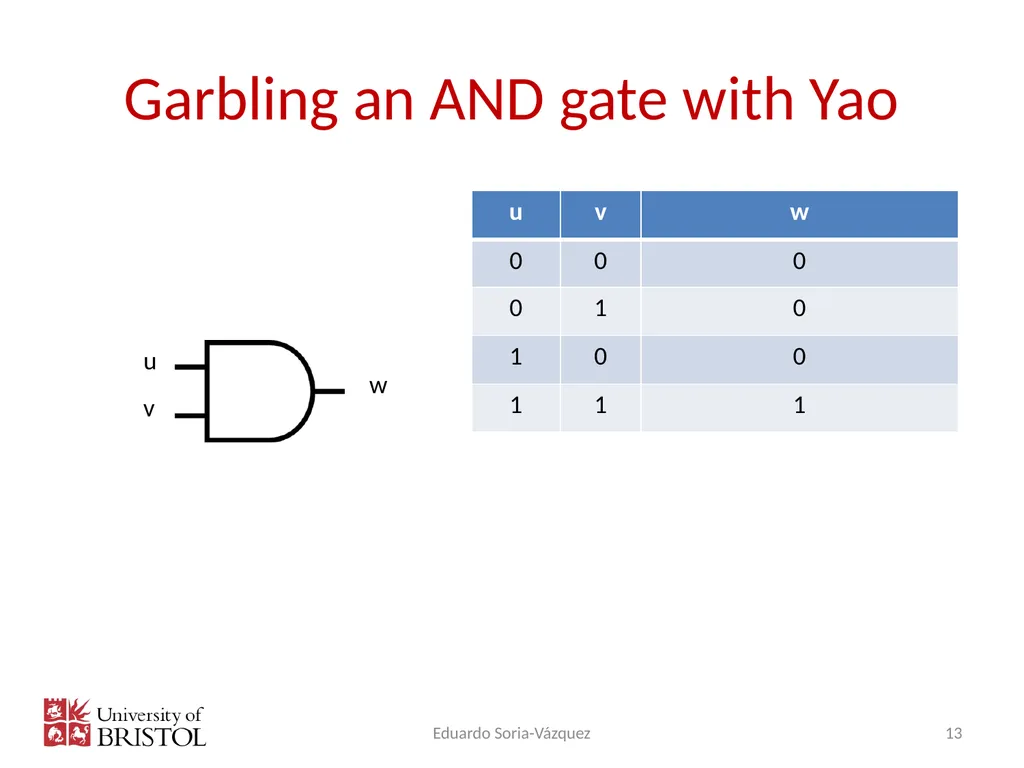
Garbling an AND gate with Yao Eduardo Soria-Vázquez 13 u v w<br>
14
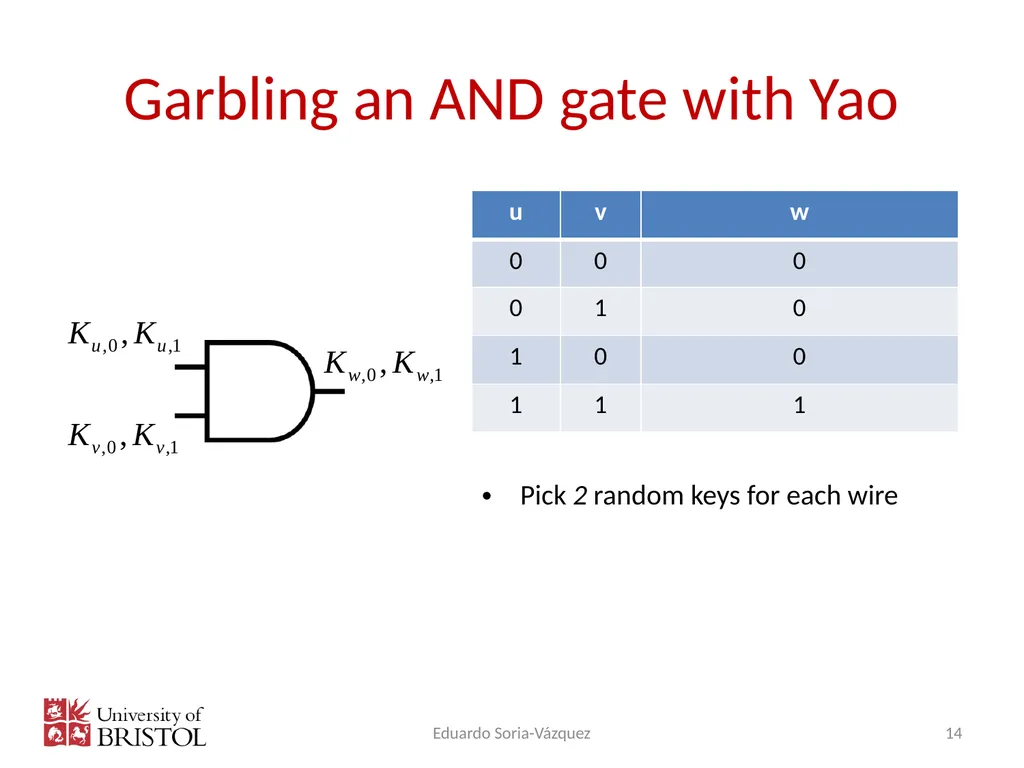
Garbling an AND gate with Yao Eduardo Soria-Vázquez 14 Pick 2 random keys for each wire<br>
15
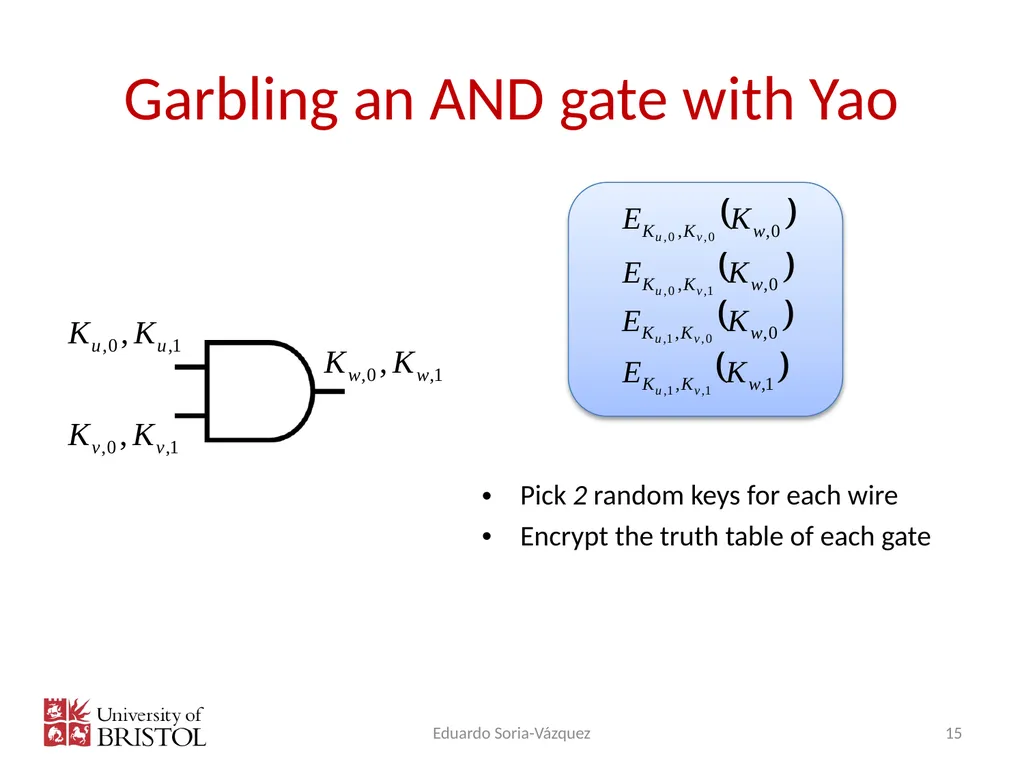
Garbling an AND gate with Yao Eduardo Soria-Vázquez 15 Pick 2 random keys for each wire
Encrypt the truth table of each gate<br>
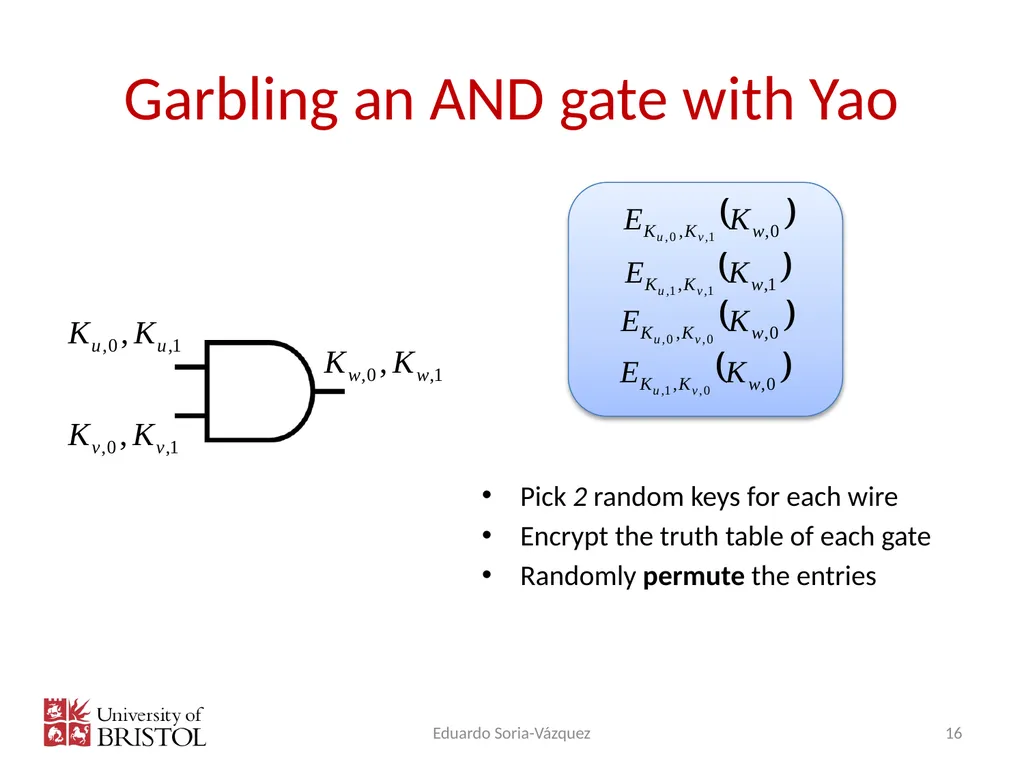
16
Garbling an AND gate with Yao Eduardo Soria-Vázquez 16 Pick 2 random keys for each wire
Encrypt the truth table of each gate
Randomly permute the entries<br>
17
Garbling in BMR Eduardo Soria-Vázquez 17<br>
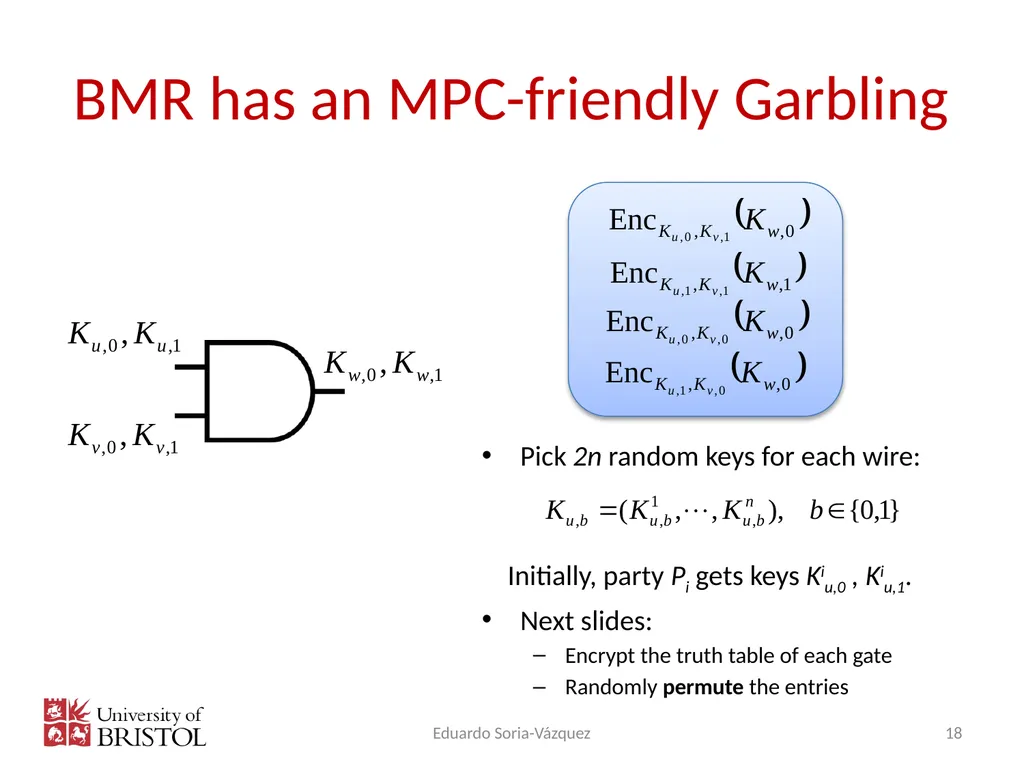
18
BMR has an MPC-friendly Garbling Pick 2n random keys for each wire:
Initially, party Pi gets keys Kiu,0 , Kiu,1.
Next slides:
Encrypt the truth table of each gate
Randomly permute the entries Eduardo Soria-Vázquez 18<br>
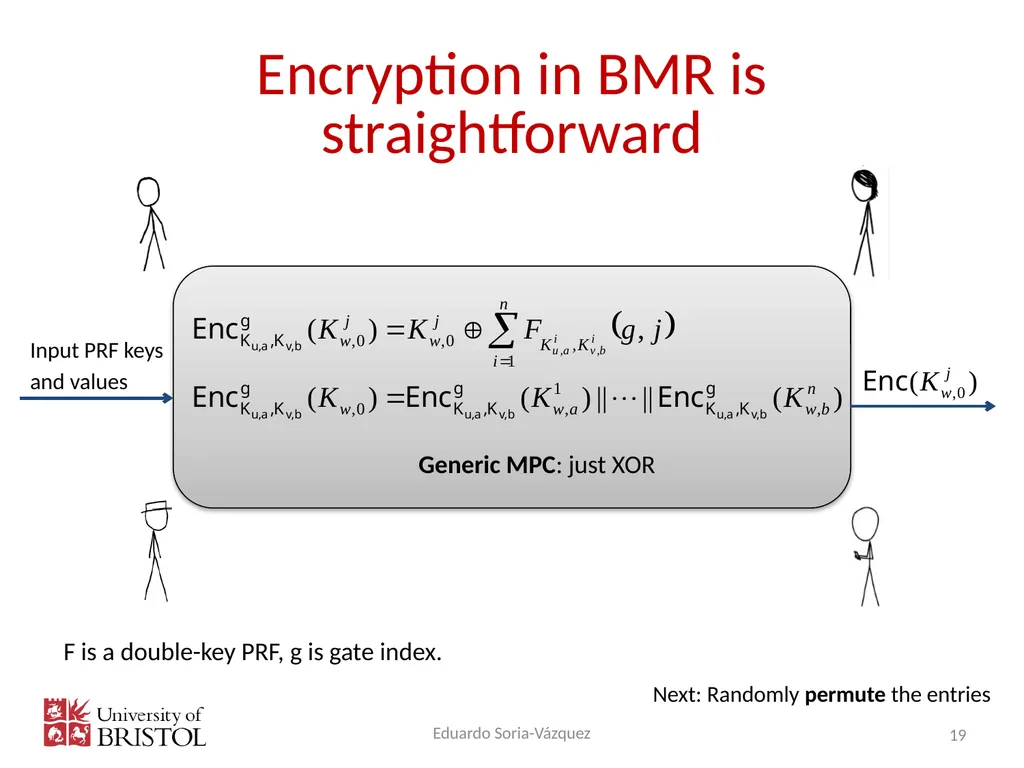
19
Encryption in BMR is straightforward Eduardo Soria-Vázquez 19 Input PRF keys
and values Generic MPC: just XOR F is a double-key PRF, g is gate index. Next: Randomly permute the entries<br>
20
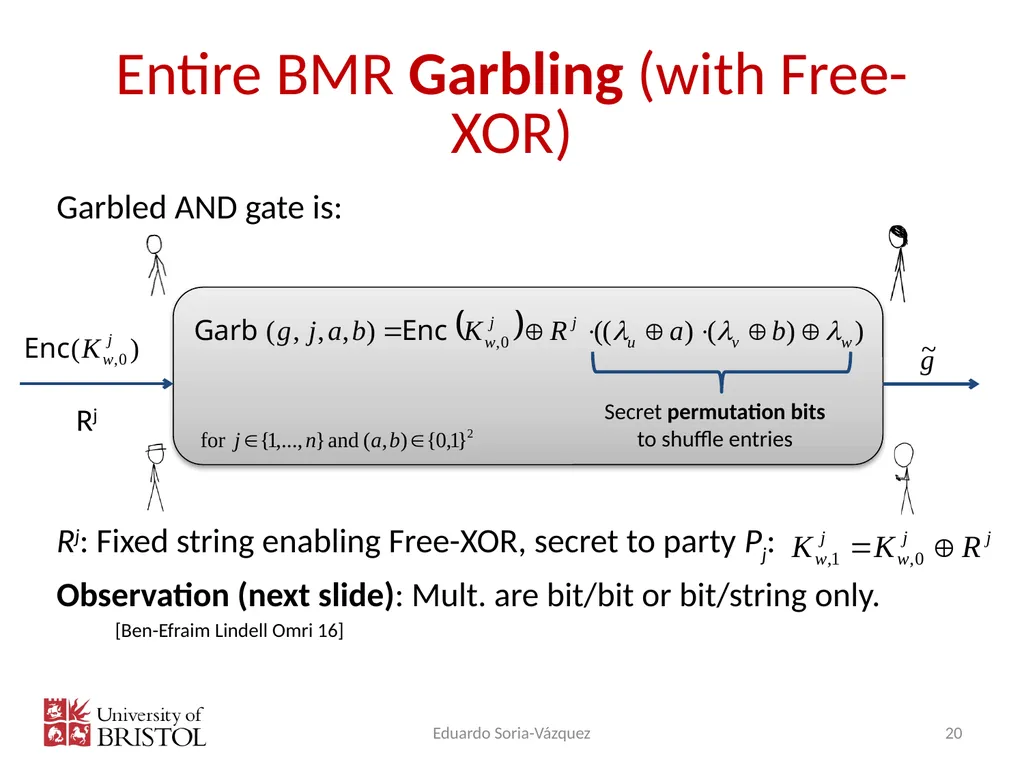
Entire BMR Garbling (with Free-XOR) Garbled AND gate is:
Rj: Fixed string enabling Free-XOR, secret to party Pj:
Observation (next slide): Mult. are bit/bit or bit/string only.
[Ben-Efraim Lindell Omri 16] Eduardo Soria-Vázquez 20 Rj<br>
21
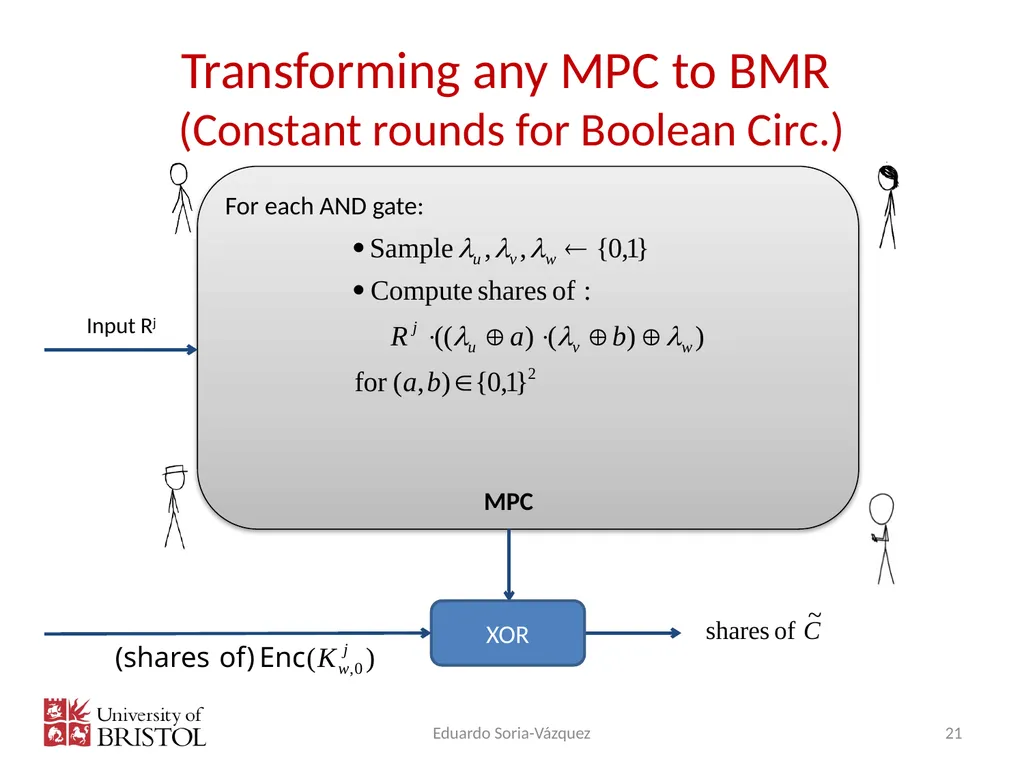
Transforming any MPC to BMR �(Constant rounds for Boolean Circ.) Eduardo Soria-Vázquez 21 For each AND gate: Input Rj MPC XOR<br>
22
Eduardo Soria-Vázquez 22 For each AND gate: Input Rj 1 x F2 mult in MPC n(n-1) COTs for bit/string mult. Consistency
Check XOR Transforming any MPC to BMR �(Constant rounds for Boolean Circ.)<br>
23
Robustness of Garbling in BMR Eduardo Soria-Vázquez 23<br>
24
BMR garbling is very robust to errors Thought experiment with an adversary: Eduardo Soria-Vázquez 24 Garble Encoding Eval<br>
25
BMR garbling is very robust to errors Intuition:
Only possible break is to flip honest Pj‘s masked key:
Negligible (guess Rj) if the mask was obtained from a suitable PRF
We strengthen previous results (proofs) [LPSY15, KRW17]:
Allowed incorrect PRF values, non-adaptively.
Did not directly reduce to PRF security.
Shares of garbling had to be authenticated (less efficient). Eduardo Soria-Vázquez 25<br>
26
An optimized protocol for BMR:�TinyOT Eduardo Soria-Vázquez 26<br>
27
Optimized variant based on TinyOT Multi-party TinyOT protocol [FrederiksenKellerOrsiniScholl15]
Efficient instantiation of binary MPC.
Optimized in [KatzRanellucciWang17]
Uses Correlated OT to create information-theoretic MACs
MAC(x) = K + x R
For shared bit x, and MAC key (K, R)
Fix R to be the global difference in Free-XOR
Bit/string products for free! Eduardo Soria-Vázquez 27<br>
28
Eduardo Soria-Vázquez 28 For each AND gate: Input Rj 1 x F2 mult in MPC n(n-1) COTs for bit/string mult. Consistency
Check XOR Optimized variant based on TinyOT<br>
29
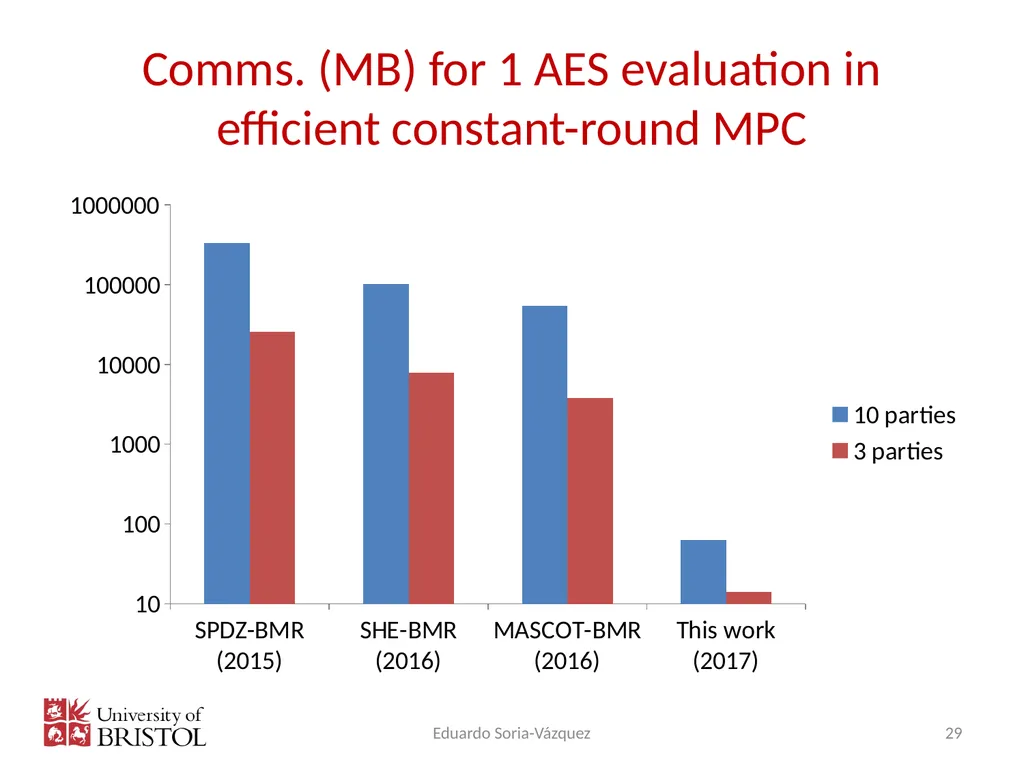
Comms. (MB) for 1 AES evaluation in efficient constant-round MPC 29 Eduardo Soria-Vázquez<br>
30
Conclusion Constant Rounds (Almost) For Free:
Small, O(k) overhead on top of any protocol for binary circuits.
Almost no overhead when using TinyOT.
Improved security proof: Unauthenticated shares, better online.
Open Problems:
Can BMR garbling be optimized? Currently: 4nk bits + O(n2) PRF eval.
How about TinyOT?
Can we further tailor other MPC protocols for BMR garbling? 30 Eduardo Soria-Vázquez<br>
31
Thank you! Eduardo Soria-Vázquez 31 http://ia.cr/2017/214
Low Cost, Constant Round MPC Combining BMR and Oblivious Transfer
Carmit Hazay, Peter Scholl and Eduardo Soria-Vázquez<br>
32
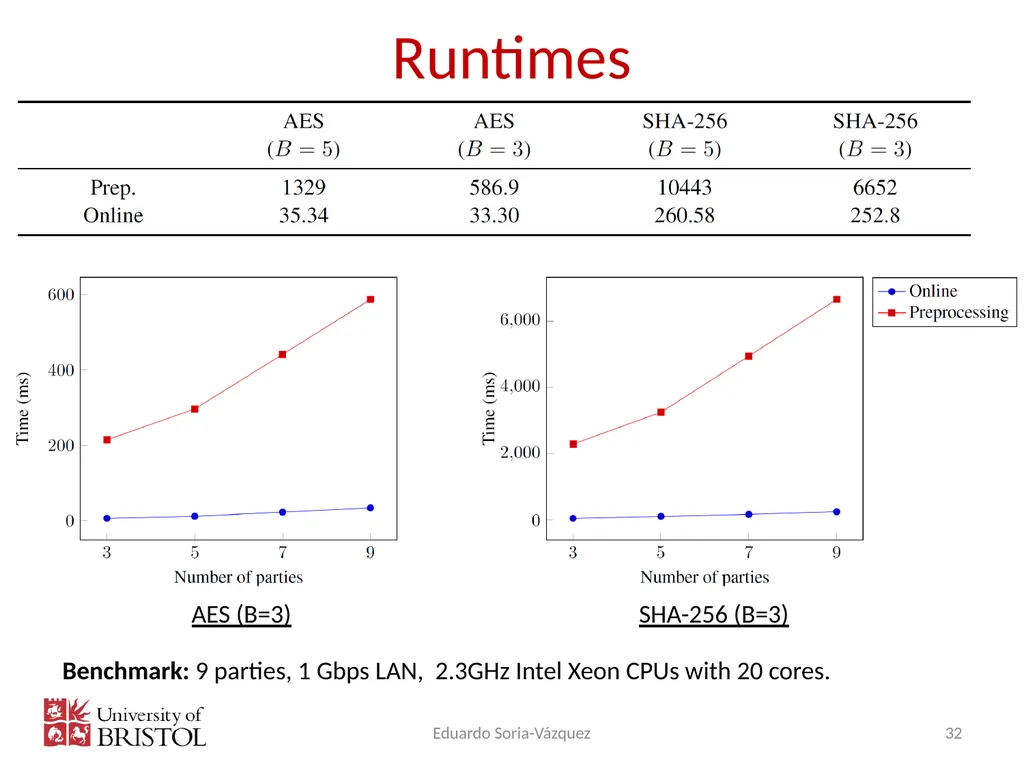
Runtimes Eduardo Soria-Vázquez 32 Benchmark: 9 parties, 1 Gbps LAN, 2.3GHz Intel Xeon CPUs with 20 cores. AES (B=3) SHA-256 (B=3)<br>