
TSA Update David Cooper Surface Policy Division
Description: TSA Update David Cooper Surface Policy Division American Bus Association BISC June 29, 2022 The United States Intelligence Community (IC) Public-Private Talent Exchange (PPTE) Program 2 WHEN: Virtual Industry Day on June 21, 2022, 1:00 pm
Related Topics
Download Presentation
"TSA Update David Cooper Surface Policy Division" is the property of its rightful owner. Permission is granted to download and print the materials on this website for personal, non-commercial use only, and to display it on your personal computer provided you do not modify the materials and that you retain all copyright notices contained in the materials. By downloading content from our website, you accept the terms of this agreement.
Presentation Transcript
slide1. TSA Update
David Cooper
Surface Policy Division American Bus Association / BISC
June 29, 2022<br>
slide2. The United States Intelligence Community (IC) Public-Private Talent Exchange (PPTE) Program 2 WHEN: Virtual Industry Day on June 21, 2022, 1:00 pm – 2:00 pm EDT
GOAL: Create partnerships between the IC and private sector partners.
WHAT: For the 2022 inaugural ore meaningful and productive opportunities for building expertise, sharing business processes, and expanding effort, government and industry partners will collaborate in the following critical focus areas:
• Artificial Intelligence
• Data Management
• Economic Security and Financial Intelligence
Human Capital
Space
During IC PPTE Industry Day, attendees will be provided with an overview of the program followed by a description of each focus area presented by the area champion.
If you would like to participate in this important endeavor, please register here or connect to the following link at https://icsurvey.dni.gov/index.php/488118?lang=en, to register for the event. You can connect with us via email at IC_PPTE@odni.gov for more information.<br>
slide3. In partnership with Chicago Police Department’s Crime Prevention and Information Center (CPIC), the Cybersecurity and Infrastructure Security Agency (CISA) developed the Vehicle Ramming Self-Assessment Tool to assist federal, state, and local law enforcement agencies, as well as critical infrastructure owners and operators inform planning considerations and protective measures associated with mitigating risk against a vehicle-ramming method of attack.
Throughout the tool, helpful resources and references are noted. Users may further examine those resources online at cisa.gov/vehicle-ramming-attack-mitigation under the dropdown feature titled "Self-Assessment Tool Resources." CISA Launches a Vehicle Ramming Self-Assessment Tool 3<br>
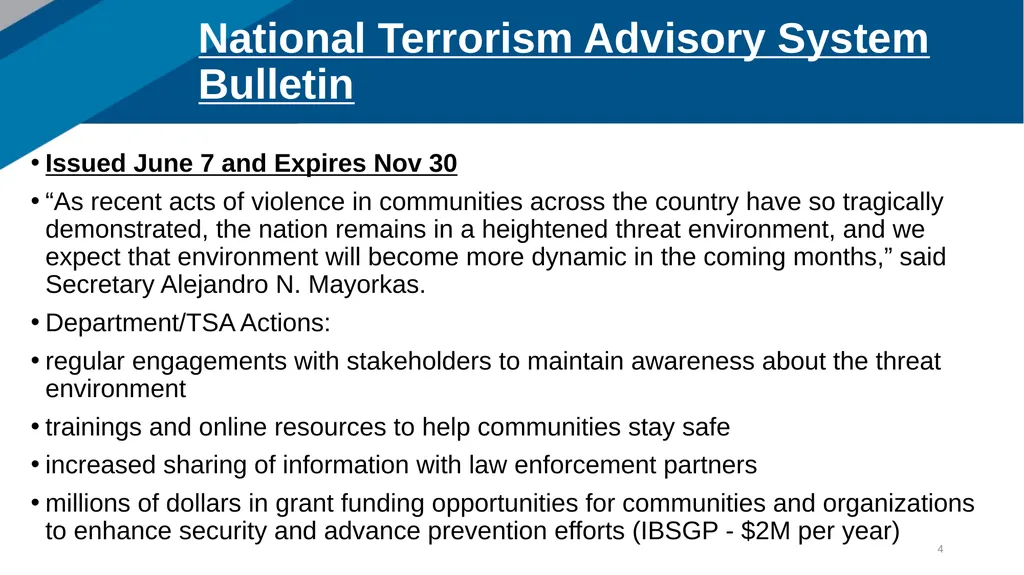
slide4. Issued June 7 and Expires Nov 30
“As recent acts of violence in communities across the country have so tragically demonstrated, the nation remains in a heightened threat environment, and we expect that environment will become more dynamic in the coming months,” said Secretary Alejandro N. Mayorkas.
Department/TSA Actions:
regular engagements with stakeholders to maintain awareness about the threat environment
trainings and online resources to help communities stay safe
increased sharing of information with law enforcement partners
millions of dollars in grant funding opportunities for communities and organizations to enhance security and advance prevention efforts (IBSGP - $2M per year) National Terrorism Advisory System Bulletin 4<br>
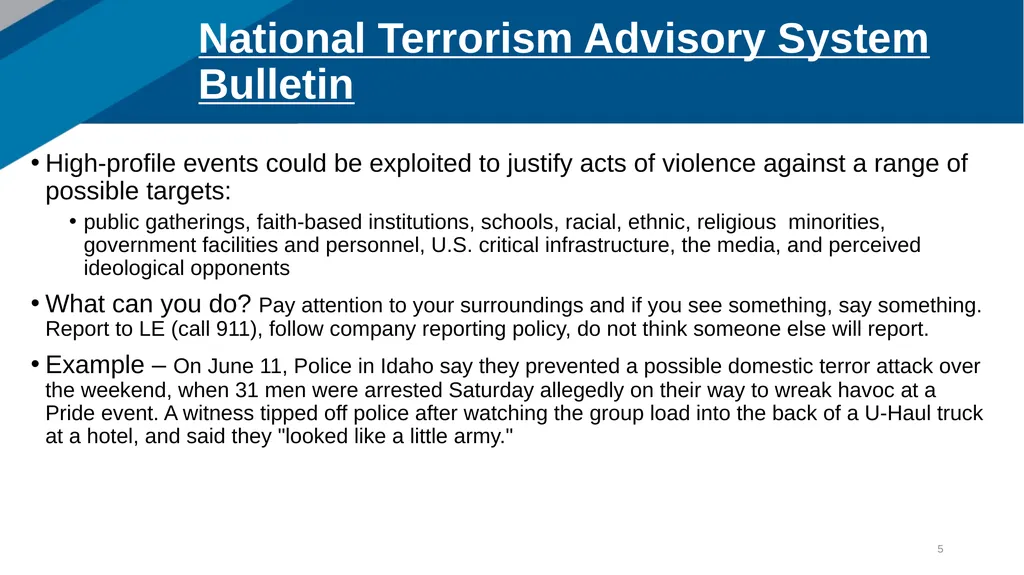
slide5. High-profile events could be exploited to justify acts of violence against a range of possible targets:
public gatherings, faith-based institutions, schools, racial, ethnic, religious minorities, government facilities and personnel, U.S. critical infrastructure, the media, and perceived ideological opponents
What can you do? Pay attention to your surroundings and if you see something, say something. Report to LE (call 911), follow company reporting policy, do not think someone else will report.
Example – On June 11, Police in Idaho say they prevented a possible domestic terror attack over the weekend, when 31 men were arrested Saturday allegedly on their way to wreak havoc at a Pride event. A witness tipped off police after watching the group load into the back of a U-Haul truck at a hotel, and said they "looked like a little army." National Terrorism Advisory System Bulletin 5<br>
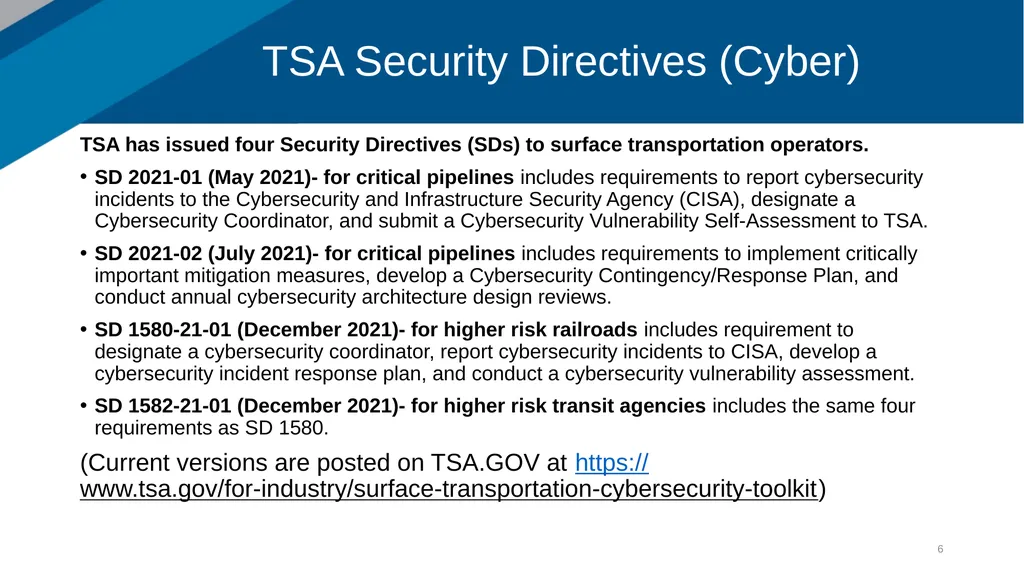
slide6. TSA has issued four Security Directives (SDs) to surface transportation operators.
SD 2021-01 (May 2021)- for critical pipelines includes requirements to report cybersecurity incidents to the Cybersecurity and Infrastructure Security Agency (CISA), designate a Cybersecurity Coordinator, and submit a Cybersecurity Vulnerability Self-Assessment to TSA.
SD 2021-02 (July 2021)- for critical pipelines includes requirements to implement critically important mitigation measures, develop a Cybersecurity Contingency/Response Plan, and conduct annual cybersecurity architecture design reviews.
SD 1580-21-01 (December 2021)- for higher risk railroads includes requirement to designate a cybersecurity coordinator, report cybersecurity incidents to CISA, develop a cybersecurity incident response plan, and conduct a cybersecurity vulnerability assessment.
SD 1582-21-01 (December 2021)- for higher risk transit agencies includes the same four requirements as SD 1580.
(Current versions are posted on TSA.GOV at https://www.tsa.gov/for-industry/surface-transportation-cybersecurity-toolkit) TSA Security Directives (Cyber) 6<br>
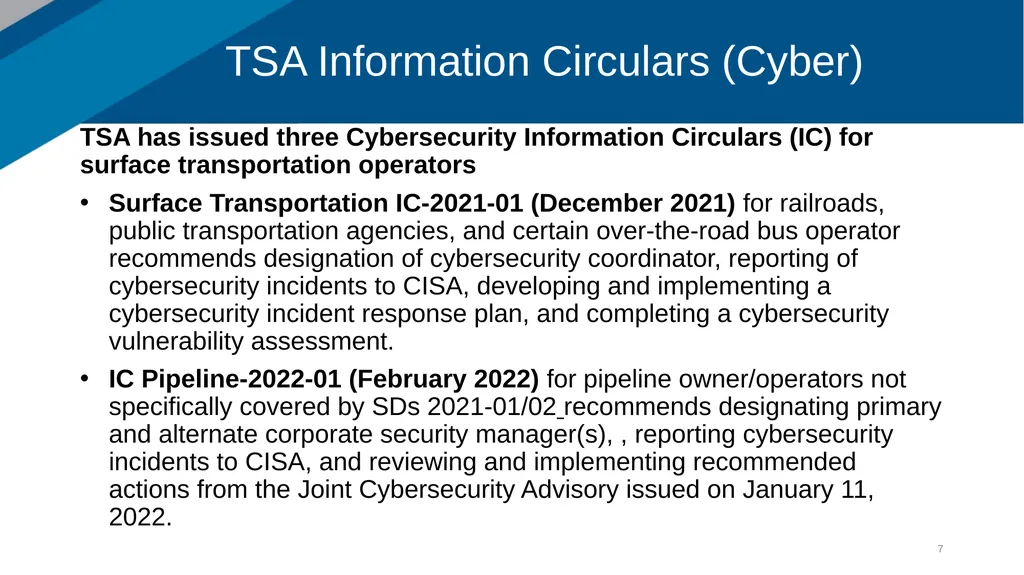
slide7. TSA has issued three Cybersecurity Information Circulars (IC) for surface transportation operators
Surface Transportation IC-2021-01 (December 2021) for railroads, public transportation agencies, and certain over-the-road bus operator recommends designation of cybersecurity coordinator, reporting of cybersecurity incidents to CISA, developing and implementing a cybersecurity incident response plan, and completing a cybersecurity vulnerability assessment.
IC Pipeline-2022-01 (February 2022) for pipeline owner/operators not specifically covered by SDs 2021-01/02 recommends designating primary and alternate corporate security manager(s), , reporting cybersecurity incidents to CISA, and reviewing and implementing recommended actions from the Joint Cybersecurity Advisory issued on January 11, 2022. TSA Information Circulars (Cyber) 7<br>
slide8. TSA has issued three Cybersecurity Information Circulars (IC) for surface transportation operators
Surface Transportation IC-2022-01 (February 2022) for railroads, public transportation agencies, and certain over-the-road bus operator recommended reviewing and implementing the recommended actions in the Joint Cybersecurity Alert, Understanding and Mitigating Russian State-Sponsored Cyber Threats to U.S. Critical Infrastructure and the Cybersecurity and Infrastructure Security Agency’s “Shields Up” site.
Surface Transportation IC-2022-02 (March 2022) for railroads, public transportation agencies, rail transit agencies, pipelines, and certain over-the-road bus operators recommended reviewing and implementing the recommended actions in two Joint Cybersecurity Advisories issued on March 15 “Russian State Actors” (AA2-074A) and on March 17 “Strengthening Cybersecurity of SATCOM Network providers and customers” (AA22-076A) TSA Information Circulars (Cyber) cont. 8<br>
slide9. Issue SD2C for pipelines with revised requirements that are performance based and will allow for flexibility in implementation.
Issue before current SD expires on 7/26/2022
Issue other SDs/ICs
Issue “Advanced Notice of Proposed Rulemaking” on pipeline cybersecurity risk management programs
Coordinate with DHS Policy and other components on the development of cybersecurity standards and regulations. Future Cyber Policy 9<br>
slide10. CISA.gov/shields-up
Latest Updates
Guidance for All Organizations
Recommendations for Corporate Leaders and CEOs
Ransomware Response
Steps You Can Take to Protect Yourself and Your Family
Additional Resources
TSA Regional POCs MAP
TSA Sec Training Rule (Fixed-route)
TSA Threat Assessment Bill to combine TWIC, HMC, Pre-check, etc. Security Initiatives and Resources 10<br>
slide11. What do you do if you recognize something/someone suspicious? Imminent threat?
Lastly, as mentioned above with the Idaho example, the Motorcoach industry also serves as our frontline of defense against those that may try to carry out attacks as described in the NTAS Bulletin. If you see something please don’t hesitate to report it. Follow company procedures or report to LE through 911 for imminent threats.
Think about what looks normal to you through all of your experience. In Idaho, a bunch of people in militant clothes with military style gear loading into a U-Haul truck didn’t look normal and if that person would not have reported what they saw then who knows what would have happened. If you end up with customers on your bus that for whatever reason seem suspicious or you hear something suspicious en-route, have a plan (i.e. a way to call it in to company/dispatch so they can notify LE, a plan to pull over bus due to mechanical that alerts (code) company/dispatch to notify LE, notify company/dispatch or LE after dropping off customers). The worst possible thing is to do nothing. Security Initiatives and Resources cont. 11<br>
June 29, 2022<br>
slide2. The United States Intelligence Community (IC) Public-Private Talent Exchange (PPTE) Program 2 WHEN: Virtual Industry Day on June 21, 2022, 1:00 pm – 2:00 pm EDT
GOAL: Create partnerships between the IC and private sector partners.
WHAT: For the 2022 inaugural ore meaningful and productive opportunities for building expertise, sharing business processes, and expanding effort, government and industry partners will collaborate in the following critical focus areas:
• Artificial Intelligence
• Data Management
• Economic Security and Financial Intelligence
Human Capital
Space
During IC PPTE Industry Day, attendees will be provided with an overview of the program followed by a description of each focus area presented by the area champion.
If you would like to participate in this important endeavor, please register here or connect to the following link at https://icsurvey.dni.gov/index.php/488118?lang=en, to register for the event. You can connect with us via email at IC_PPTE@odni.gov for more information.<br>
slide3. In partnership with Chicago Police Department’s Crime Prevention and Information Center (CPIC), the Cybersecurity and Infrastructure Security Agency (CISA) developed the Vehicle Ramming Self-Assessment Tool to assist federal, state, and local law enforcement agencies, as well as critical infrastructure owners and operators inform planning considerations and protective measures associated with mitigating risk against a vehicle-ramming method of attack.
Throughout the tool, helpful resources and references are noted. Users may further examine those resources online at cisa.gov/vehicle-ramming-attack-mitigation under the dropdown feature titled "Self-Assessment Tool Resources." CISA Launches a Vehicle Ramming Self-Assessment Tool 3<br>
slide4. Issued June 7 and Expires Nov 30
“As recent acts of violence in communities across the country have so tragically demonstrated, the nation remains in a heightened threat environment, and we expect that environment will become more dynamic in the coming months,” said Secretary Alejandro N. Mayorkas.
Department/TSA Actions:
regular engagements with stakeholders to maintain awareness about the threat environment
trainings and online resources to help communities stay safe
increased sharing of information with law enforcement partners
millions of dollars in grant funding opportunities for communities and organizations to enhance security and advance prevention efforts (IBSGP - $2M per year) National Terrorism Advisory System Bulletin 4<br>
slide5. High-profile events could be exploited to justify acts of violence against a range of possible targets:
public gatherings, faith-based institutions, schools, racial, ethnic, religious minorities, government facilities and personnel, U.S. critical infrastructure, the media, and perceived ideological opponents
What can you do? Pay attention to your surroundings and if you see something, say something. Report to LE (call 911), follow company reporting policy, do not think someone else will report.
Example – On June 11, Police in Idaho say they prevented a possible domestic terror attack over the weekend, when 31 men were arrested Saturday allegedly on their way to wreak havoc at a Pride event. A witness tipped off police after watching the group load into the back of a U-Haul truck at a hotel, and said they "looked like a little army." National Terrorism Advisory System Bulletin 5<br>
slide6. TSA has issued four Security Directives (SDs) to surface transportation operators.
SD 2021-01 (May 2021)- for critical pipelines includes requirements to report cybersecurity incidents to the Cybersecurity and Infrastructure Security Agency (CISA), designate a Cybersecurity Coordinator, and submit a Cybersecurity Vulnerability Self-Assessment to TSA.
SD 2021-02 (July 2021)- for critical pipelines includes requirements to implement critically important mitigation measures, develop a Cybersecurity Contingency/Response Plan, and conduct annual cybersecurity architecture design reviews.
SD 1580-21-01 (December 2021)- for higher risk railroads includes requirement to designate a cybersecurity coordinator, report cybersecurity incidents to CISA, develop a cybersecurity incident response plan, and conduct a cybersecurity vulnerability assessment.
SD 1582-21-01 (December 2021)- for higher risk transit agencies includes the same four requirements as SD 1580.
(Current versions are posted on TSA.GOV at https://www.tsa.gov/for-industry/surface-transportation-cybersecurity-toolkit) TSA Security Directives (Cyber) 6<br>
slide7. TSA has issued three Cybersecurity Information Circulars (IC) for surface transportation operators
Surface Transportation IC-2021-01 (December 2021) for railroads, public transportation agencies, and certain over-the-road bus operator recommends designation of cybersecurity coordinator, reporting of cybersecurity incidents to CISA, developing and implementing a cybersecurity incident response plan, and completing a cybersecurity vulnerability assessment.
IC Pipeline-2022-01 (February 2022) for pipeline owner/operators not specifically covered by SDs 2021-01/02 recommends designating primary and alternate corporate security manager(s), , reporting cybersecurity incidents to CISA, and reviewing and implementing recommended actions from the Joint Cybersecurity Advisory issued on January 11, 2022. TSA Information Circulars (Cyber) 7<br>
slide8. TSA has issued three Cybersecurity Information Circulars (IC) for surface transportation operators
Surface Transportation IC-2022-01 (February 2022) for railroads, public transportation agencies, and certain over-the-road bus operator recommended reviewing and implementing the recommended actions in the Joint Cybersecurity Alert, Understanding and Mitigating Russian State-Sponsored Cyber Threats to U.S. Critical Infrastructure and the Cybersecurity and Infrastructure Security Agency’s “Shields Up” site.
Surface Transportation IC-2022-02 (March 2022) for railroads, public transportation agencies, rail transit agencies, pipelines, and certain over-the-road bus operators recommended reviewing and implementing the recommended actions in two Joint Cybersecurity Advisories issued on March 15 “Russian State Actors” (AA2-074A) and on March 17 “Strengthening Cybersecurity of SATCOM Network providers and customers” (AA22-076A) TSA Information Circulars (Cyber) cont. 8<br>
slide9. Issue SD2C for pipelines with revised requirements that are performance based and will allow for flexibility in implementation.
Issue before current SD expires on 7/26/2022
Issue other SDs/ICs
Issue “Advanced Notice of Proposed Rulemaking” on pipeline cybersecurity risk management programs
Coordinate with DHS Policy and other components on the development of cybersecurity standards and regulations. Future Cyber Policy 9<br>
slide10. CISA.gov/shields-up
Latest Updates
Guidance for All Organizations
Recommendations for Corporate Leaders and CEOs
Ransomware Response
Steps You Can Take to Protect Yourself and Your Family
Additional Resources
TSA Regional POCs MAP
TSA Sec Training Rule (Fixed-route)
TSA Threat Assessment Bill to combine TWIC, HMC, Pre-check, etc. Security Initiatives and Resources 10<br>
slide11. What do you do if you recognize something/someone suspicious? Imminent threat?
Lastly, as mentioned above with the Idaho example, the Motorcoach industry also serves as our frontline of defense against those that may try to carry out attacks as described in the NTAS Bulletin. If you see something please don’t hesitate to report it. Follow company procedures or report to LE through 911 for imminent threats.
Think about what looks normal to you through all of your experience. In Idaho, a bunch of people in militant clothes with military style gear loading into a U-Haul truck didn’t look normal and if that person would not have reported what they saw then who knows what would have happened. If you end up with customers on your bus that for whatever reason seem suspicious or you hear something suspicious en-route, have a plan (i.e. a way to call it in to company/dispatch so they can notify LE, a plan to pull over bus due to mechanical that alerts (code) company/dispatch to notify LE, notify company/dispatch or LE after dropping off customers). The worst possible thing is to do nothing. Security Initiatives and Resources cont. 11<br>