"AGENTCON JAPAN Aksh Stop Giving Agents Tokens" is the property of its rightful owner. Permission is granted to
download and print the materials on this website for personal, non-commercial use only, and to display it
on your personal computer provided you do not modify the materials and that you retain all copyright
notices contained in the materials. By downloading content from our website, you accept the terms of this
agreement.
Presentation Transcript
01
AGENTCON JAPAN Aksh Stop Giving Agents
Tokens Securing with Side-Car Proxies Separating reasoning from authority. Ritwik Ranjan | Girish Motwani AKSH | Security sidecar for AI agents 1<br>
02
THE HOOK Ordering food. Writing code? AKSH | Security sidecar for AI agents 2 REPORTED VIRAL SCREENSHOT Persuaded off-task An ordering chatbot apparently generated linked-list code. Off-task text is not yet an authorized action.<br>
03
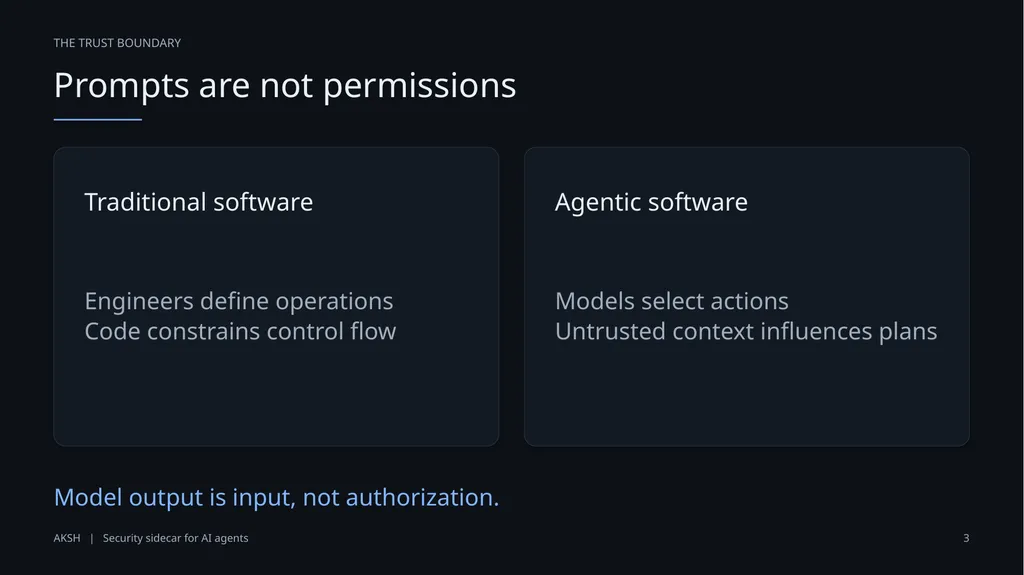
THE TRUST BOUNDARY Prompts are not permissions AKSH | Security sidecar for AI agents 3 Traditional software Engineers define operations
Code constrains control flow Agentic software Models select actions
Untrusted context influences plans Model output is input, not authorization.<br>
04
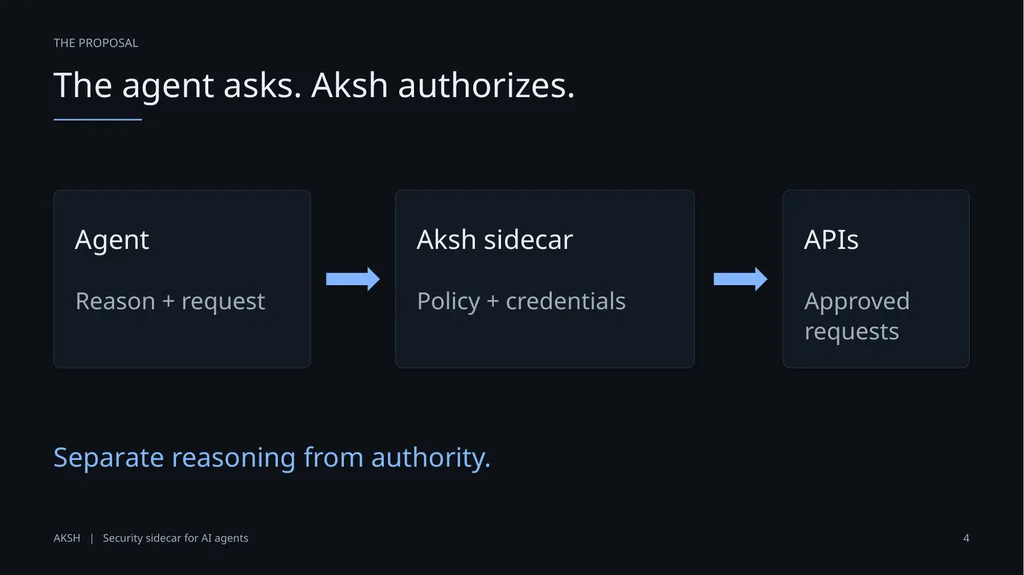
THE PROPOSAL The agent asks. Aksh authorizes. AKSH | Security sidecar for AI agents 4 Agent Reason + request Aksh sidecar Policy + credentials APIs Approved requests Separate reasoning from authority.<br>
05
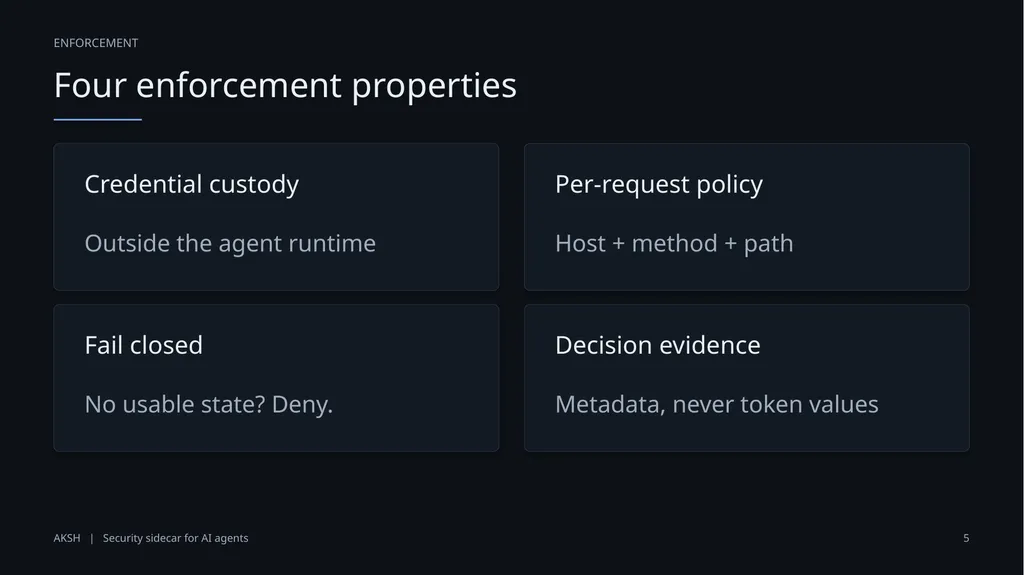
ENFORCEMENT Four enforcement properties AKSH | Security sidecar for AI agents 5 Credential custody Outside the agent runtime Per-request policy Host + method + path Fail closed No usable state? Deny. Decision evidence Metadata, never token values<br>
06
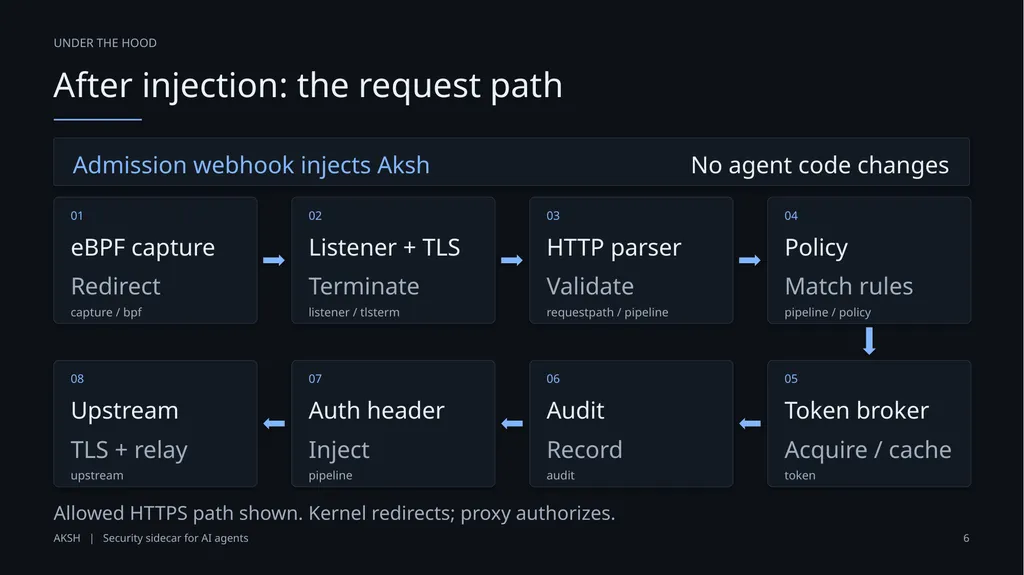
UNDER THE HOOD After injection: the request path AKSH | Security sidecar for AI agents 6 Admission webhook injects Aksh No agent code changes 01 eBPF capture Redirect capture / bpf 02 Listener + TLS Terminate listener / tlsterm 03 HTTP parser Validate requestpath / pipeline 04 Policy Match rules pipeline / policy 05 Token broker Acquire / cache token 06 Audit Record audit 07 Auth header Inject pipeline 08 Upstream TLS + relay upstream Allowed HTTPS path shown. Kernel redirects; proxy authorizes.<br>
07
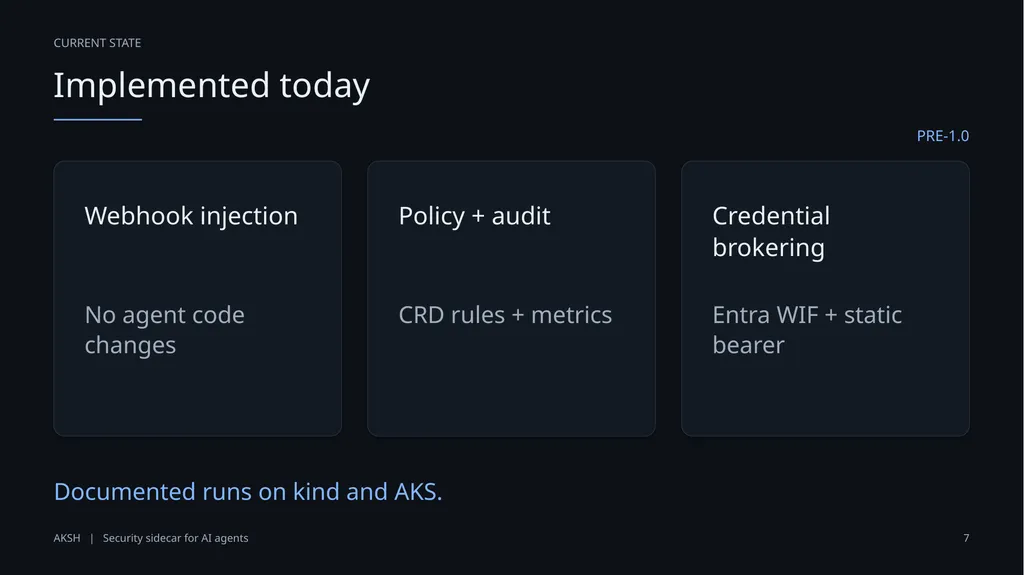
CURRENT STATE Implemented today AKSH | Security sidecar for AI agents 7 PRE-1.0 Webhook injection No agent code changes Policy + audit CRD rules + metrics Credential brokering Entra WIF + static bearer Documented runs on kind and AKS.<br>
08
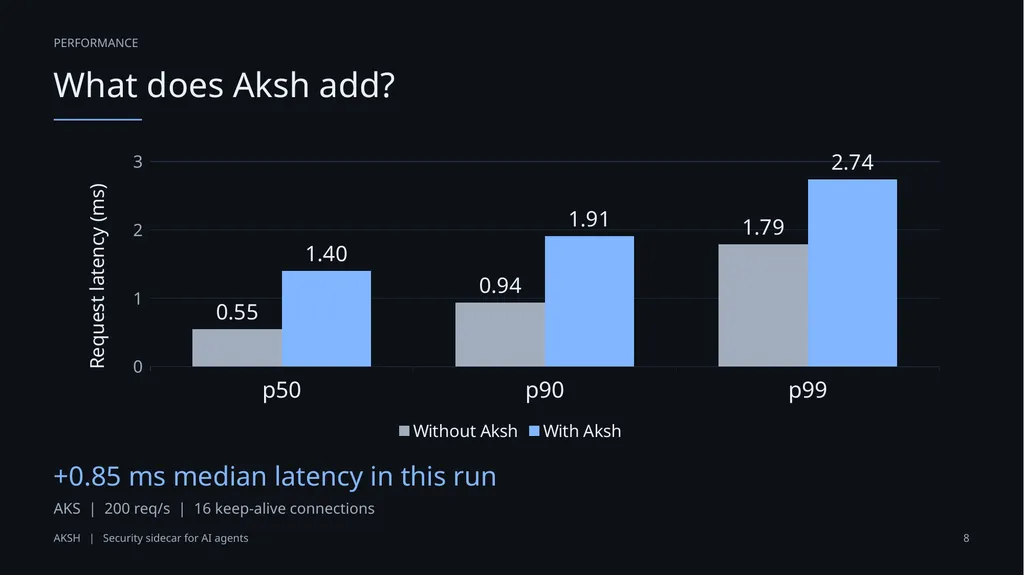
PERFORMANCE What does Aksh add? AKSH | Security sidecar for AI agents 8 +0.85 ms median latency in this run AKS | 200 req/s | 16 keep-alive connections<br>
09
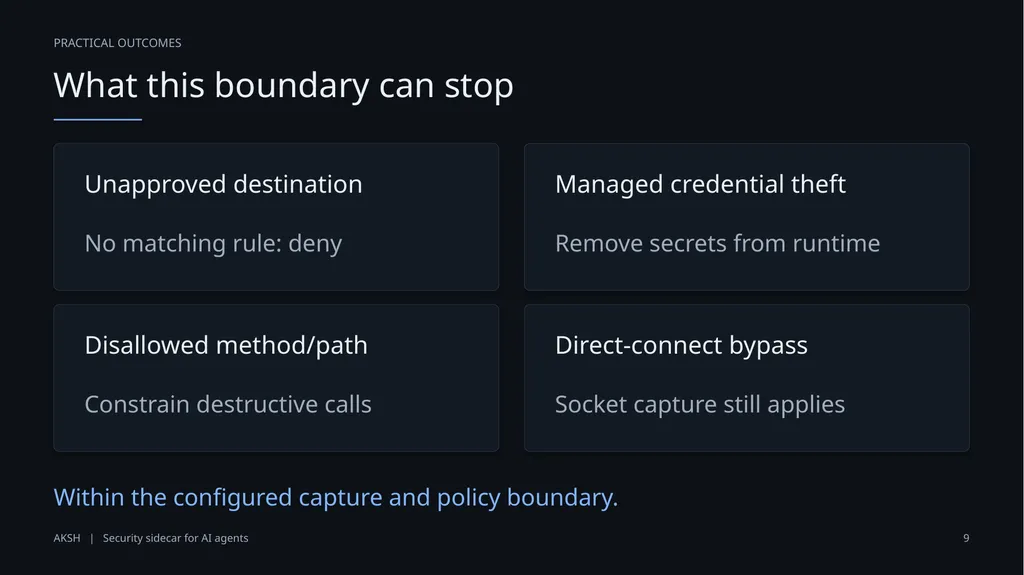
PRACTICAL OUTCOMES What this boundary can stop AKSH | Security sidecar for AI agents 9 Unapproved destination No matching rule: deny Managed credential theft Remove secrets from runtime Disallowed method/path Constrain destructive calls Direct-connect bypass Socket capture still applies Within the configured capture and policy boundary.<br>
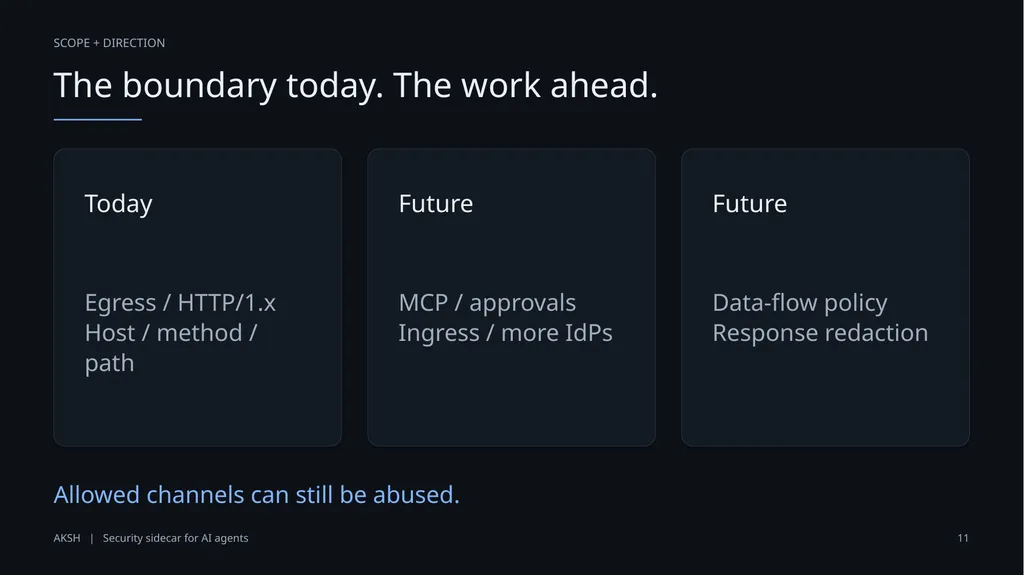
SCOPE + DIRECTION The boundary today. The work ahead. AKSH | Security sidecar for AI agents 11 Today Egress / HTTP/1.x
Host / method / path Future MCP / approvals
Ingress / more IdPs Future Data-flow policy
Response redaction Allowed channels can still be abused.<br>
12
Demo Same agent. Baseline credential leak, then policy enforcement and credential brokering with Aksh.<br>
13
Q&A<br>
14
BUILD WITH US Star Aksh
on GitHub Help us build safer agents. github.com/girishmotwani/aksh SCAN FOR THE MAIN BRANCH<br>