Browser Instrumentation for Exploit Analysis Mihai Neagu, Bitdefender About Mihai Neagu Exploit research Bitdefender Past: Cloud-based protocols Data encryption Reverse engineering Summary Exploit Kits MagnitudeCerber demo The problem
"Browser Instrumentation for Exploit Analysis Mihai" is the property of its rightful owner. Permission is granted to
download and print the materials on this website for personal, non-commercial use only, and to display it
on your personal computer provided you do not modify the materials and that you retain all copyright
notices contained in the materials. By downloading content from our website, you accept the terms of this
agreement.
Presentation Transcript
01
Browser Instrumentation for Exploit Analysis Mihai Neagu, Bitdefender<br>
02
About Mihai Neagu – Exploit research @ Bitdefender
Past:
Cloud-based protocols
Data encryption
Reverse engineering<br>
03
Summary Exploit Kits
Magnitude/Cerber demo
The problem
Browser instrumentation
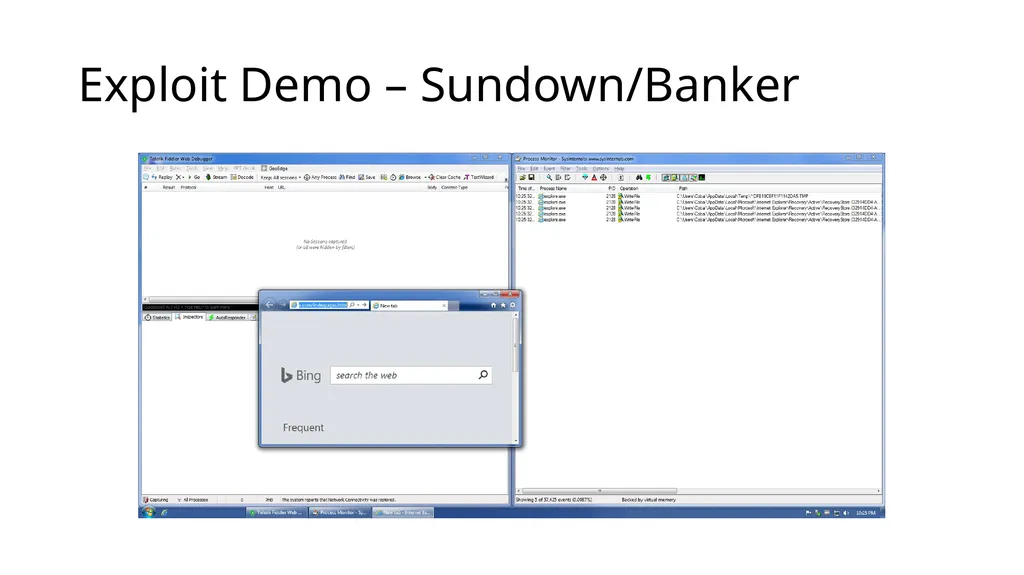
Sundown/Banker demo
Word of advice<br>
04
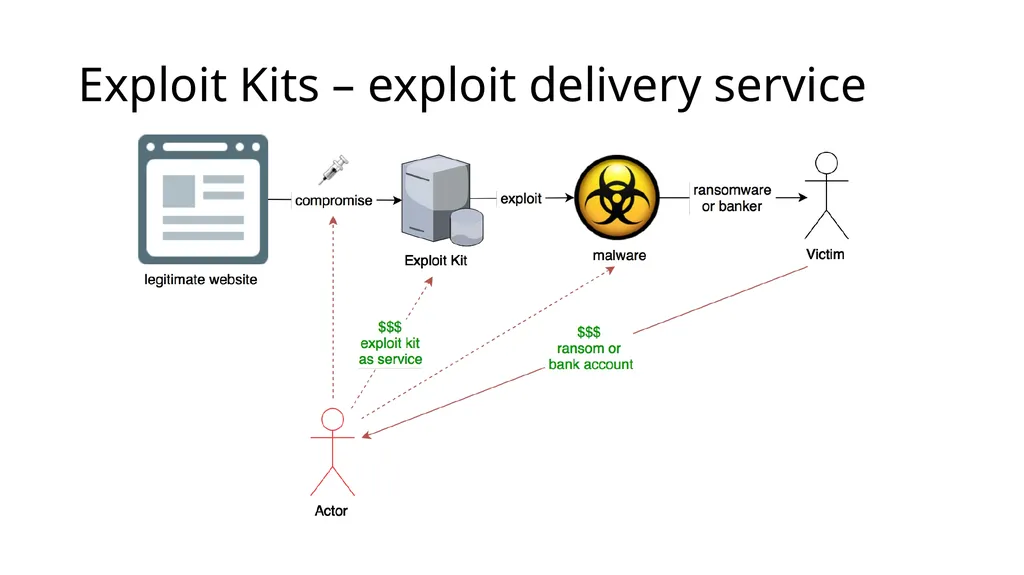
Exploit Kits – exploit delivery service<br>
05
What I’m interested in What’s the Exploit Kit
What’s the exploit
What’s the malware<br>
06
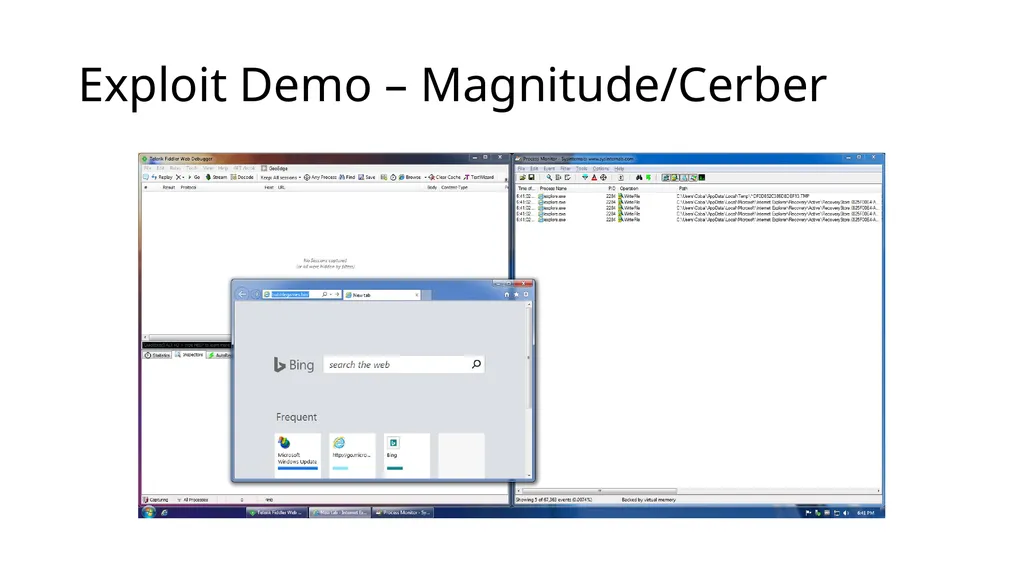
Exploit Demo – Magnitude/Cerber<br>
07
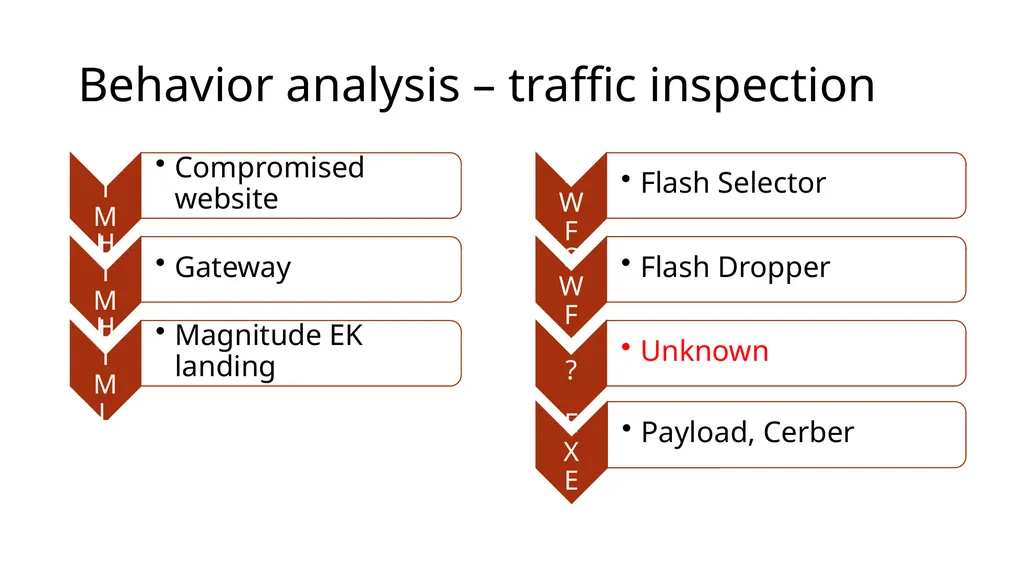
Behavior analysis – traffic inspection<br>
08
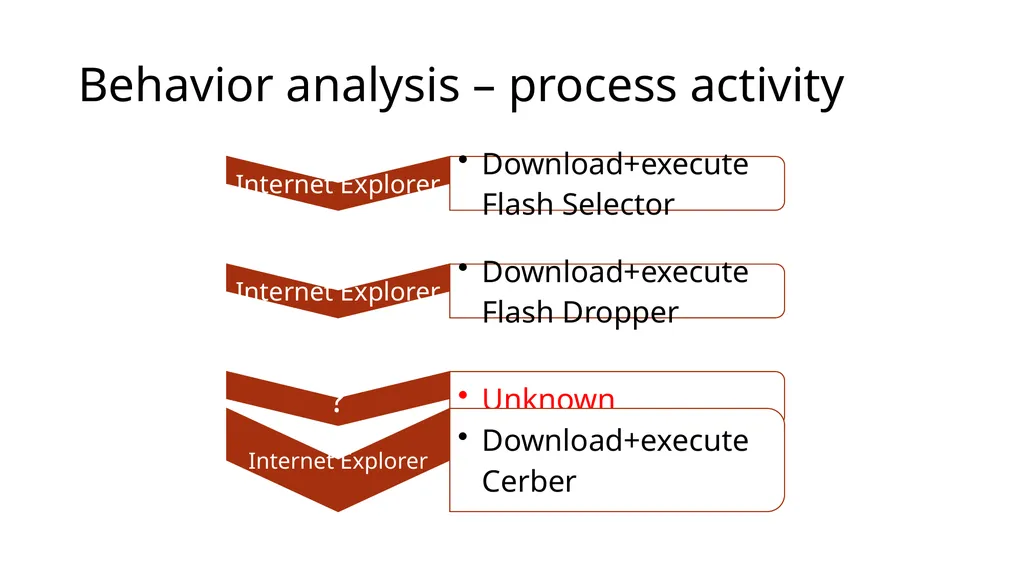
Behavior analysis – process activity<br>
09
The problem Flash Dropper has no exploit code
Where is the actual exploit?
How is Cerber downloaded and executed?
We need more in-depth inspection<br>
10
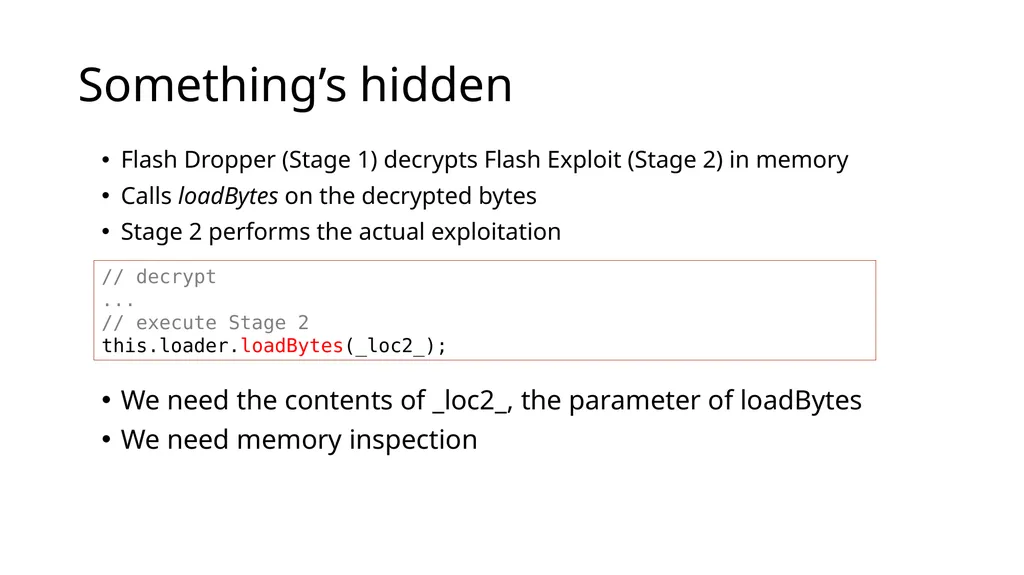
Something’s hidden Flash Dropper (Stage 1) decrypts Flash Exploit (Stage 2) in memory
Calls loadBytes on the decrypted bytes
Stage 2 performs the actual exploitation // decrypt
...
// execute Stage 2
this.loader.loadBytes(_loc2_); We need the contents of _loc2_, the parameter of loadBytes
We need memory inspection<br>
11
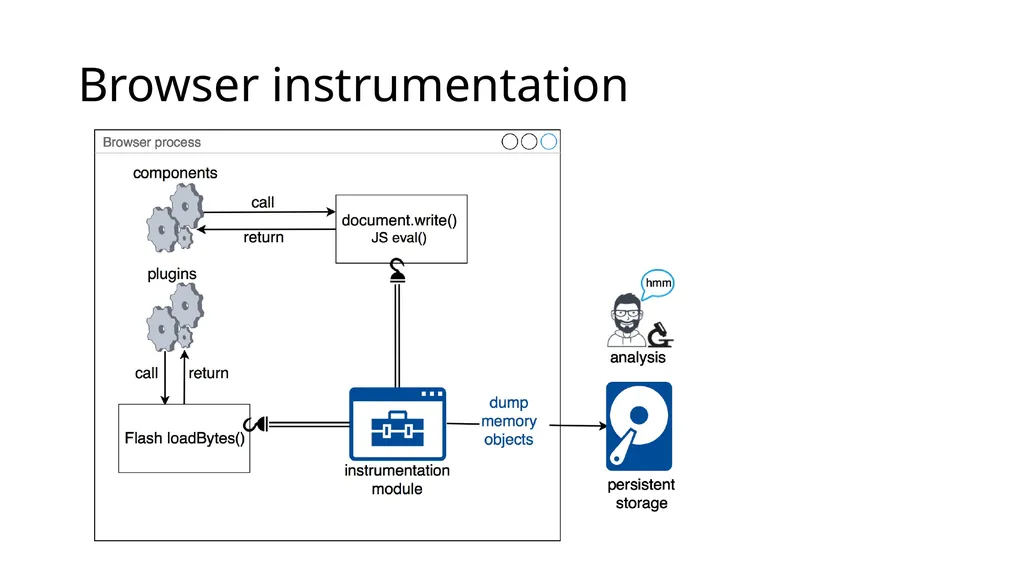
Browser instrumentation<br>
12
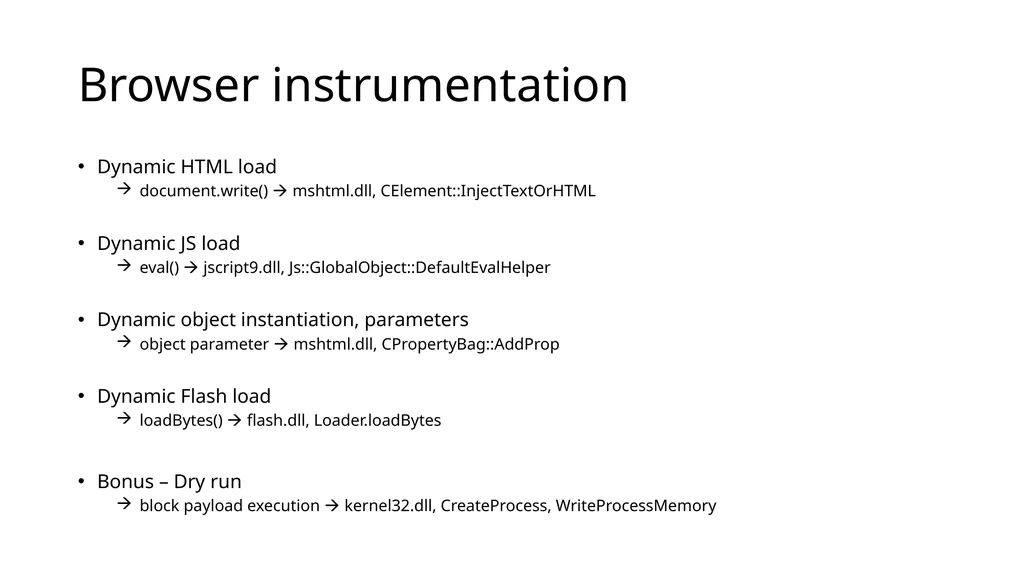
Browser instrumentation Dynamic HTML load
document.write() mshtml.dll, CElement::InjectTextOrHTML
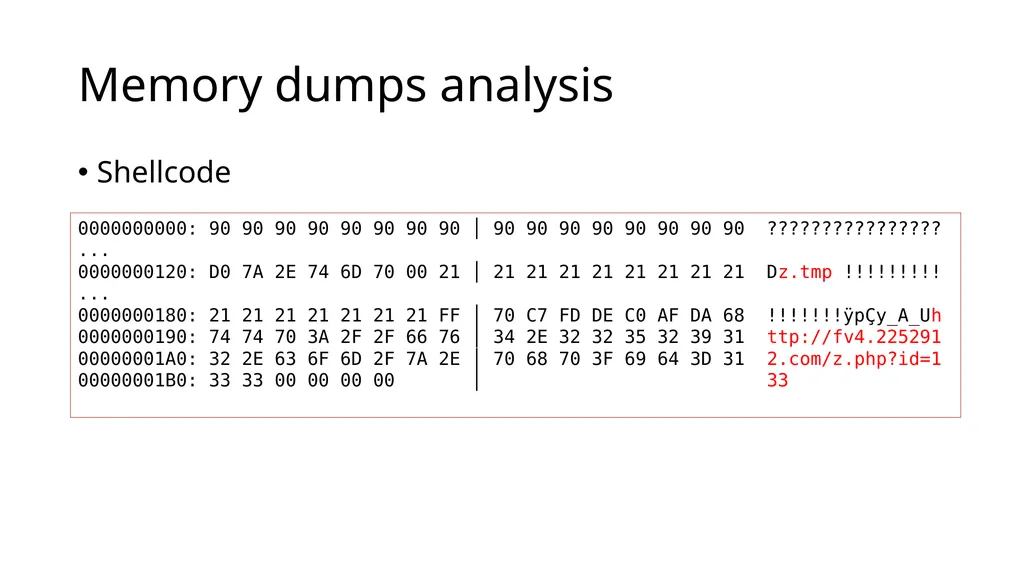
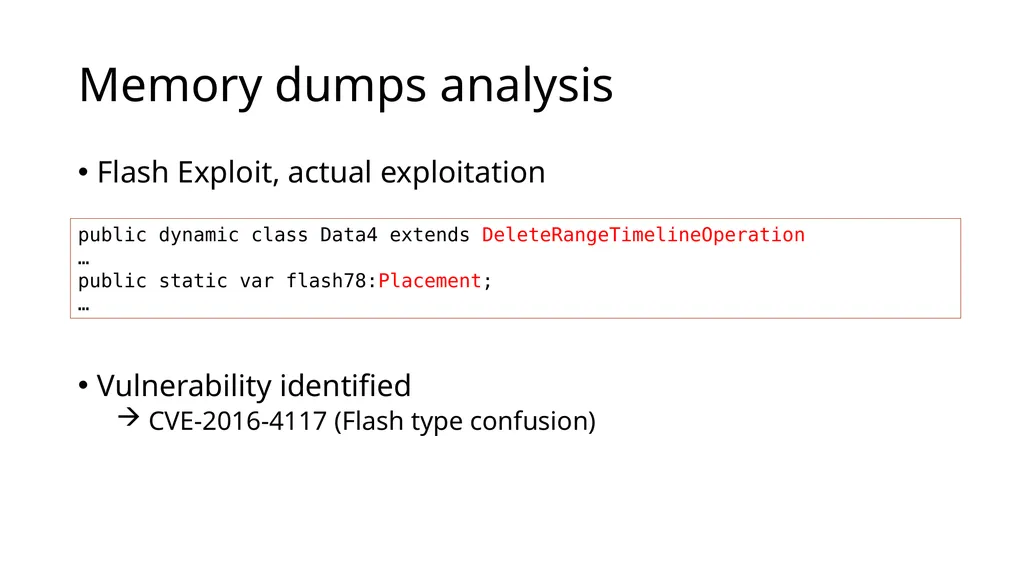
Memory dumps analysis Flash Exploit, actual exploitation public dynamic class Data4 extends DeleteRangeTimelineOperation
…
public static var flash78:Placement;
… Vulnerability identified
CVE-2016-4117 (Flash type confusion)<br>
18
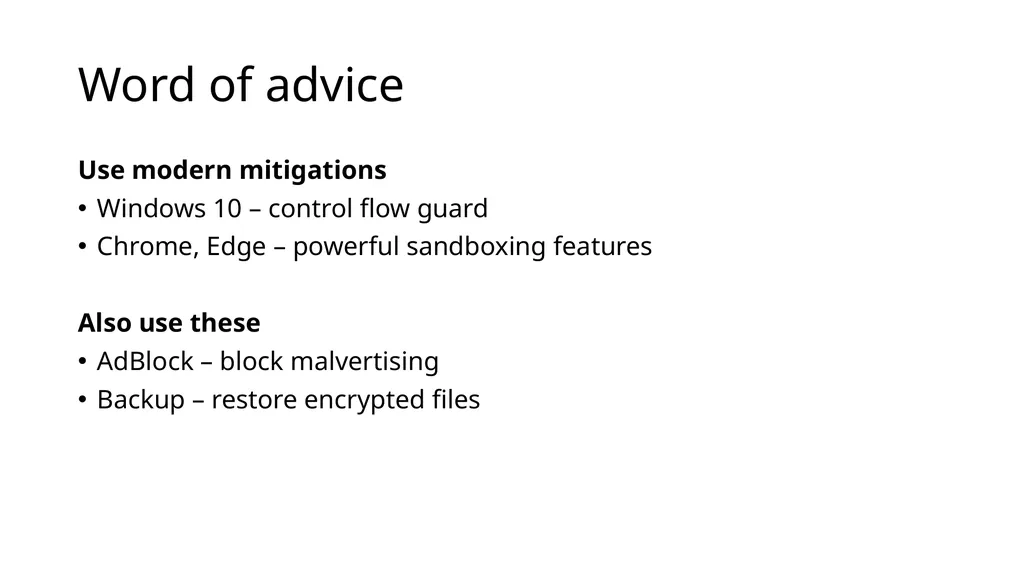
Word of advice Use modern mitigations
Windows 10 – control flow guard
Chrome, Edge – powerful sandboxing features
Also use these
AdBlock – block malvertising
Backup – restore encrypted files<br>