04
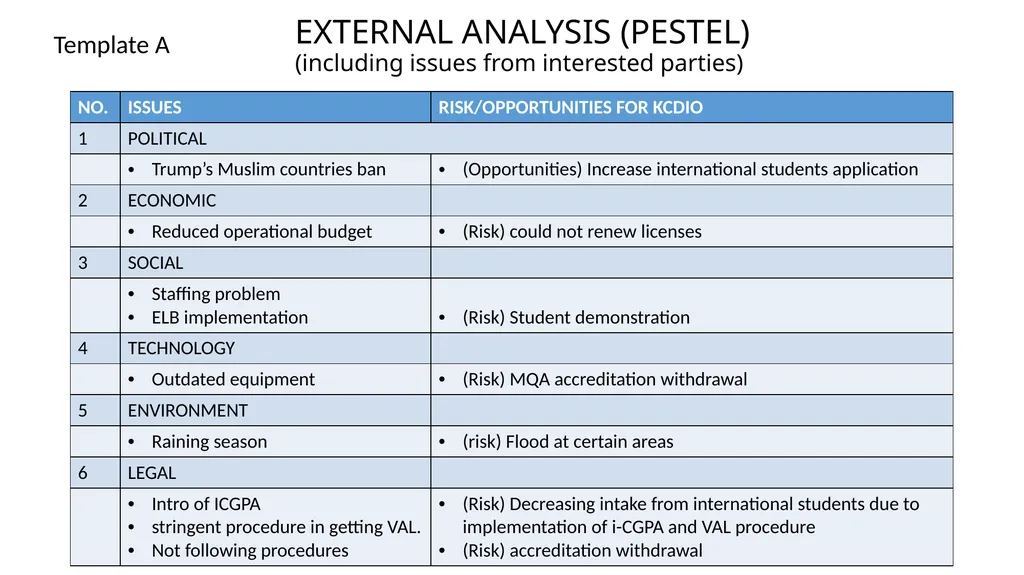
EXTERNAL ANALYSIS (PESTEL) �(including issues from interested parties) 4 Template A<br>
05
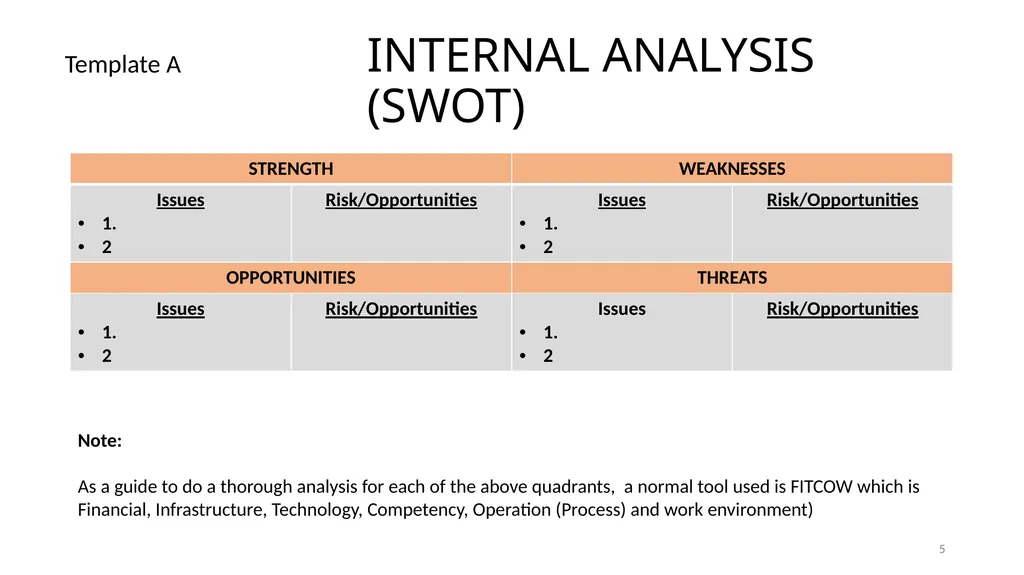
INTERNAL ANALYSIS (SWOT) 5 Note:
As a guide to do a thorough analysis for each of the above quadrants, a normal tool used is FITCOW which is Financial, Infrastructure, Technology, Competency, Operation (Process) and work environment) Template A<br>
06
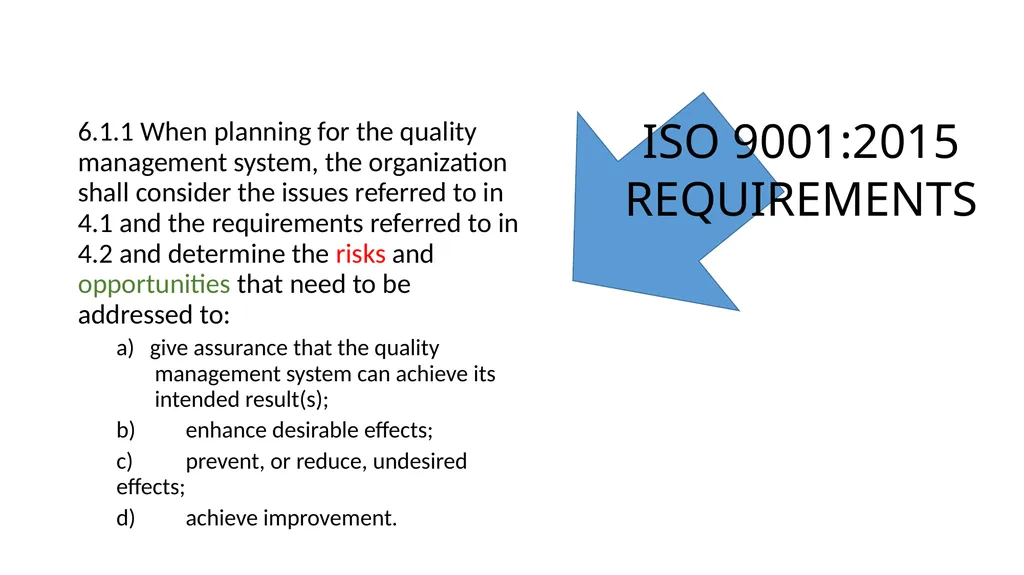
6.1.1 When planning for the quality management system, the organization shall consider the issues referred to in 4.1 and the requirements referred to in 4.2 and determine the risks and opportunities that need to be addressed to:
a) give assurance that the quality management system can achieve its intended result(s);
b) enhance desirable effects;
c) prevent, or reduce, undesired effects;
d) achieve improvement. ISO 9001:2015 REQUIREMENTS<br>
07
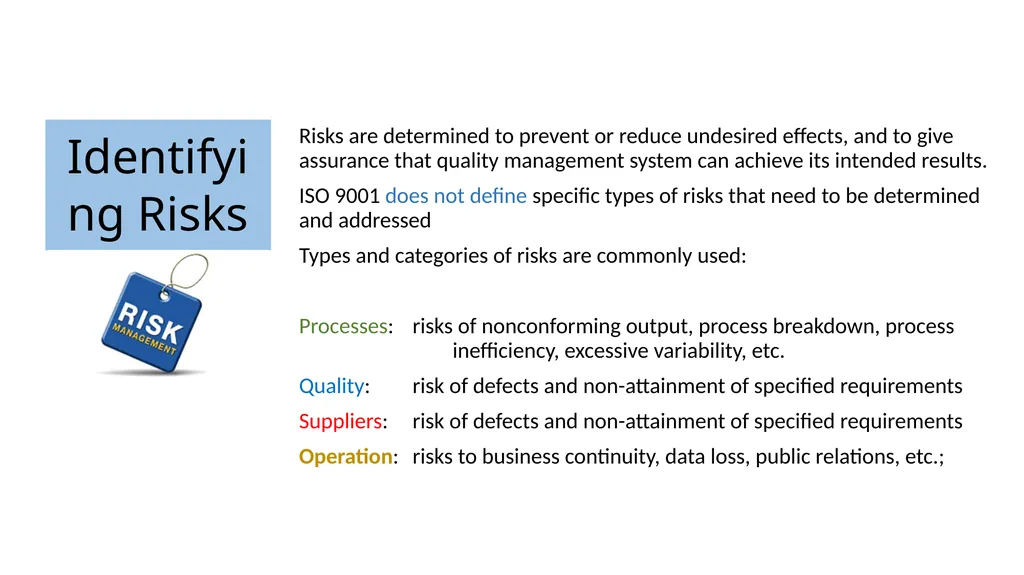
Identifying Risks Risks are determined to prevent or reduce undesired effects, and to give assurance that quality management system can achieve its intended results.
ISO 9001 does not define specific types of risks that need to be determined and addressed
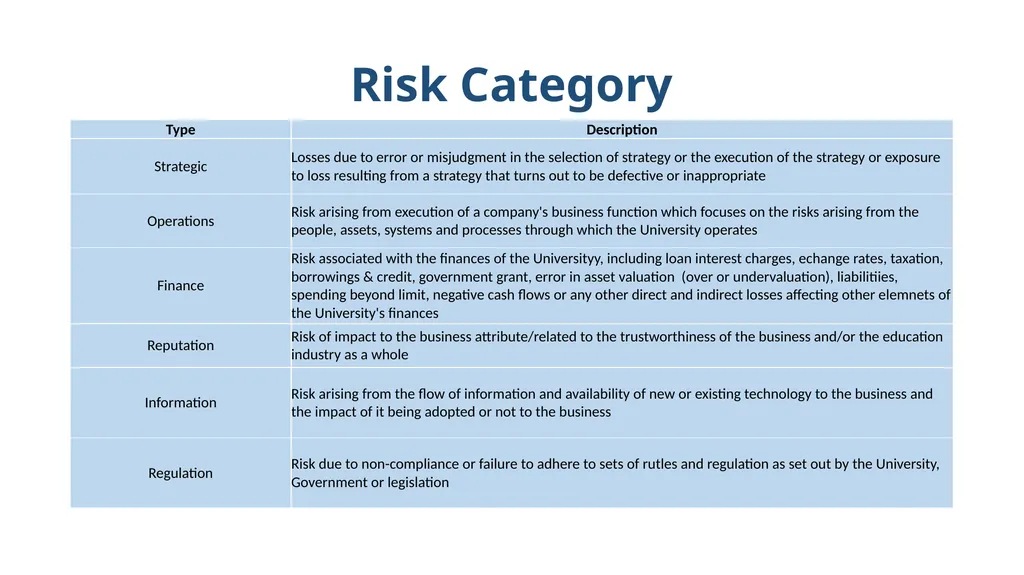
Types and categories of risks are commonly used:
Processes: risks of nonconforming output, process breakdown, process inefficiency, excessive variability, etc.
Quality: risk of defects and non-attainment of specified requirements
Suppliers: risk of defects and non-attainment of specified requirements
Operation: risks to business continuity, data loss, public relations, etc.;<br>
08
What about Opportunity? Apart from the risks, the organization has to also identify the opportunities that may come in its way.
Opportunities can be in form of adoption of new practices, launching of new products or services, opening new markets, addressing new clients, building partnerships, using new technology and other desirable and viable possibilities to address the organization’s or its customers’ needs.<br>
09
Why Risks are considered? Risk : Effect of uncertainties
Risk Level: Likelihood x consequences
Risks and opportunities can affect conformity of products and services and the ability to enhance customer satisfaction are determined and addressed<br>
10
Managing Risks Step 1: Identify the Risk. ...
Step 2: Analyze the risk. ...
Step 3: Evaluate or Rank the Risk. ...
Step 4: Treat the Risk. ...
Step 5: Monitor and Review the risk.<br>
11
Brainstorming
Environmental/Horizon Scanning
Interviews
Past data Analysis<br>
12
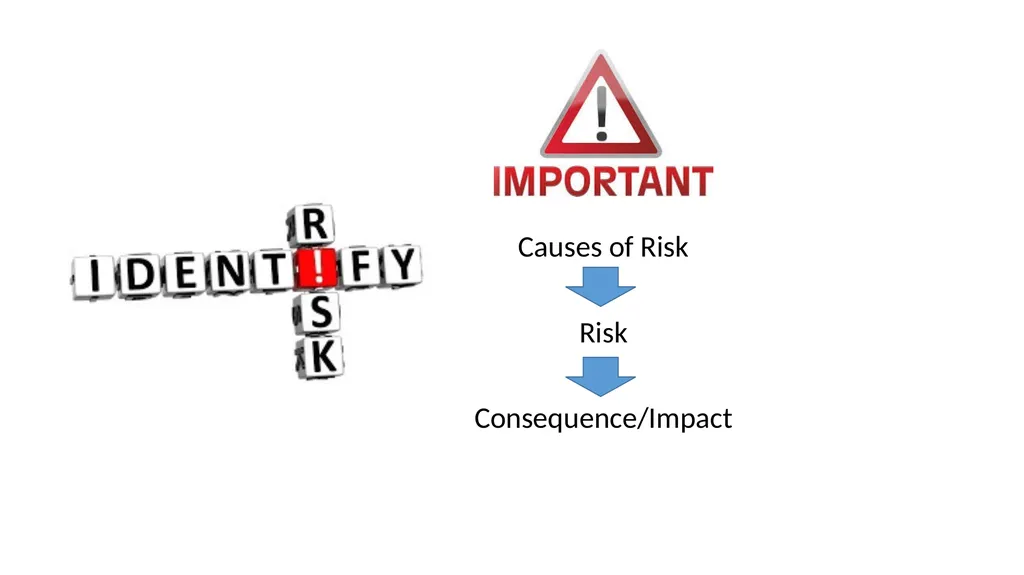
Causes of Risk
Risk
Consequence/Impact<br>
13
According to a leading global provider of risk management services AON in their 2011 Global Risk Management Survey (AON, 2013) the top three risks for higher education are ranked as follows:
1. Regulatory and legislative changes
2. Economic slowdown
3. Damage to brand or reputation Online Journal of Applied Knowledge Management, Volume 2, Issue 1, 2014<br>
14
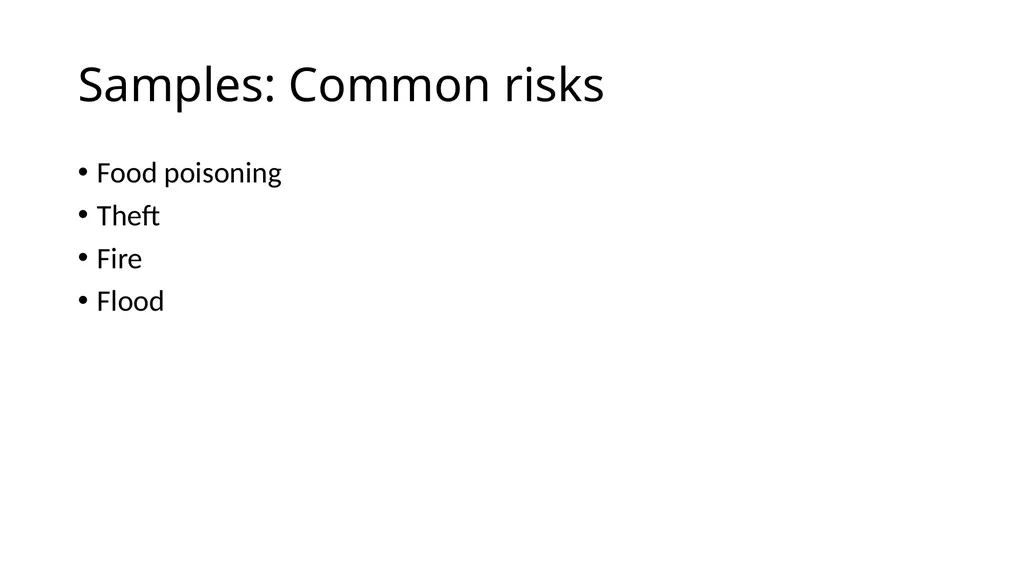
Samples: Common risks Food poisoning
Theft
Fire
Flood<br>
15
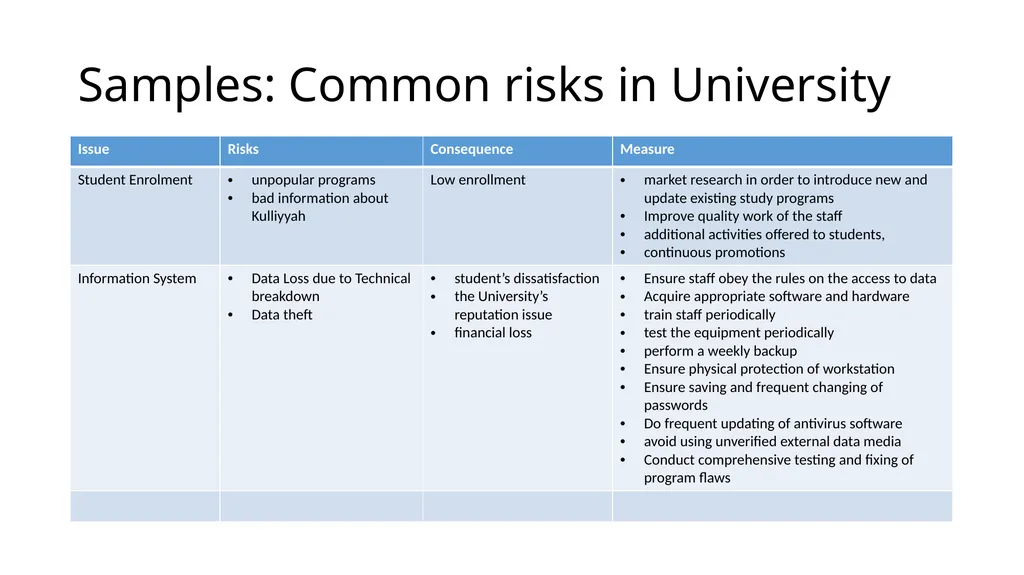
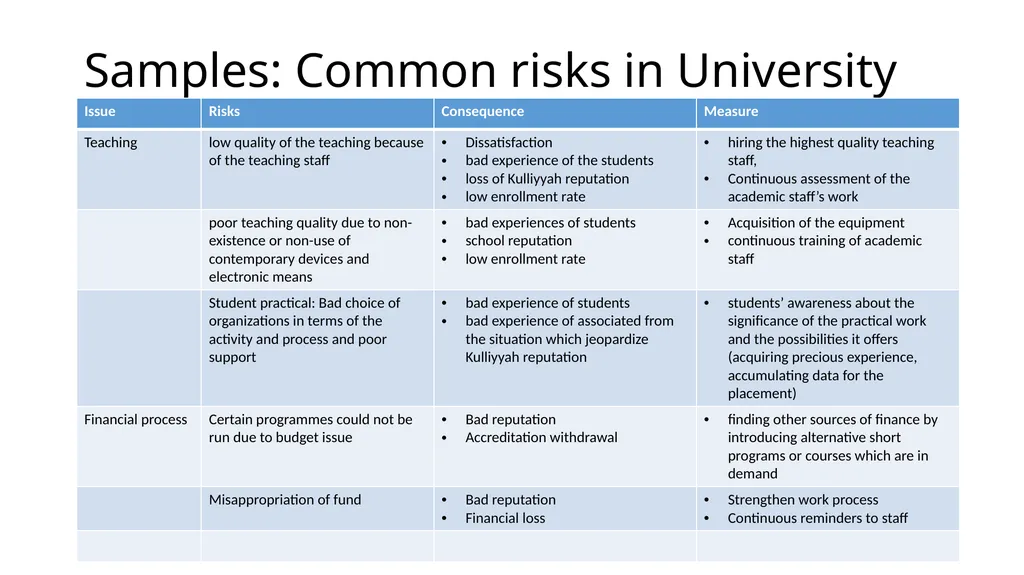
Samples: Common risks in University<br>
16
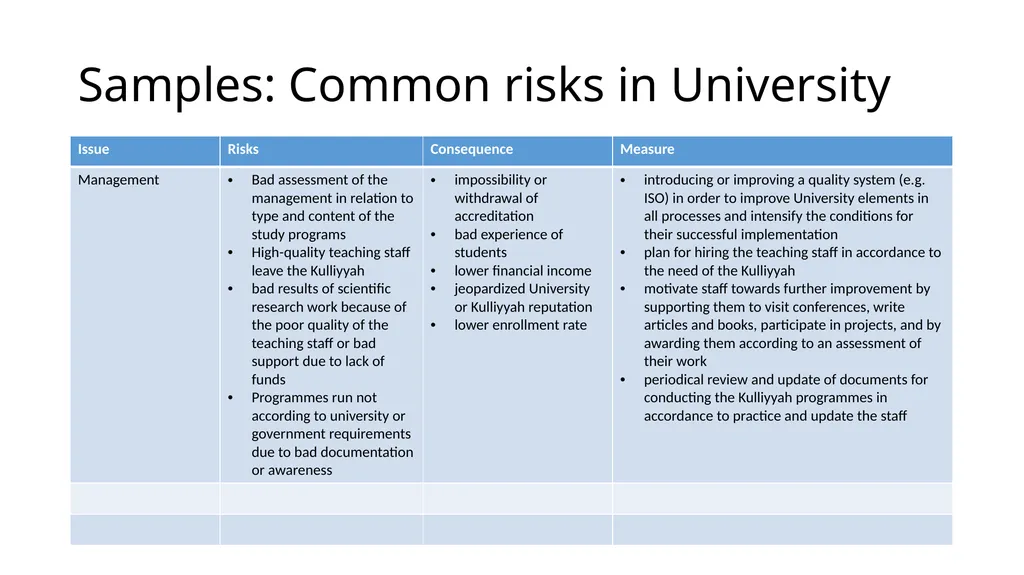
Samples: Common risks in University<br>
17
Samples: Common risks in University<br>
20
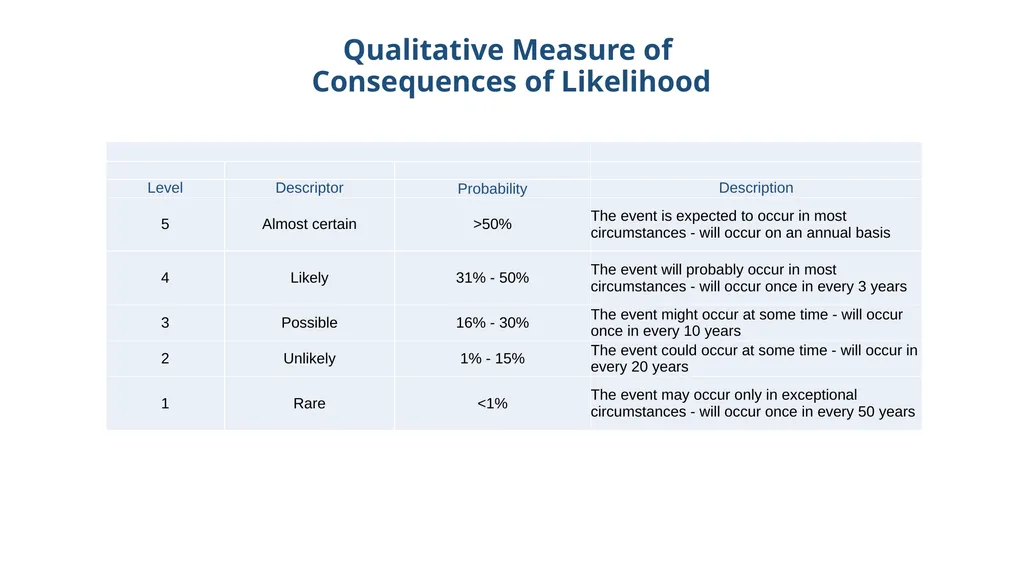
Qualitative Measure of �Consequences of Likelihood<br>
21
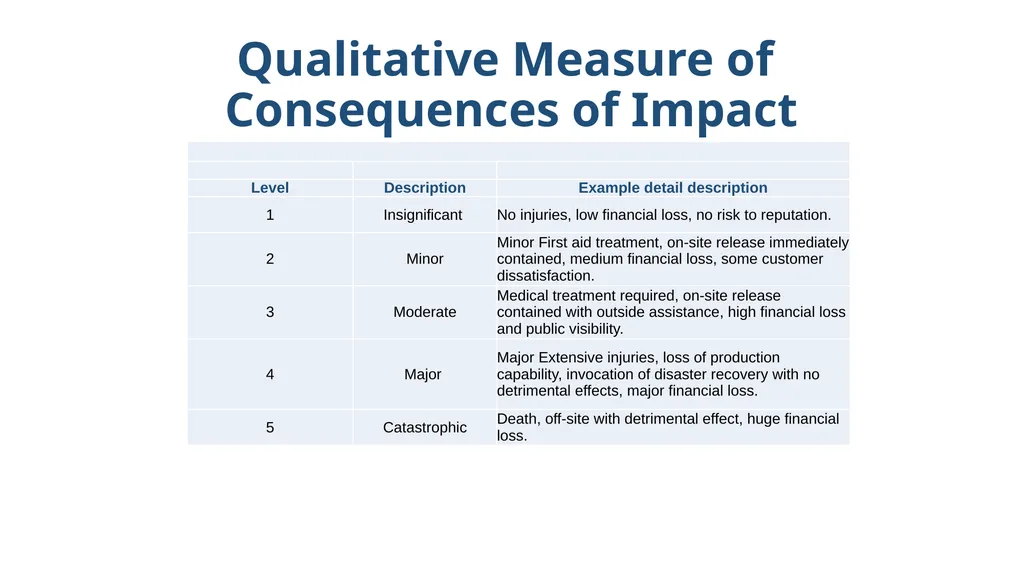
Qualitative Measure of �Consequences of Impact<br>
22
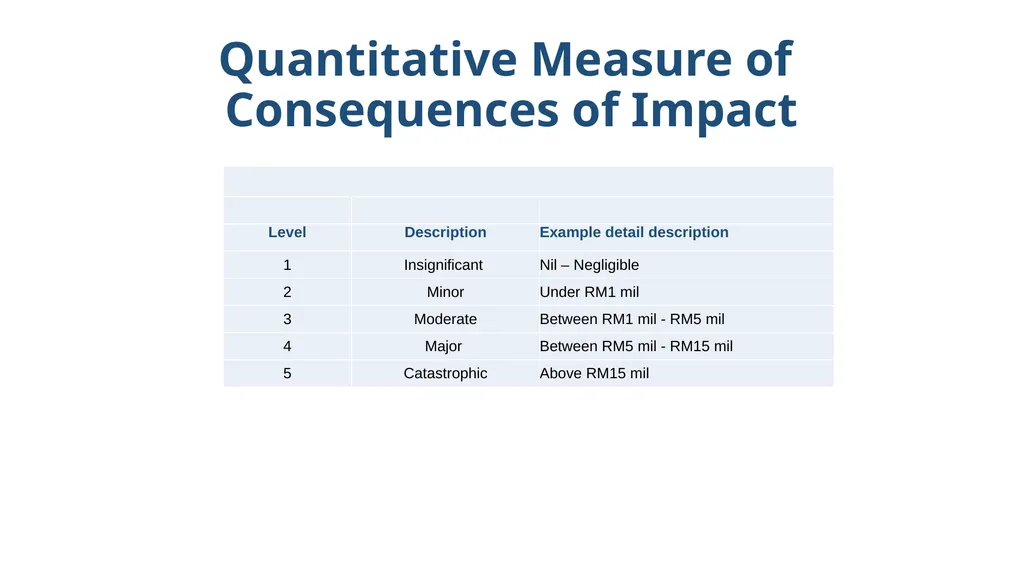
Quantitative Measure of �Consequences of Impact<br>
23
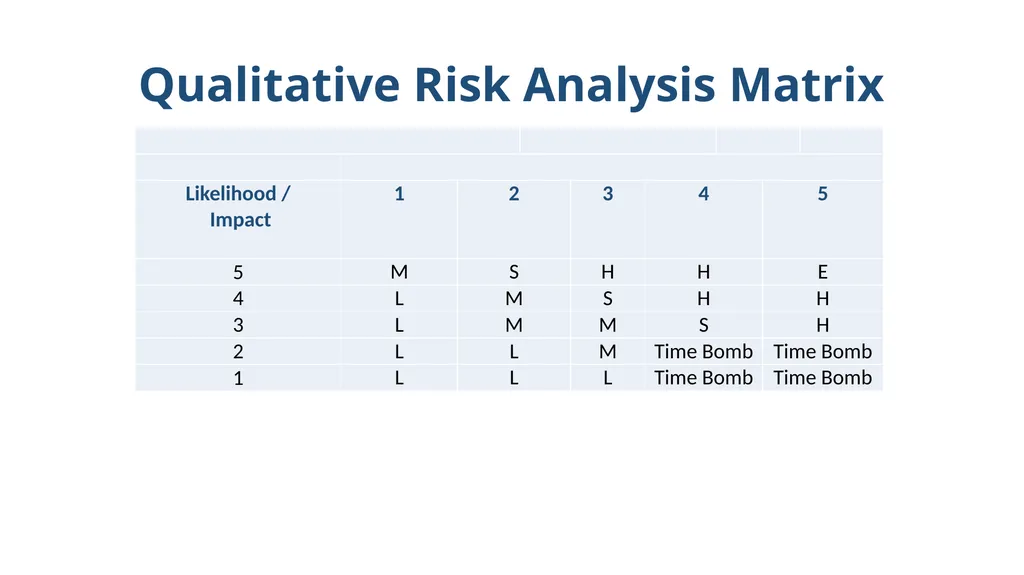
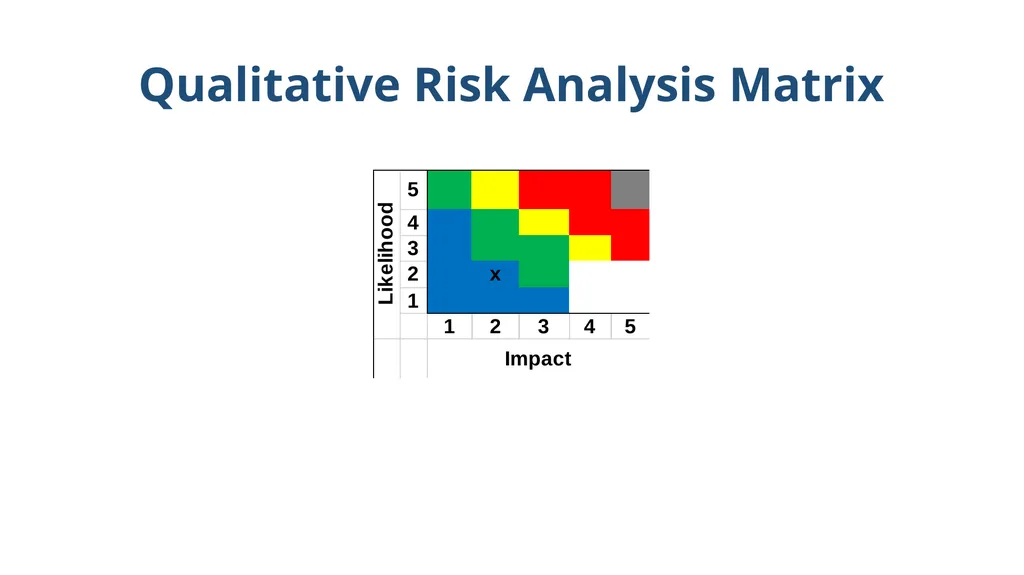
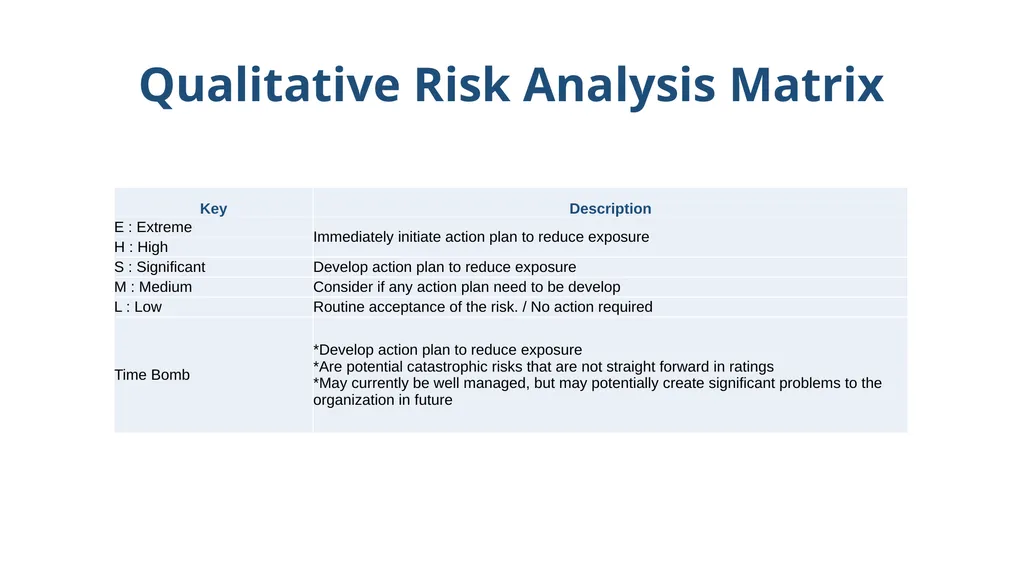
Qualitative Risk Analysis Matrix<br>
24
Qualitative Risk Analysis Matrix<br>
25
Qualitative Risk Analysis Matrix<br>
26
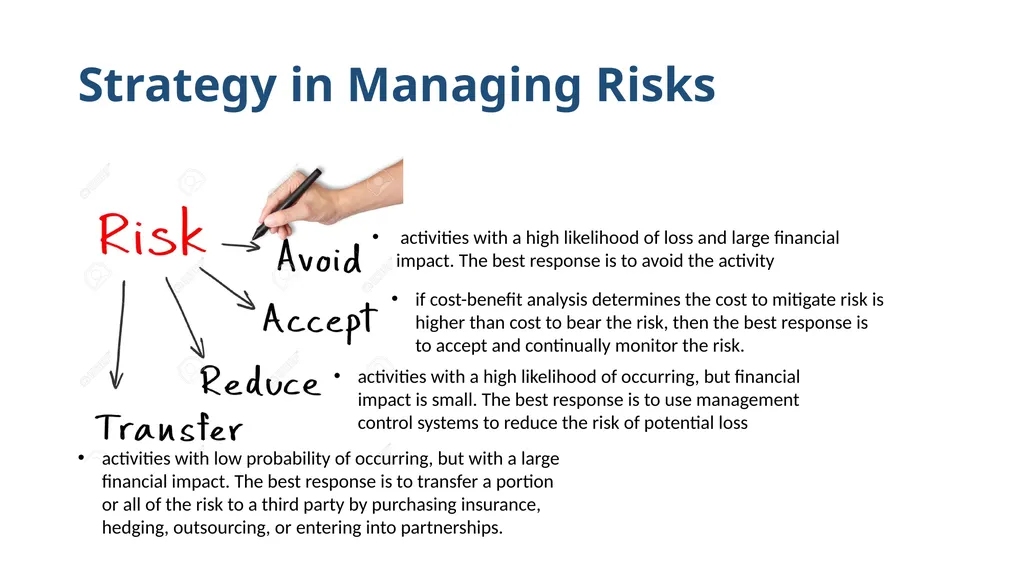
Strategy in Managing Risks activities with a high likelihood of loss and large financial impact. The best response is to avoid the activity activities with low probability of occurring, but with a large financial impact. The best response is to transfer a portion or all of the risk to a third party by purchasing insurance, hedging, outsourcing, or entering into partnerships. if cost-benefit analysis determines the cost to mitigate risk is higher than cost to bear the risk, then the best response is to accept and continually monitor the risk. activities with a high likelihood of occurring, but financial impact is small. The best response is to use management control systems to reduce the risk of potential loss<br>
27
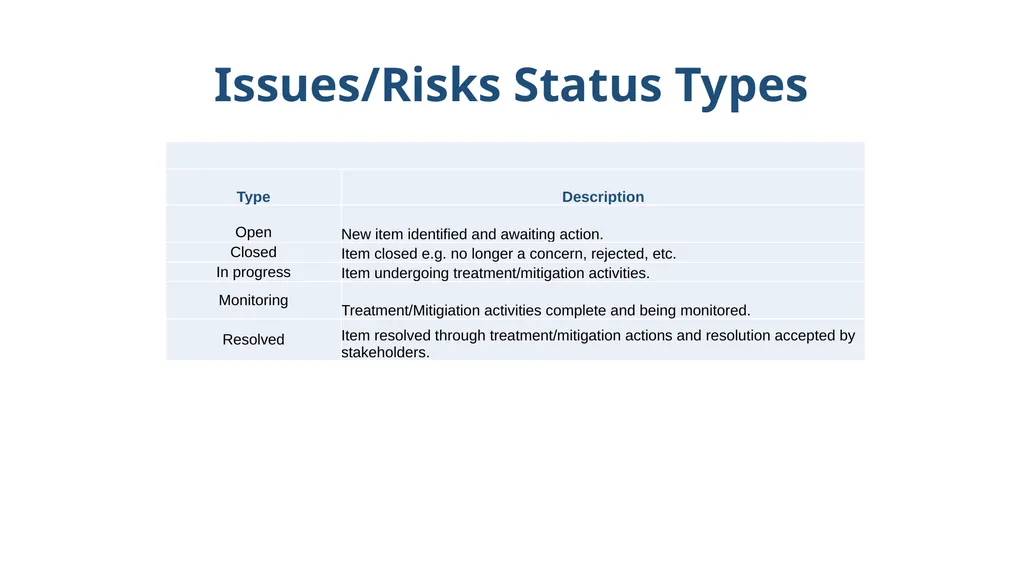
Issues/Risks Status Types<br>
28
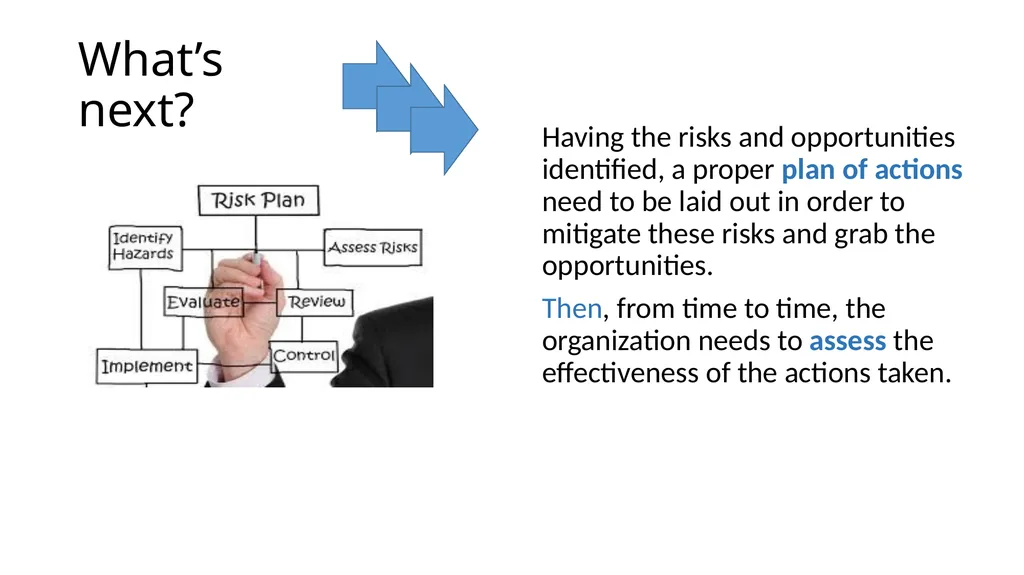
What’s next? Having the risks and opportunities identified, a proper plan of actions need to be laid out in order to mitigate these risks and grab the opportunities.
Then, from time to time, the organization needs to assess the effectiveness of the actions taken.<br>
29
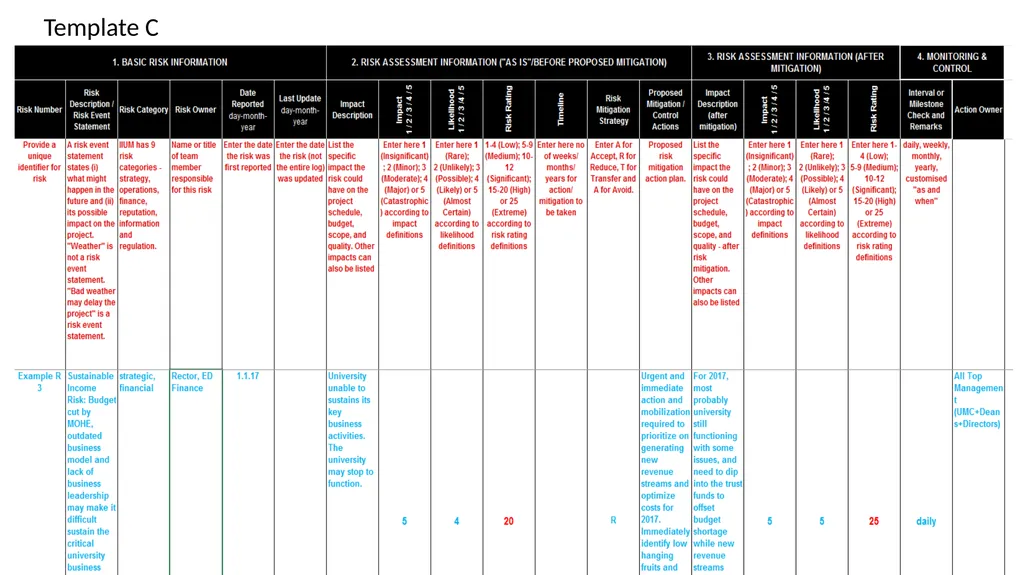
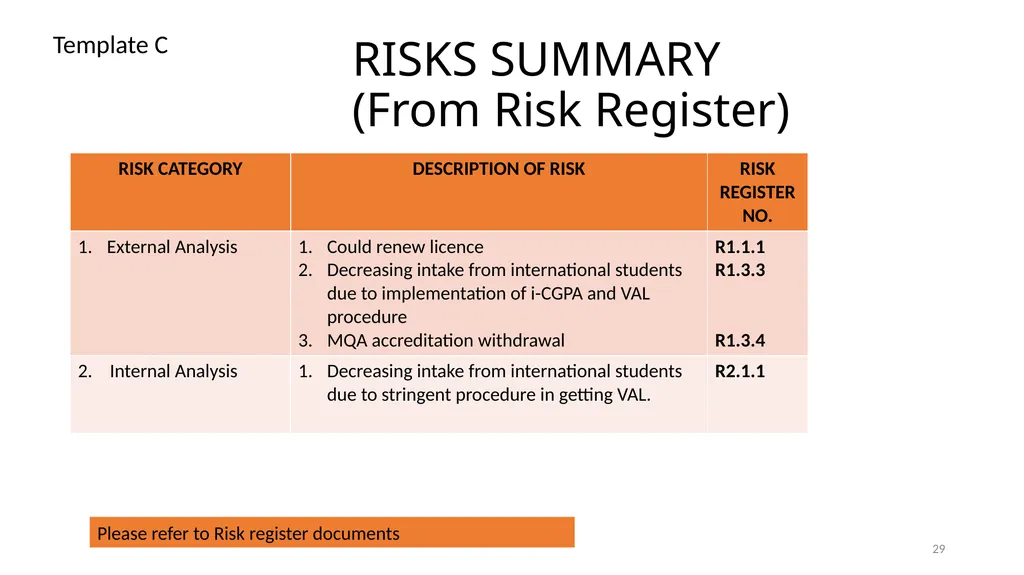
RISKS SUMMARY�(From Risk Register) 29 Please refer to Risk register documents Template C<br>
30
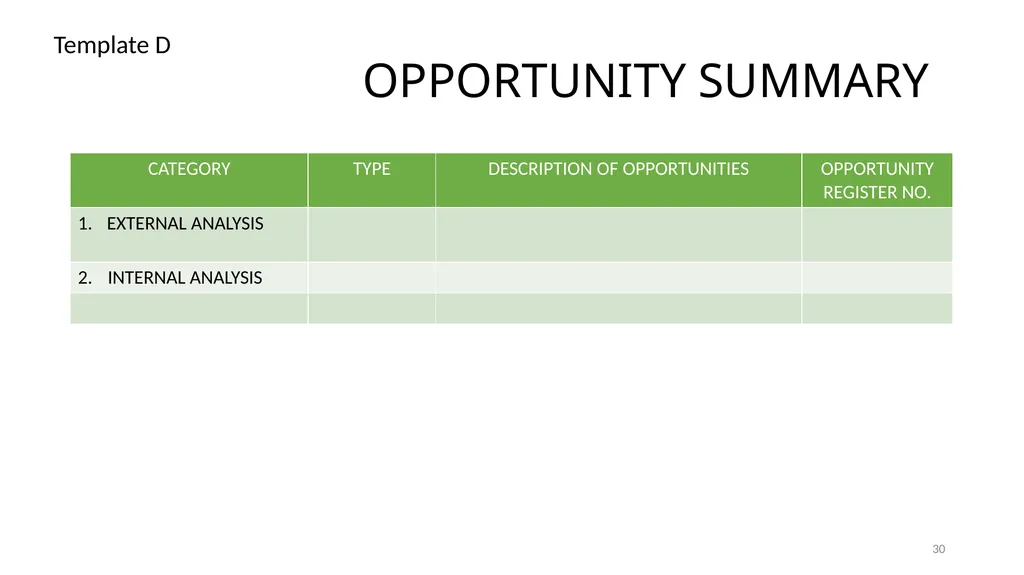
OPPORTUNITY SUMMARY 30 Template D<br>
31
Risks No:
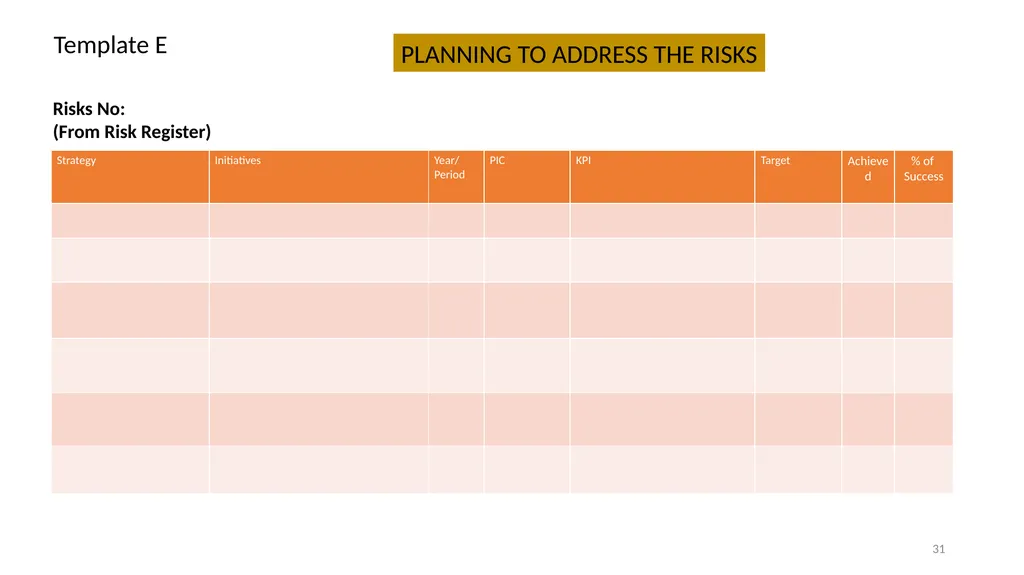
(From Risk Register) PLANNING TO ADDRESS THE RISKS 31 Template E<br>
32
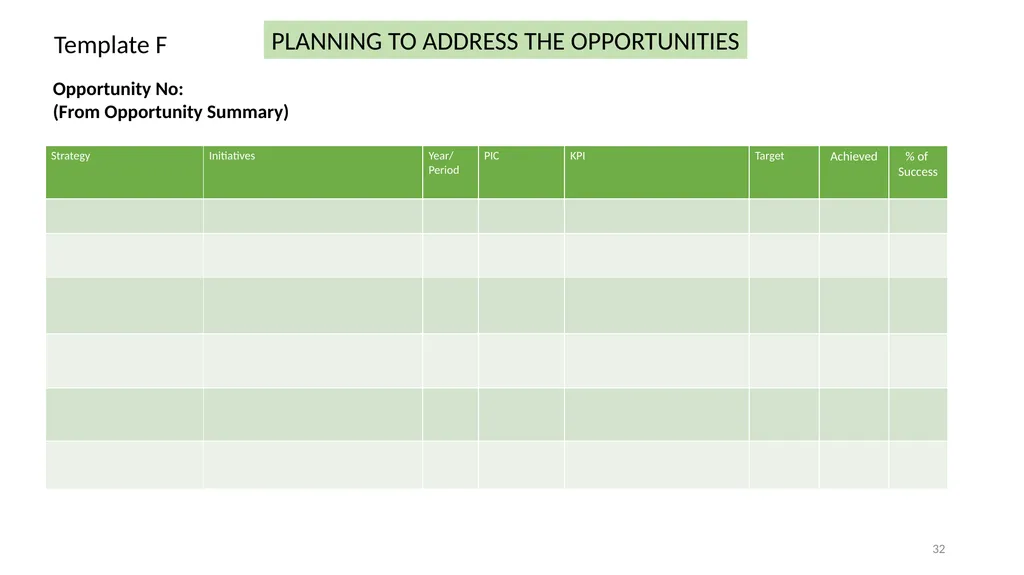
PLANNING TO ADDRESS THE OPPORTUNITIES 32 Opportunity No:
(From Opportunity Summary) Template F<br>
33
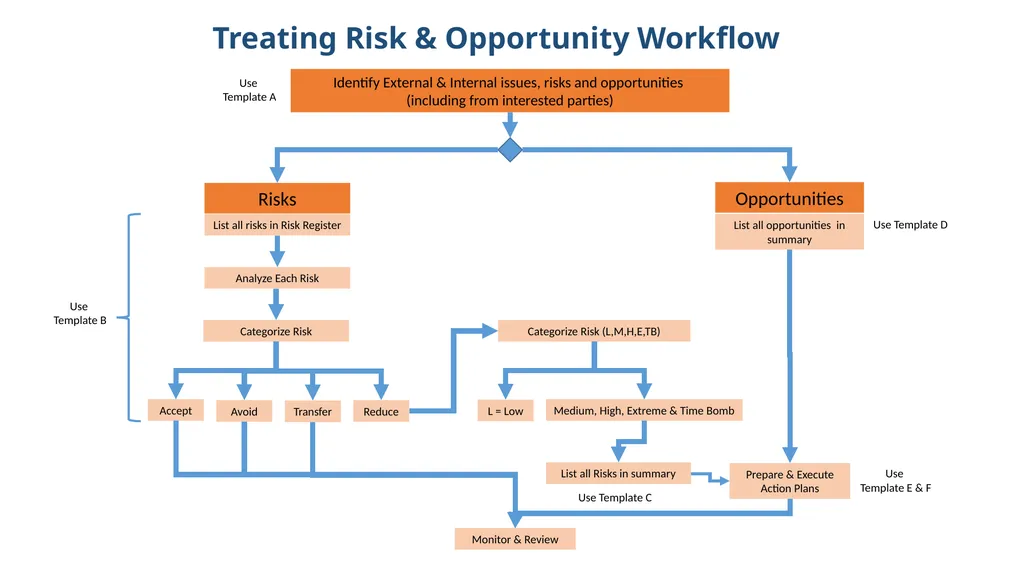
Treating Risk & Opportunity Workflow Identify External & Internal issues, risks and opportunities
(including from interested parties) Risks Opportunities List all risks in Risk Register Analyze Each Risk Categorize Risk Avoid Accept Transfer Reduce Categorize Risk (L,M,H,E,TB) L = Low Medium, High, Extreme & Time Bomb Prepare & Execute Action Plans Monitor & Review List all opportunities in summary List all Risks in summary Use
Template B Use
Template A Use Template C Use
Template E & F Use Template D<br>
34
ISO 9001:2015 ISO 9001:2015 - Risk-based thinking standard
Intent - To ensure organizations consider risks and opportunities that could affect the results of their plan.
Objective Evidence:
Risk & Opportunity Analysis on External and Internal Factors
Risk Profile/Register
Risk & Opportunity Action Plan
Action Plans have been carried out Summary<br>