
Management of Information Security, 4th Edition

Description: Management of Information Security, 4th Edition Chapter 9 Risk Management: Controlling Risk Objectives Recognize the strategy options used to control risk and be prepared to select from them when given background information Evaluate risk
Related Topics
Download Presentation
"Management of Information Security, 4th Edition" is the property of its rightful owner. Permission is granted to download and print the materials on this website for personal, non-commercial use only, and to display it on your personal computer provided you do not modify the materials and that you retain all copyright notices contained in the materials. By downloading content from our website, you accept the terms of this agreement.
Presentation Transcript
slide1. Management of Information Security, 4th Edition Chapter 9
Risk Management: Controlling Risk<br>
slide2. Objectives Recognize the strategy options used to control risk and be prepared to select from them when given background information
Evaluate risk controls and formulate a cost-benefit analysis (CBA) using existing conceptual frameworks
Explain how to maintain and perpetuate risk controls
Describe popular approaches used in the industry to manage risk Management of Information Security, 4th Edition 2<br>
slide3. Risk Control Strategies Once the InfoSec development team has created the ranked vulnerability worksheet, the team must choose one of five basic control strategies:
Defense
Transferal
Mitigation
Acceptance
Termination Management of Information Security, 4th Edition 3<br>
slide4. Defense Defense risk control strategy - attempts to prevent the exploitation of the vulnerability
Accomplished by means of countering threats, removing vulnerabilities in assets, limiting access to assets, and adding protective safeguards
Sometimes referred to as avoidance
Three common methods of risk defense:
Application of policy
Application of training and education
Implementation of technology Management of Information Security, 4th Edition 4<br>
slide5. Transferal Transferal risk control strategy - attempts to shift the risk to other assets, other processes, or other organizations
May be accomplished by:
Rethinking how services are offered
Revising deployment models
Outsourcing to other organizations
Purchasing insurance
Implementing service contracts with providers Management of Information Security, 4th Edition 5<br>
slide6. Mitigation Mitigation risk control strategy - attempts to reduce the damage caused by a realized incident or disaster
By means of planning and preparation
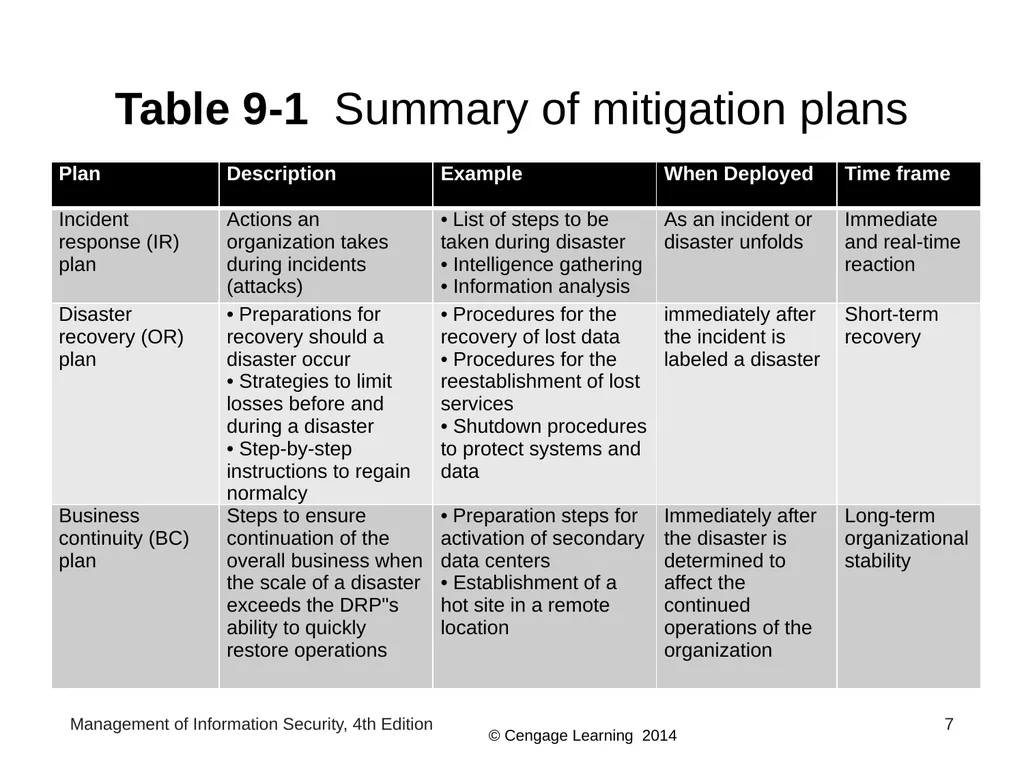
Includes three types of plans
Incident response (IR) plan
Disaster recovery (DR) plan
Business continuity (BC) plan
Mitigation depends on the ability to detect and respond to an attack as quickly as possible Management of Information Security, 4th Edition 6<br>
slide7. Table 9-1 Summary of mitigation plans Management of Information Security, 4th Edition 7<br>
slide8. Acceptance Acceptance risk control strategy - the decision to do nothing to protect an information asset from risk and accept the outcome
Acceptance is recognized as a valid strategy only when the organization has:
Determined the level of risk posed to the information asset
Assessed the probability of attack and the likelihood of a successful exploitation of a vulnerability
Estimated the potential damage or loss that could result from attacks Management of Information Security, 4th Edition 8<br>
slide9. Acceptance (continued) Acceptance is recognized as a valid strategy only when the organization has (cont’d):
Evaluated potential controls using each appropriate type of feasibility
Performed a thorough CBA
Determined that the costs to control the risk to a particular function, service, collection of data, or information asset do not justify the cost of implementing and maintaining controls
Strategy should be implemented when the cost of protecting an asset does not justify the expense Management of Information Security, 4th Edition 9<br>
slide10. Termination Termination risk control strategy - based on the organization’s need or choice not to protect an asset
The organization does not wish the asset to remain at risk so it is removed form the environment that represents risk
Termination must be a conscious business decision
Not simply the abandonment of an asset
Would technically qualify as acceptance Management of Information Security, 4th Edition 10<br>
slide11. Managing Risk Part 1 Risk appetite - the quantity and nature of risk that organizations are willing to accept
As they evaluate the trade-offs between perfect security and unlimited accessibility
Also known as risk tolerance
The key is for the organization to find balance in its decision-making processes and in its feasibility analyses
Assuring that its risk appetite is based on experience and facts, not on ignorance and wishful thinking Management of Information Security, 4th Edition 11<br>
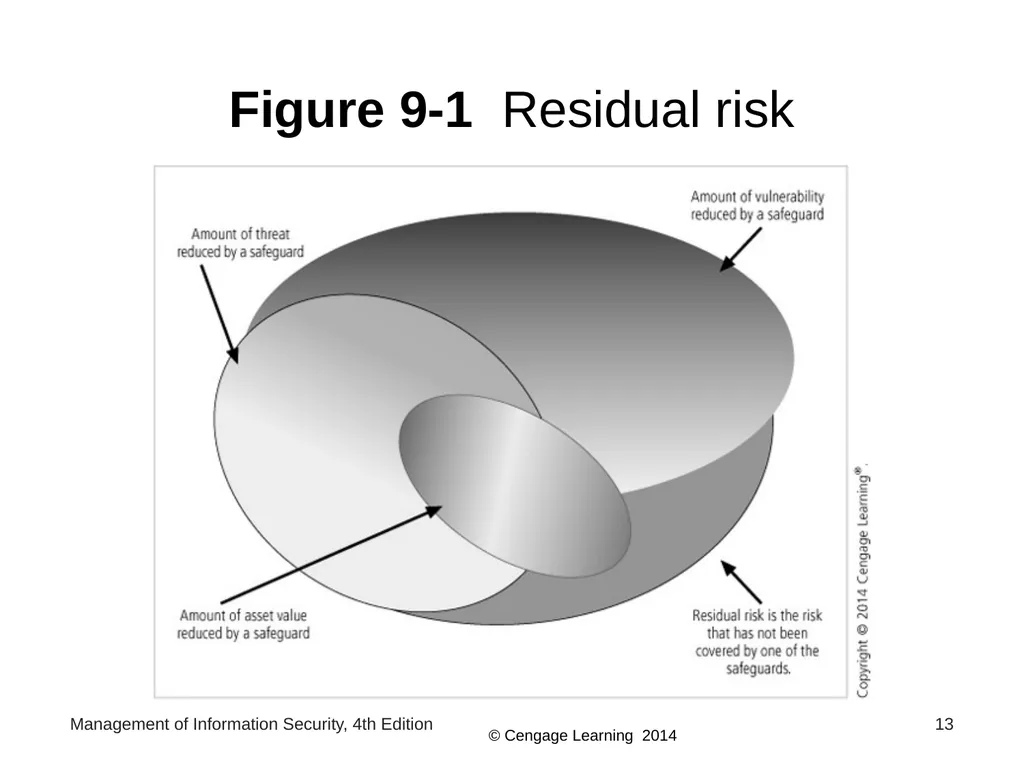
slide12. Managing Risk Part 2 Residual risk is the amount of risk that remains after the organization has implemented policy, education and training, and technical controls and safeguards
The goal of InfoSec is not to bring residual risk to zero
It is to bring residual risk in line with an organization’s risk appetite Management of Information Security, 4th Edition 12<br>
slide13. Figure 9-1 Residual risk Management of Information Security, 4th Edition 13<br>
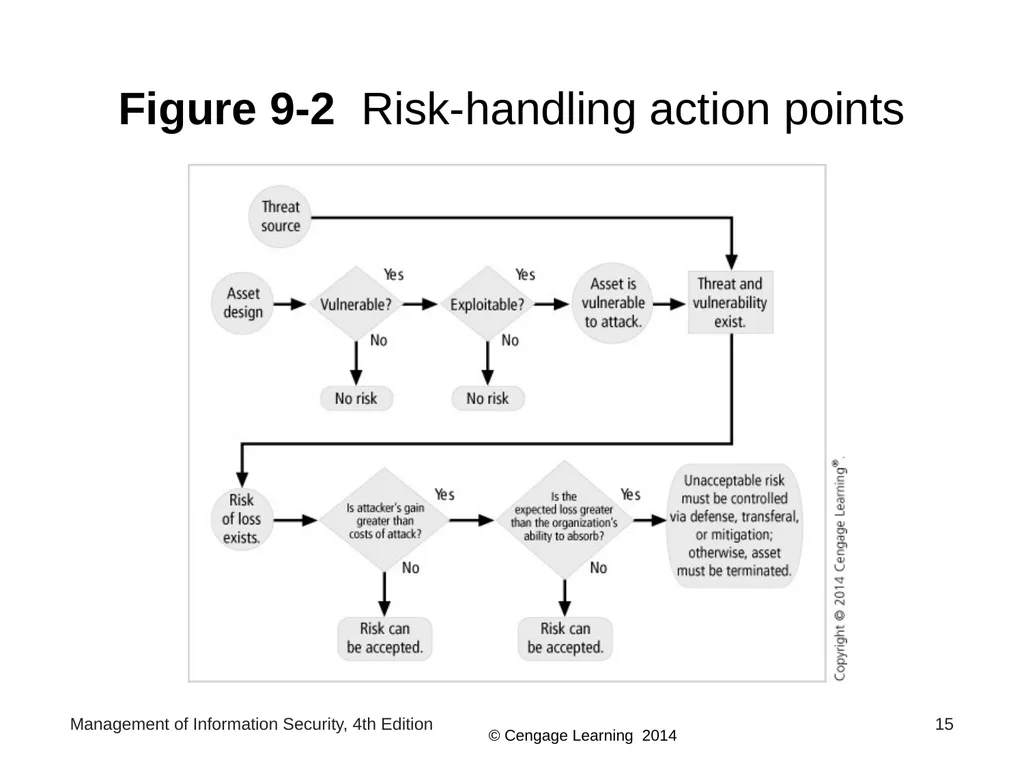
slide14. Managing Risk Part 3 Rules of thumb for selecting a strategy:
When a vulnerability exists in an important asset - implement security controls to reduced likelihood of a vulnerability being exploited
When a vulnerability can be exploited - apply layered protections, architectural designs, and administrative controls to minimize risk
When the attacker’s potential gain is greater than the costs of attack - apply protections to increase attacker’s cost
When the potential loss is substantial - apply technical and nontechnical protections to limit the extent of attack Management of Information Security, 4th Edition 14<br>
slide15. Figure 9-2 Risk-handling action points Management of Information Security, 4th Edition 15<br>
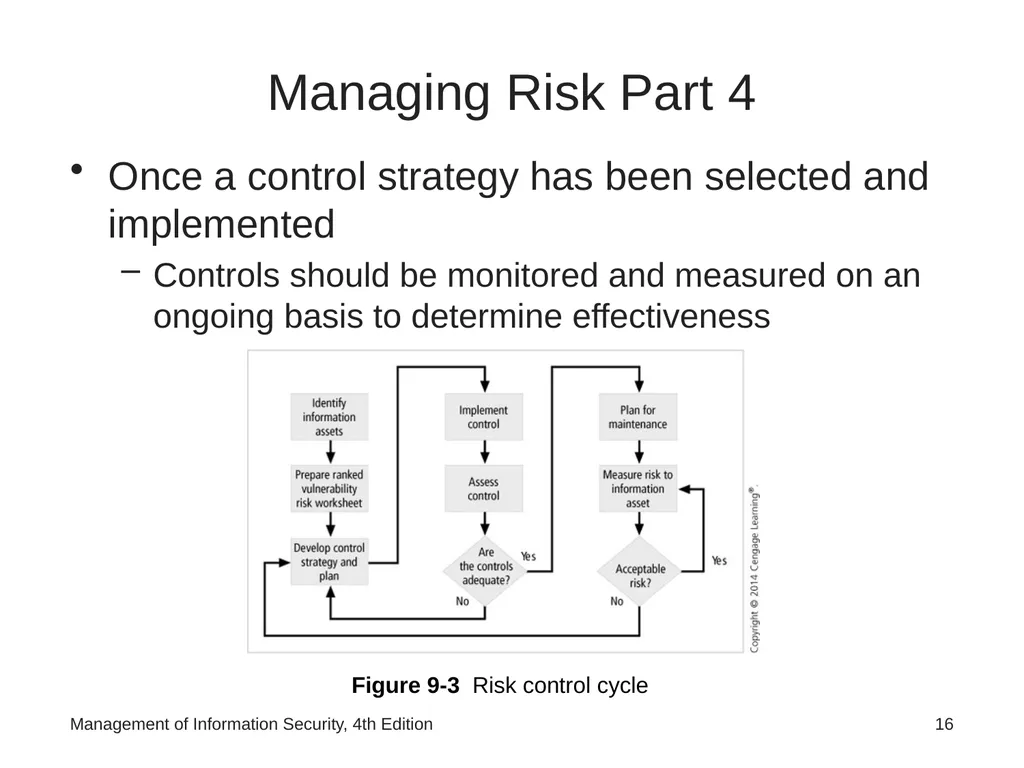
slide16. Managing Risk Part 4 Once a control strategy has been selected and implemented
Controls should be monitored and measured on an ongoing basis to determine effectiveness Figure 9-3 Risk control cycle Management of Information Security, 4th Edition 16<br>
slide17. Feasibility and Cost-Benefit Analysis Cost avoidance - the money saved by using the defense strategy via the implementation of control
Eliminating the financial ramifications of an incident
Before deciding on a strategy
An organization must explore all readily accessible information about the economic and noneconomic consequences of an exploitation of the vulnerability Management of Information Security, 4th Edition 17<br>
slide18. Cost-Benefit Analysis Economic feasibility - the most common criterion used when evaluating a strategy to implement InfoSec controls and safeguards
Economic feasibility analysis beings by valuing the information assets and determining the loss in value if those assets become compromised
Cost-benefit analysis (CBA) - A form of feasibility study that compares the life-cycle cost of implementing a control mechanism against the estimated economic benefit that would accrue from the implementation of the control Management of Information Security, 4th Edition 18<br>
slide19. Cost Items that affect the cost of a control or safeguard:
Cost of development or acquisition (hardware, software, and services)
Training fees (cost to train personnel)
Cost of implementation (installing, configuring, and testing hardware, software, and services)
Service costs (vendor fees for maintenance and upgrades)
Cost of maintenance (labor expense to verify and continually test, maintain, train, and update) Management of Information Security, 4th Edition 19<br>
slide20. Benefit Benefit - the value to the organization of using controls to prevent losses associated with a specific vulnerability
Usually determined by valuing the information asset or assets exposed by the vulnerability
Then determining how much of that value is at risk and how much risk exists for the asset
The result is expressed as the annualized loss expectancy (ALE) Management of Information Security, 4th Edition 20<br>
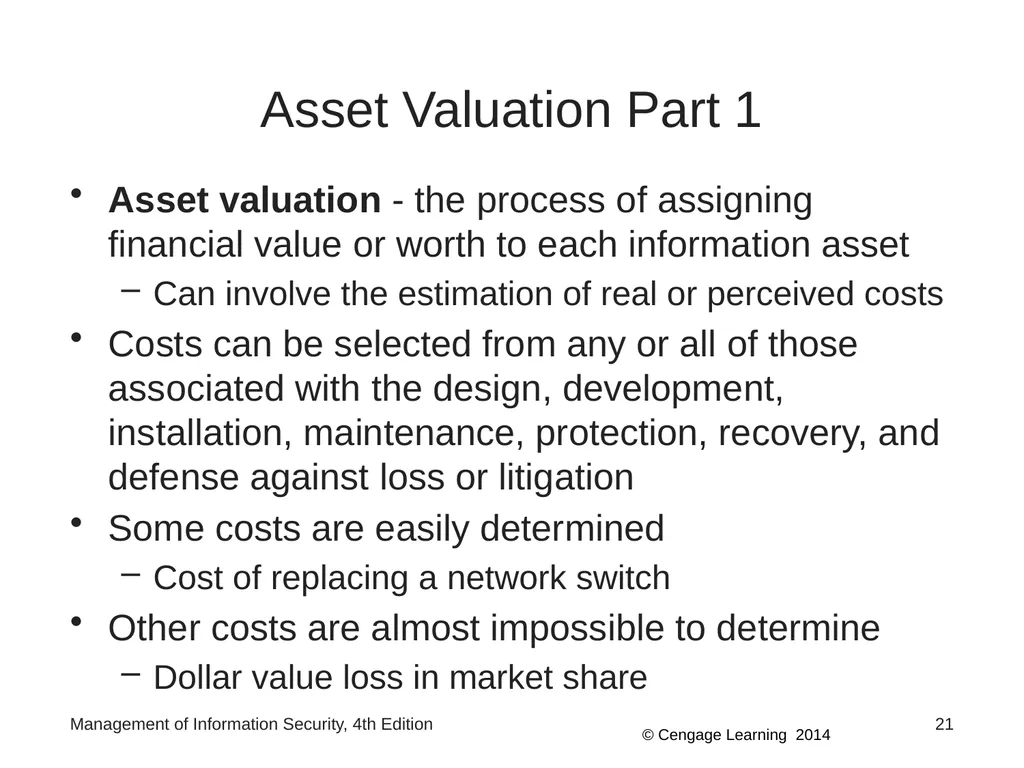
slide21. Asset Valuation Part 1 Asset valuation - the process of assigning financial value or worth to each information asset
Can involve the estimation of real or perceived costs
Costs can be selected from any or all of those associated with the design, development, installation, maintenance, protection, recovery, and defense against loss or litigation
Some costs are easily determined
Cost of replacing a network switch
Other costs are almost impossible to determine
Dollar value loss in market share Management of Information Security, 4th Edition 21<br>
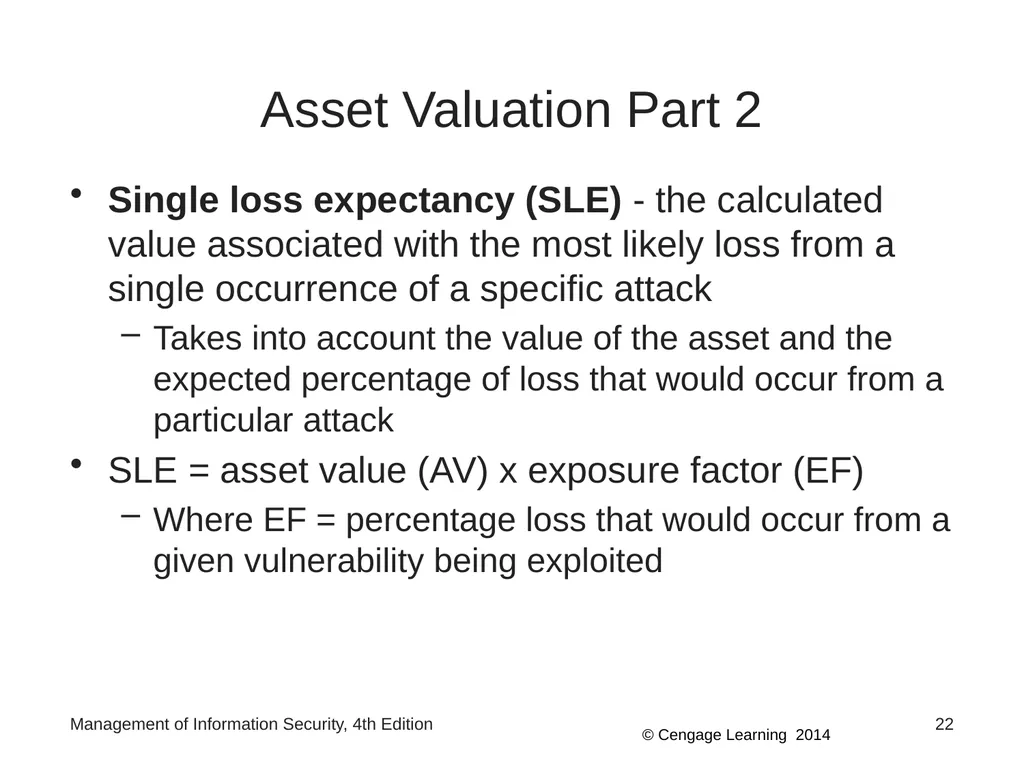
slide22. Asset Valuation Part 2 Single loss expectancy (SLE) - the calculated value associated with the most likely loss from a single occurrence of a specific attack
Takes into account the value of the asset and the expected percentage of loss that would occur from a particular attack
SLE = asset value (AV) x exposure factor (EF)
Where EF = percentage loss that would occur from a given vulnerability being exploited Management of Information Security, 4th Edition 22<br>
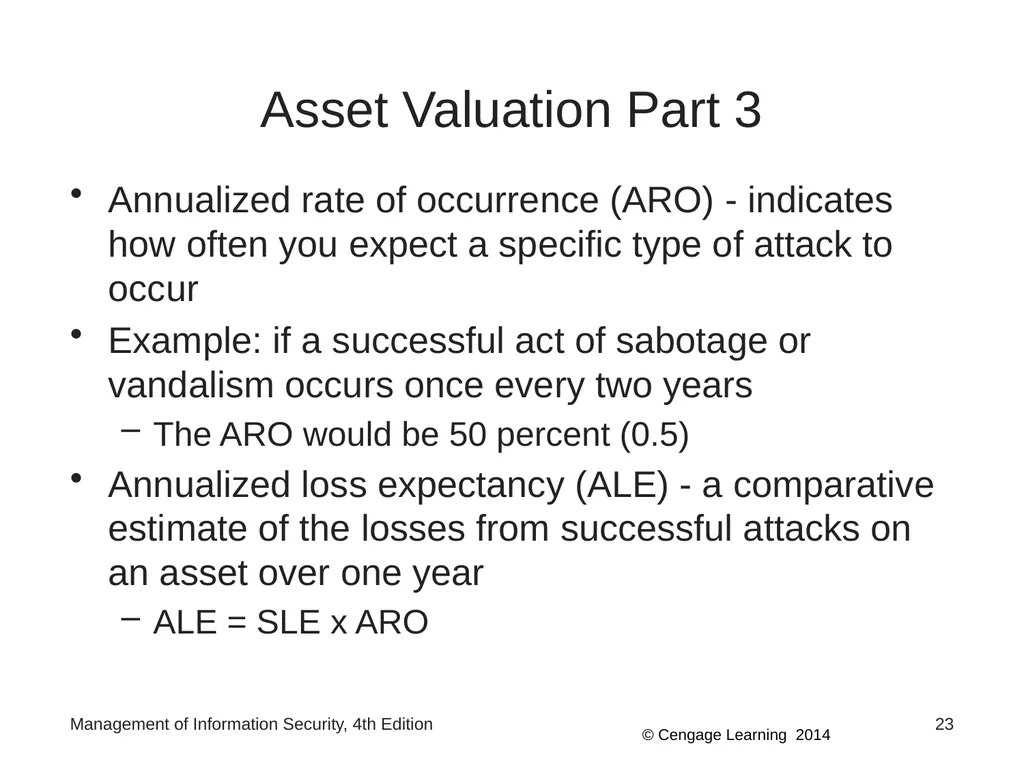
slide23. Asset Valuation Part 3 Annualized rate of occurrence (ARO) - indicates how often you expect a specific type of attack to occur
Example: if a successful act of sabotage or vandalism occurs once every two years
The ARO would be 50 percent (0.5)
Annualized loss expectancy (ALE) - a comparative estimate of the losses from successful attacks on an asset over one year
ALE = SLE x ARO Management of Information Security, 4th Edition 23<br>
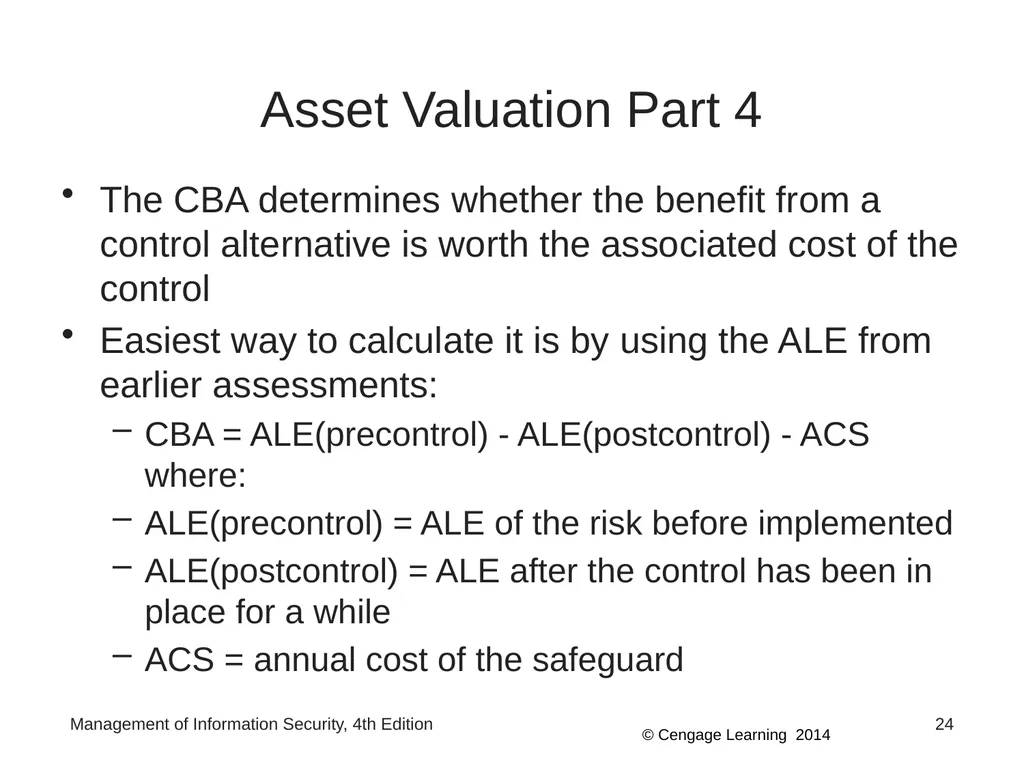
slide24. Asset Valuation Part 4 The CBA determines whether the benefit from a control alternative is worth the associated cost of the control
Easiest way to calculate it is by using the ALE from earlier assessments:
CBA = ALE(precontrol) - ALE(postcontrol) - ACS where:
ALE(precontrol) = ALE of the risk before implemented
ALE(postcontrol) = ALE after the control has been in place for a while
ACS = annual cost of the safeguard Management of Information Security, 4th Edition 24<br>
slide25. Other Methods of Establishing Feasibility The next step in measuring how ready an organization is for the introduction of controls is to determine the proposal’s:
Organizational feasibility
Operational feasibility
Technical feasibility
Political feasibility Management of Information Security, 4th Edition 25<br>
slide26. Organizational Feasibility Organizational feasibility - examines how well the proposed InfoSec alternatives will contribute to the efficiency, effectiveness, and overall operation of an organization
The proposed control approach must contribute to the organization’s strategic objectives
The organization should not invest in technology that changes its fundamental ability to explore certain avenues and opportunities Management of Information Security, 4th Edition 26<br>
slide27. Operational Feasibility Operational feasibility - refers to user acceptance and support, management acceptance and support, and the system’s compatibility with the requirements of the organization’s stakeholders
Also known as behavioral feasibility
If users do not accept a new technology, policy, or program, it will eventually fail
Communication, education, and involvement can reduce resistance to change Management of Information Security, 4th Edition 27<br>
slide28. Technical Feasibility Technical feasibility - determining whether an organization already has or can acquire the technology necessary to implement and support them
Also examines whether an organization has the technological expertise to manage the new technology Management of Information Security, 4th Edition 28<br>
slide29. Political Feasibility Political feasibility - considers what can and cannot occur based on the consensus and relationships among the communities of interest
Limits imposed by InfoSec controls must fit within the realm of the possible before they can be effectively implemented
That realm includes the availability of staff resources Management of Information Security, 4th Edition 29<br>
slide30. Alternatives to Feasibility Analysis List of alternatives to using CBA:
Benchmarking is the process of seeking out and studying the practices used in other organizations that produce results you desire
Due care and due diligence occur when an organization adopts a certain minimum level of security
Best business practices are considered those thought to be among the best in the industry
The gold standard is for those ambitious organizations in which the best business practices are not sufficient Management of Information Security, 4th Edition 30<br>
slide31. Alternatives to Feasibility Analysis (continued) List of alternatives to using CBA (cont’d):
Government recommendations and best practices are useful for organizations that operate in industries regulated by governmental agencies
A baseline is derived by comparing measured actual performance against established standards for the measured category Management of Information Security, 4th Edition 31<br>
slide32. Microsoft Risk Management Approach Microsoft asserts that risk management is not a stand-alone subject
Should be part of a general governance program
Microsoft presents four phases in its security risk management process:
Assessing risk
Conducting decision support
Implementing controls
Measuring program effectiveness Management of Information Security, 4th Edition 32<br>
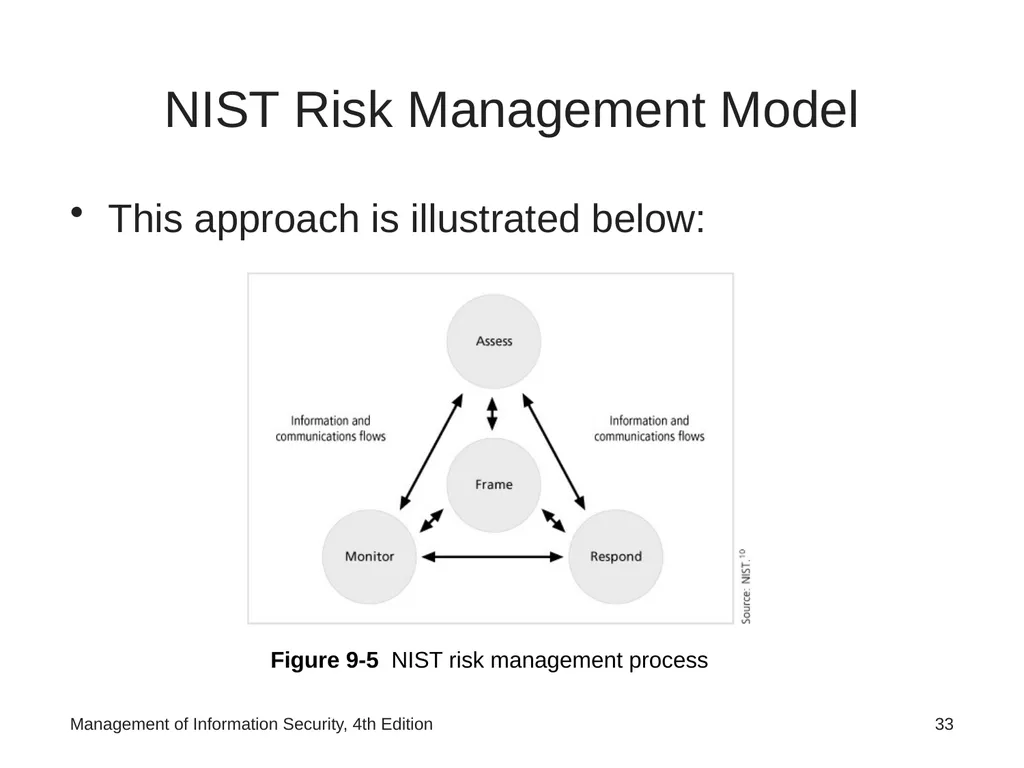
slide33. NIST Risk Management Model This approach is illustrated below: Figure 9-5 NIST risk management process Management of Information Security, 4th Edition 33<br>
slide34. Summary Part 1 Once vulnerabilities are identified and ranked, a strategy to control the risks must be chosen
Economic feasibility studies determine and compare costs and benefits from potential controls
An organization must be able to place a dollar value on each collection of information and information assets it owns
Single loss expectancy (SLE) is calculated from the value of the asset and the expected percentage of loss that would occur from a single successful attack Management of Information Security, 4th Edition 34<br>
slide35. Summary Part 2 Cost-benefit analysis (CBA) determines whether a control alternative is worth its associated cost
Organizations may choose alternatives to feasibility studies to justify applying InfoSec controls
Risk appetite defines the quantity and nature of risk that organizations are willing to accept as they evaluate the trade-offs between perfect security and unlimited accessibility
It is possible to repeat risk analysis using estimates based on a qualitative assessment Management of Information Security, 4th Edition 35<br>
Risk Management: Controlling Risk<br>
slide2. Objectives Recognize the strategy options used to control risk and be prepared to select from them when given background information
Evaluate risk controls and formulate a cost-benefit analysis (CBA) using existing conceptual frameworks
Explain how to maintain and perpetuate risk controls
Describe popular approaches used in the industry to manage risk Management of Information Security, 4th Edition 2<br>
slide3. Risk Control Strategies Once the InfoSec development team has created the ranked vulnerability worksheet, the team must choose one of five basic control strategies:
Defense
Transferal
Mitigation
Acceptance
Termination Management of Information Security, 4th Edition 3<br>
slide4. Defense Defense risk control strategy - attempts to prevent the exploitation of the vulnerability
Accomplished by means of countering threats, removing vulnerabilities in assets, limiting access to assets, and adding protective safeguards
Sometimes referred to as avoidance
Three common methods of risk defense:
Application of policy
Application of training and education
Implementation of technology Management of Information Security, 4th Edition 4<br>
slide5. Transferal Transferal risk control strategy - attempts to shift the risk to other assets, other processes, or other organizations
May be accomplished by:
Rethinking how services are offered
Revising deployment models
Outsourcing to other organizations
Purchasing insurance
Implementing service contracts with providers Management of Information Security, 4th Edition 5<br>
slide6. Mitigation Mitigation risk control strategy - attempts to reduce the damage caused by a realized incident or disaster
By means of planning and preparation
Includes three types of plans
Incident response (IR) plan
Disaster recovery (DR) plan
Business continuity (BC) plan
Mitigation depends on the ability to detect and respond to an attack as quickly as possible Management of Information Security, 4th Edition 6<br>
slide7. Table 9-1 Summary of mitigation plans Management of Information Security, 4th Edition 7<br>
slide8. Acceptance Acceptance risk control strategy - the decision to do nothing to protect an information asset from risk and accept the outcome
Acceptance is recognized as a valid strategy only when the organization has:
Determined the level of risk posed to the information asset
Assessed the probability of attack and the likelihood of a successful exploitation of a vulnerability
Estimated the potential damage or loss that could result from attacks Management of Information Security, 4th Edition 8<br>
slide9. Acceptance (continued) Acceptance is recognized as a valid strategy only when the organization has (cont’d):
Evaluated potential controls using each appropriate type of feasibility
Performed a thorough CBA
Determined that the costs to control the risk to a particular function, service, collection of data, or information asset do not justify the cost of implementing and maintaining controls
Strategy should be implemented when the cost of protecting an asset does not justify the expense Management of Information Security, 4th Edition 9<br>
slide10. Termination Termination risk control strategy - based on the organization’s need or choice not to protect an asset
The organization does not wish the asset to remain at risk so it is removed form the environment that represents risk
Termination must be a conscious business decision
Not simply the abandonment of an asset
Would technically qualify as acceptance Management of Information Security, 4th Edition 10<br>
slide11. Managing Risk Part 1 Risk appetite - the quantity and nature of risk that organizations are willing to accept
As they evaluate the trade-offs between perfect security and unlimited accessibility
Also known as risk tolerance
The key is for the organization to find balance in its decision-making processes and in its feasibility analyses
Assuring that its risk appetite is based on experience and facts, not on ignorance and wishful thinking Management of Information Security, 4th Edition 11<br>
slide12. Managing Risk Part 2 Residual risk is the amount of risk that remains after the organization has implemented policy, education and training, and technical controls and safeguards
The goal of InfoSec is not to bring residual risk to zero
It is to bring residual risk in line with an organization’s risk appetite Management of Information Security, 4th Edition 12<br>
slide13. Figure 9-1 Residual risk Management of Information Security, 4th Edition 13<br>
slide14. Managing Risk Part 3 Rules of thumb for selecting a strategy:
When a vulnerability exists in an important asset - implement security controls to reduced likelihood of a vulnerability being exploited
When a vulnerability can be exploited - apply layered protections, architectural designs, and administrative controls to minimize risk
When the attacker’s potential gain is greater than the costs of attack - apply protections to increase attacker’s cost
When the potential loss is substantial - apply technical and nontechnical protections to limit the extent of attack Management of Information Security, 4th Edition 14<br>
slide15. Figure 9-2 Risk-handling action points Management of Information Security, 4th Edition 15<br>
slide16. Managing Risk Part 4 Once a control strategy has been selected and implemented
Controls should be monitored and measured on an ongoing basis to determine effectiveness Figure 9-3 Risk control cycle Management of Information Security, 4th Edition 16<br>
slide17. Feasibility and Cost-Benefit Analysis Cost avoidance - the money saved by using the defense strategy via the implementation of control
Eliminating the financial ramifications of an incident
Before deciding on a strategy
An organization must explore all readily accessible information about the economic and noneconomic consequences of an exploitation of the vulnerability Management of Information Security, 4th Edition 17<br>
slide18. Cost-Benefit Analysis Economic feasibility - the most common criterion used when evaluating a strategy to implement InfoSec controls and safeguards
Economic feasibility analysis beings by valuing the information assets and determining the loss in value if those assets become compromised
Cost-benefit analysis (CBA) - A form of feasibility study that compares the life-cycle cost of implementing a control mechanism against the estimated economic benefit that would accrue from the implementation of the control Management of Information Security, 4th Edition 18<br>
slide19. Cost Items that affect the cost of a control or safeguard:
Cost of development or acquisition (hardware, software, and services)
Training fees (cost to train personnel)
Cost of implementation (installing, configuring, and testing hardware, software, and services)
Service costs (vendor fees for maintenance and upgrades)
Cost of maintenance (labor expense to verify and continually test, maintain, train, and update) Management of Information Security, 4th Edition 19<br>
slide20. Benefit Benefit - the value to the organization of using controls to prevent losses associated with a specific vulnerability
Usually determined by valuing the information asset or assets exposed by the vulnerability
Then determining how much of that value is at risk and how much risk exists for the asset
The result is expressed as the annualized loss expectancy (ALE) Management of Information Security, 4th Edition 20<br>
slide21. Asset Valuation Part 1 Asset valuation - the process of assigning financial value or worth to each information asset
Can involve the estimation of real or perceived costs
Costs can be selected from any or all of those associated with the design, development, installation, maintenance, protection, recovery, and defense against loss or litigation
Some costs are easily determined
Cost of replacing a network switch
Other costs are almost impossible to determine
Dollar value loss in market share Management of Information Security, 4th Edition 21<br>
slide22. Asset Valuation Part 2 Single loss expectancy (SLE) - the calculated value associated with the most likely loss from a single occurrence of a specific attack
Takes into account the value of the asset and the expected percentage of loss that would occur from a particular attack
SLE = asset value (AV) x exposure factor (EF)
Where EF = percentage loss that would occur from a given vulnerability being exploited Management of Information Security, 4th Edition 22<br>
slide23. Asset Valuation Part 3 Annualized rate of occurrence (ARO) - indicates how often you expect a specific type of attack to occur
Example: if a successful act of sabotage or vandalism occurs once every two years
The ARO would be 50 percent (0.5)
Annualized loss expectancy (ALE) - a comparative estimate of the losses from successful attacks on an asset over one year
ALE = SLE x ARO Management of Information Security, 4th Edition 23<br>
slide24. Asset Valuation Part 4 The CBA determines whether the benefit from a control alternative is worth the associated cost of the control
Easiest way to calculate it is by using the ALE from earlier assessments:
CBA = ALE(precontrol) - ALE(postcontrol) - ACS where:
ALE(precontrol) = ALE of the risk before implemented
ALE(postcontrol) = ALE after the control has been in place for a while
ACS = annual cost of the safeguard Management of Information Security, 4th Edition 24<br>
slide25. Other Methods of Establishing Feasibility The next step in measuring how ready an organization is for the introduction of controls is to determine the proposal’s:
Organizational feasibility
Operational feasibility
Technical feasibility
Political feasibility Management of Information Security, 4th Edition 25<br>
slide26. Organizational Feasibility Organizational feasibility - examines how well the proposed InfoSec alternatives will contribute to the efficiency, effectiveness, and overall operation of an organization
The proposed control approach must contribute to the organization’s strategic objectives
The organization should not invest in technology that changes its fundamental ability to explore certain avenues and opportunities Management of Information Security, 4th Edition 26<br>
slide27. Operational Feasibility Operational feasibility - refers to user acceptance and support, management acceptance and support, and the system’s compatibility with the requirements of the organization’s stakeholders
Also known as behavioral feasibility
If users do not accept a new technology, policy, or program, it will eventually fail
Communication, education, and involvement can reduce resistance to change Management of Information Security, 4th Edition 27<br>
slide28. Technical Feasibility Technical feasibility - determining whether an organization already has or can acquire the technology necessary to implement and support them
Also examines whether an organization has the technological expertise to manage the new technology Management of Information Security, 4th Edition 28<br>
slide29. Political Feasibility Political feasibility - considers what can and cannot occur based on the consensus and relationships among the communities of interest
Limits imposed by InfoSec controls must fit within the realm of the possible before they can be effectively implemented
That realm includes the availability of staff resources Management of Information Security, 4th Edition 29<br>
slide30. Alternatives to Feasibility Analysis List of alternatives to using CBA:
Benchmarking is the process of seeking out and studying the practices used in other organizations that produce results you desire
Due care and due diligence occur when an organization adopts a certain minimum level of security
Best business practices are considered those thought to be among the best in the industry
The gold standard is for those ambitious organizations in which the best business practices are not sufficient Management of Information Security, 4th Edition 30<br>
slide31. Alternatives to Feasibility Analysis (continued) List of alternatives to using CBA (cont’d):
Government recommendations and best practices are useful for organizations that operate in industries regulated by governmental agencies
A baseline is derived by comparing measured actual performance against established standards for the measured category Management of Information Security, 4th Edition 31<br>
slide32. Microsoft Risk Management Approach Microsoft asserts that risk management is not a stand-alone subject
Should be part of a general governance program
Microsoft presents four phases in its security risk management process:
Assessing risk
Conducting decision support
Implementing controls
Measuring program effectiveness Management of Information Security, 4th Edition 32<br>
slide33. NIST Risk Management Model This approach is illustrated below: Figure 9-5 NIST risk management process Management of Information Security, 4th Edition 33<br>
slide34. Summary Part 1 Once vulnerabilities are identified and ranked, a strategy to control the risks must be chosen
Economic feasibility studies determine and compare costs and benefits from potential controls
An organization must be able to place a dollar value on each collection of information and information assets it owns
Single loss expectancy (SLE) is calculated from the value of the asset and the expected percentage of loss that would occur from a single successful attack Management of Information Security, 4th Edition 34<br>
slide35. Summary Part 2 Cost-benefit analysis (CBA) determines whether a control alternative is worth its associated cost
Organizations may choose alternatives to feasibility studies to justify applying InfoSec controls
Risk appetite defines the quantity and nature of risk that organizations are willing to accept as they evaluate the trade-offs between perfect security and unlimited accessibility
It is possible to repeat risk analysis using estimates based on a qualitative assessment Management of Information Security, 4th Edition 35<br>