SIEM and Splunk SIBI M S Solution and Tools Incident Ticketing: Atlassian Jira, Azure Desk, Zoho Desk, etc.,. Version Control: Git, BitBucket, Azure Repo, etc.,. CICD: Jenkins, GitLab, etc.,. SIEM Security Information and Event management
"SIEM and Splunk SIBI M S Solution and Tools" is the property of its rightful owner. Permission is granted to
download and print the materials on this website for personal, non-commercial use only, and to display it
on your personal computer provided you do not modify the materials and that you retain all copyright
notices contained in the materials. By downloading content from our website, you accept the terms of this
agreement.
What problem SIEM solves? Credential Breach
Suspicious Internal Activities of an organization.
Overloading Alerts<br>
07
SIEM Providers Log Rhythm
Splunk>
IBM
Sentinel by Azure
Elastic Slack<br>
08
Splunk> Security Service Provider.
Monitors Log Data.<br>
09
Splunk into SIEM Perform Real-Time Analysis using SIM & SEM.
Collect the data with SIM.
Identify Patterns & use SEM to automate alerts or other functions.<br>
10
Why Splunk? As per Gartner Report, Splunk stands out above other tools for SIEM.
Analysis made easy.
Hassle free Installation over cloud, on-premises or hybrid.<br>
11
Realtime Incident 6 Years Ago, a security team working with real-time maps of Geo Location needs to respond within 10 minutes of Malware Arrival.
They used SQL Mirrors for storing geo-locations.
Splunk used by them to detect the failed SQL Mirror that SQL does.<br>
12
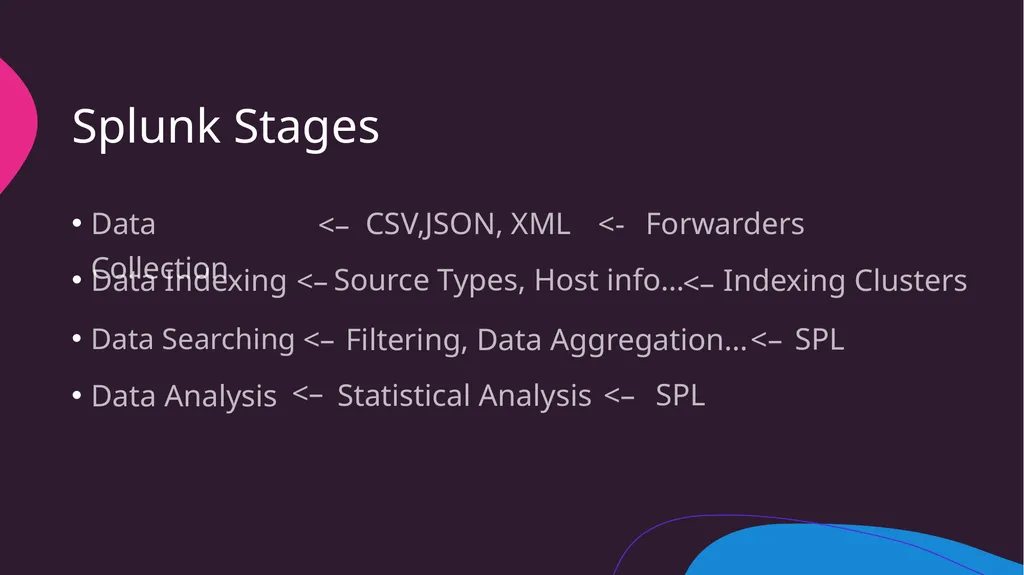
Splunk Stages Data Collection Data Indexing <– CSV,JSON, XML <- Forwarders Data Searching Indexing Clusters Source Types, Host info… <– <– Data Analysis SPL Filtering, Data Aggregation… <– <– SPL Statistical Analysis <– <–<br>
13
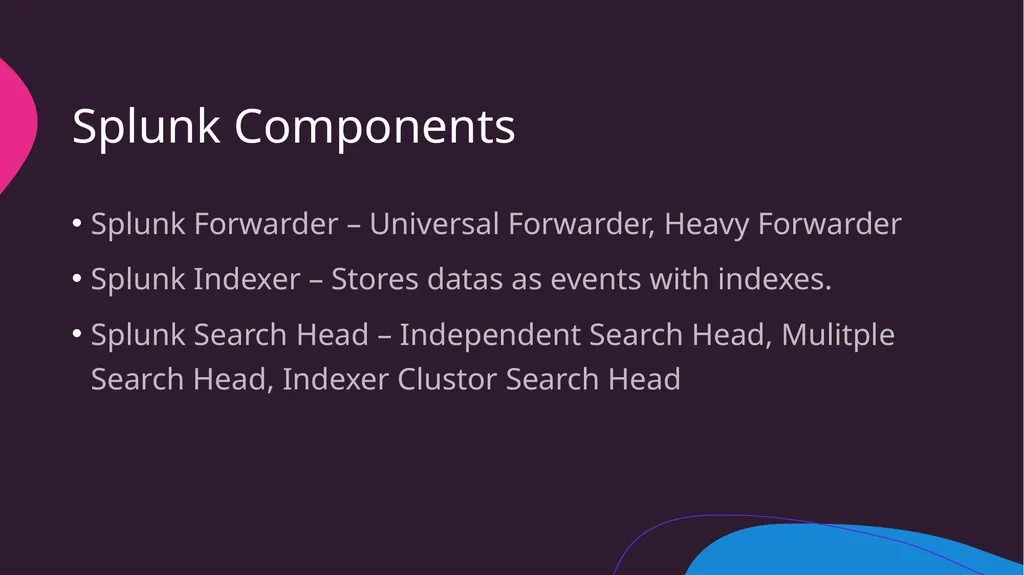
Splunk Components Splunk Forwarder – Universal Forwarder, Heavy Forwarder
Splunk Indexer – Stores datas as events with indexes.
Splunk Search Head – Independent Search Head, Mulitple Search Head, Indexer Clustor Search Head<br>
14
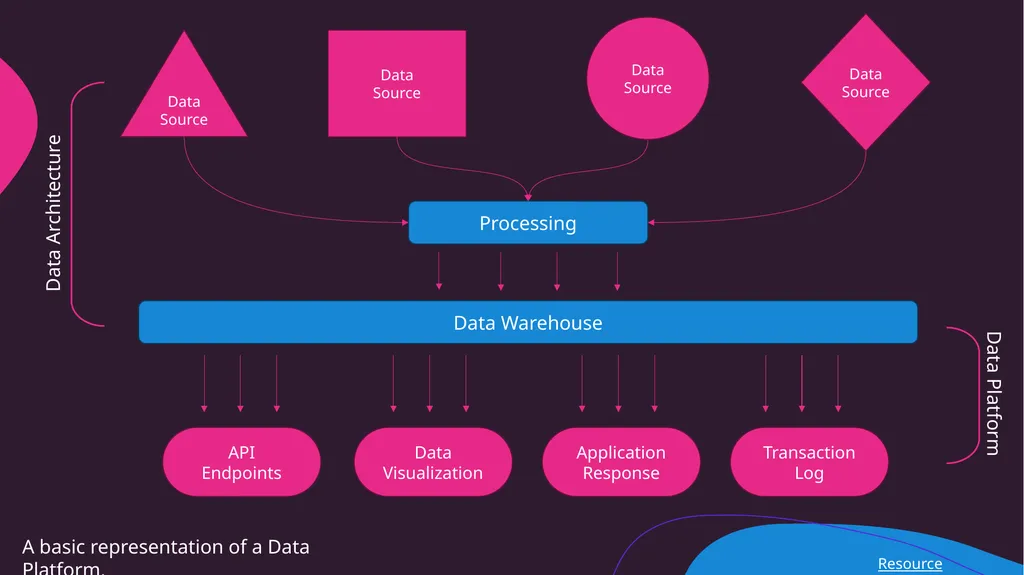
Data
Source Data
Source Data
Source Data
Source Processing Data Warehouse Data
Visualization API
Endpoints Application
Response Transaction
Log Data Architecture Data Platform A basic representation of a Data Platform. Resource<br>
15
Conclusion SIEM is neither a tool nor a software.
Data and Log Watcher.<br>
16
“A tool with a fool is still a fool.” - Grady Booch<br>
17
Reference SIEM vs SOC | Mezmo
What is SIEM? | Varonis
What Does It Do? | Splunk
SIEM, Splunk | CPrime<br>