
MoD Accessibility and Trust: Challenges, Goals and
JO
Published · 22 slides · 0 views
1 / 1
Description
MoD Accessibility and Trust: Challenges, Goals and a Success Story Dr Jane Jensen Deputy Head Identity Privilege Management CIO Information Strategy Policy 30 September 2009 2 AGENDA Challenges facing the MoD Strategic Goals Enabling
Related Topics
Share
Embed code
Download this presentation From Below
"MoD Accessibility and Trust: Challenges, Goals and" is the property of its rightful owner. Permission is granted to download and print the materials on this website for personal, non-commercial use only, and to display it on your personal computer provided you do not modify the materials and that you retain all copyright notices contained in the materials. By downloading content from our website, you accept the terms of this agreement.
Presentation Transcript
01
MoD Accessibility and Trust:
Challenges, Goals and
a Success Story Dr Jane Jensen
Deputy Head Identity & Privilege Management
CIO Information Strategy & Policy
30 September 2009<br>
Deputy Head Identity & Privilege Management
CIO Information Strategy & Policy
30 September 2009<br>
02
2 AGENDA Challenges facing the MoD
Strategic Goals
Enabling Capabilities
Federated Approach
A success story<br>
Strategic Goals
Enabling Capabilities
Federated Approach
A success story<br>
03
MoD Challenges Enable collaboration and information sharing with Partners (Allies, Other Government Departments and Industry)
Trusted access to MOD services by Partners
MOD access to external Partner services
Enable a more agile and flexible workforce
Work anywhere, easily, at the user’s convenience
Access to online services by MOD “orphans”
Protect business and personal information
Deliver higher value for money
Shared services
Increased productivity
Reduced support costs 3<br>
04
Identity and Access Management – Strategic Goals Provide a federated Identity Management service
Provide common services for attribute-based authentication and authorisation
Establish federation agreements with Partners
Exploit services to realise operational, business and financial benefits 4<br>
Provide common services for attribute-based authentication and authorisation
Establish federation agreements with Partners
Exploit services to realise operational, business and financial benefits 4<br>
05
Enabling Capabilities A number of ongoing MOD programmes will provide enabling capabilities to support delivery of the goals:
Defence Multi-Application Smart Card (DMASC)
Defence Public Key Infrastructure (DPKI)
Transglobal Secure collaboration Program (TSCP)<br>
Defence Multi-Application Smart Card (DMASC)
Defence Public Key Infrastructure (DPKI)
Transglobal Secure collaboration Program (TSCP)<br>
06
Defence Multi-Application Smart Card (DMASC) Common access card will provide ID, physical access to sites and electronic access to MOD information systems incorporating:
Photograph, service, rank, name, expiry date
Legic chip for physical access
Contact chip containing three assemblies:
EMV - used for Internet access to MOD HR services
PKI - storage of digital certificates
Common PIN policy
Bar code – for possible use in operational location tracking
Unique serial number
Security features 6<br>
07
Defence Public Key Infrastructure (DPKI) DPKI service will issue certificates to identify an entity (person, role or device) named in the certificate and state what the certificate (and corresponding public key) can be used for
Such uses could include:
Authentication of users to applications and infrastructure
Message signing and/or encryption
Signing and/or encryption of electronic forms, files or contracts
Authentication of infrastructure devices and services such as Routers, Web Servers, Firewalls, VPNs and Directories
Support for auditing and accountability 7<br>
08
TSCP TSCP is a cooperative forum in which Aerospace and Defence (A&D) companies and government agencies work together to establish and maintain an open standards-based framework for federated collaboration and information sharing
UK MOD is founder member 8 See: www.TSCP.org for more details<br>
UK MOD is founder member 8 See: www.TSCP.org for more details<br>
09
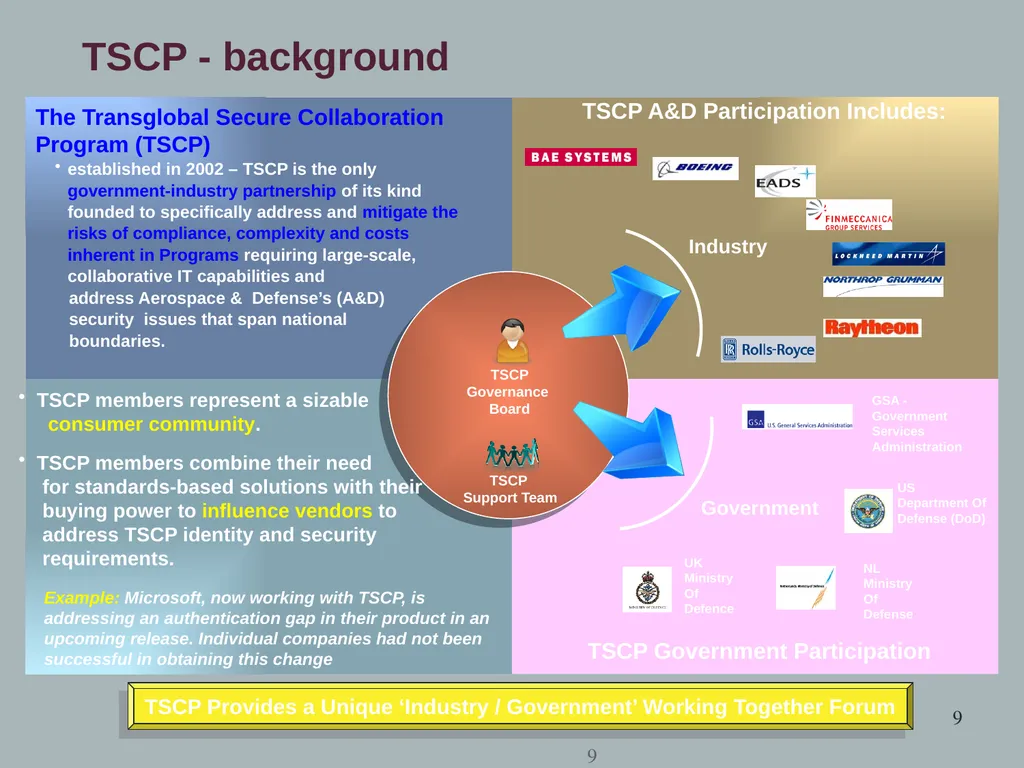
TSCP - background 9 9 The Transglobal Secure Collaboration Program (TSCP)
established in 2002 – TSCP is the only government-industry partnership of its kind founded to specifically address and mitigate the risks of compliance, complexity and costs inherent in Programs requiring large-scale, collaborative IT capabilities and
address Aerospace & Defense’s (A&D)
security issues that span national
boundaries. TSCP
Governance
Board TSCP
Support Team TSCP Provides a Unique ‘Industry / Government’ Working Together Forum TSCP members represent a sizable
consumer community.
TSCP members combine their need
for standards-based solutions with their
buying power to influence vendors to
address TSCP identity and security
requirements.
Example: Microsoft, now working with TSCP, is addressing an authentication gap in their product in an upcoming release. Individual companies had not been successful in obtaining this change<br>
10
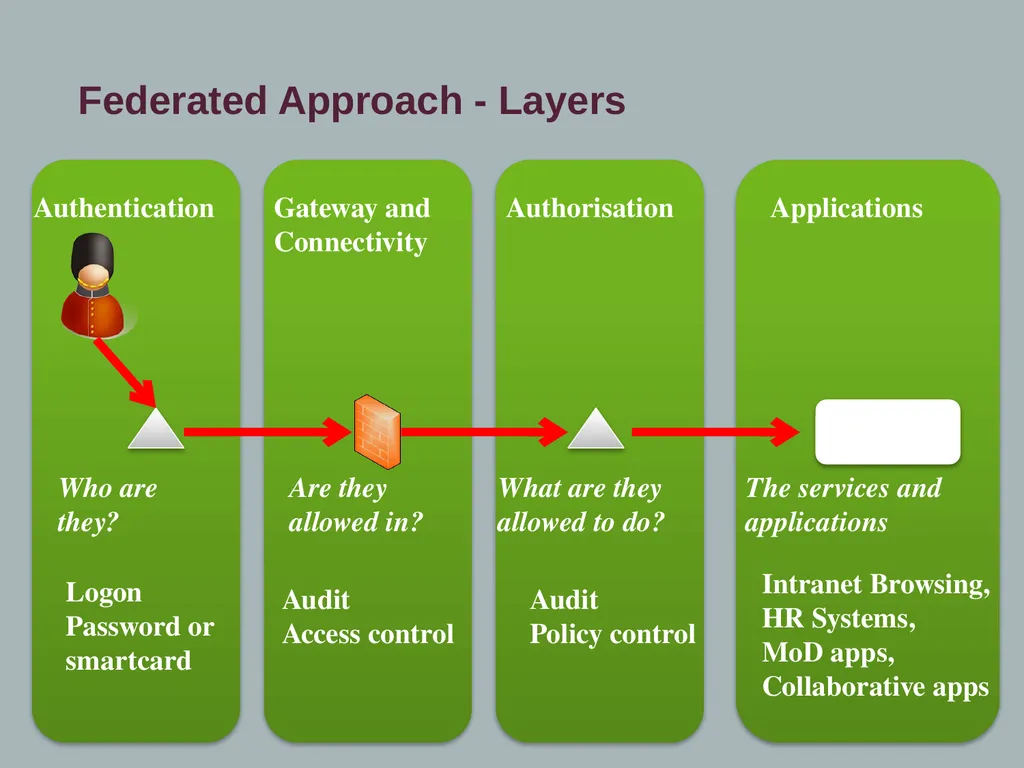
Federated Approach - Layers 10 Applications Authorisation Gateway and Connectivity Authentication Audit
Access control Audit
Policy control Intranet Browsing,
HR Systems,
MoD apps,
Collaborative apps Logon
Password or smartcard Who are they? Are they allowed in? What are they allowed to do? The services and applications<br>
Access control Audit
Policy control Intranet Browsing,
HR Systems,
MoD apps,
Collaborative apps Logon
Password or smartcard Who are they? Are they allowed in? What are they allowed to do? The services and applications<br>
11
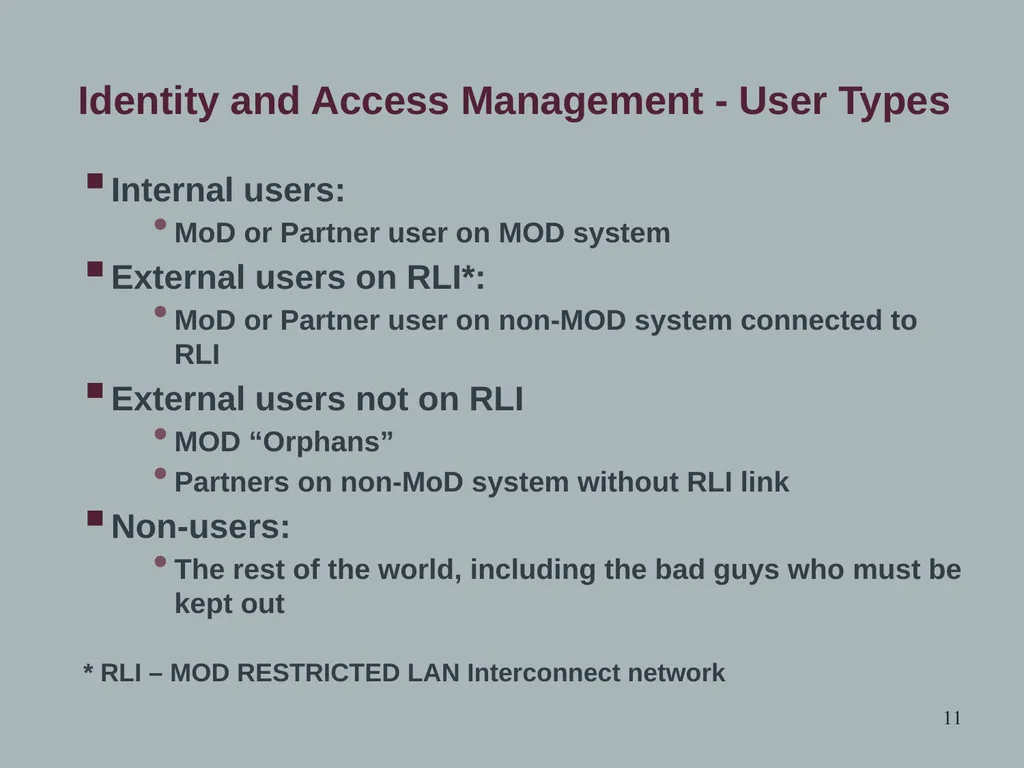
Identity and Access Management - User Types Internal users:
MoD or Partner user on MOD system
External users on RLI*:
MoD or Partner user on non-MOD system connected to RLI
External users not on RLI
MOD “Orphans”
Partners on non-MoD system without RLI link
Non-users:
The rest of the world, including the bad guys who must be kept out
* RLI – MOD RESTRICTED LAN Interconnect network 11<br>
12
Federated Approach – Incremental Delivery Small steps to the full Federated Collaboration environment to:
Achieve early benefits
Exploit services as they become available
Manage risks
Progressively add services:
User Authentication:
Accept tokens from Trusted Partners
Provide MoD Authentication Service
Authorisation:
Use claims (trusted user attributes) to control access<br>
Achieve early benefits
Exploit services as they become available
Manage risks
Progressively add services:
User Authentication:
Accept tokens from Trusted Partners
Provide MoD Authentication Service
Authorisation:
Use claims (trusted user attributes) to control access<br>
13
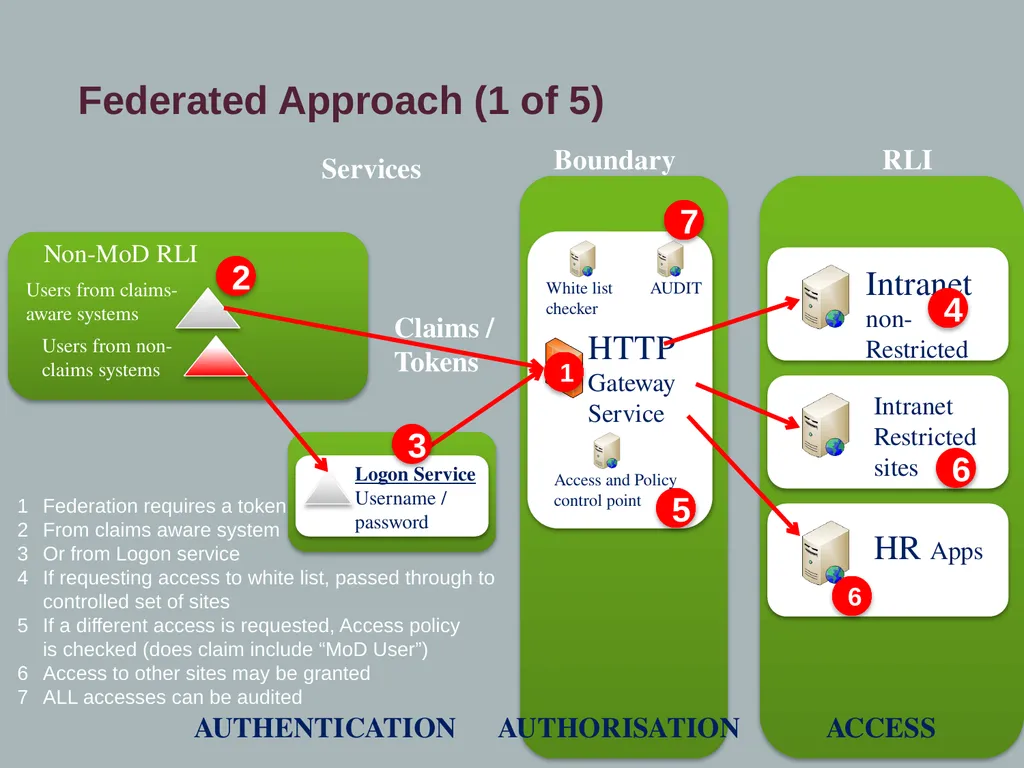
Federated Approach (1 of 5) 13 RLI Intranet non-Restricted Intranet Restricted sites Intranet non-Restricted Boundary HTTP
Gateway
Service White list checker AUDIT Access and Policy control point Services Logon Service
Username /
password Non-MoD RLI Users from claims-aware systems Users from non-claims systems Claims / Tokens Federation requires a token
From claims aware system
Or from Logon service
If requesting access to white list, passed through to controlled set of sites
If a different access is requested, Access policy is checked (does claim include “MoD User”)
Access to other sites may be granted
ALL accesses can be audited 1 2 3 4 5 6 7 HR Apps 6 AUTHENTICATION AUTHORISATION ACCESS<br>
14
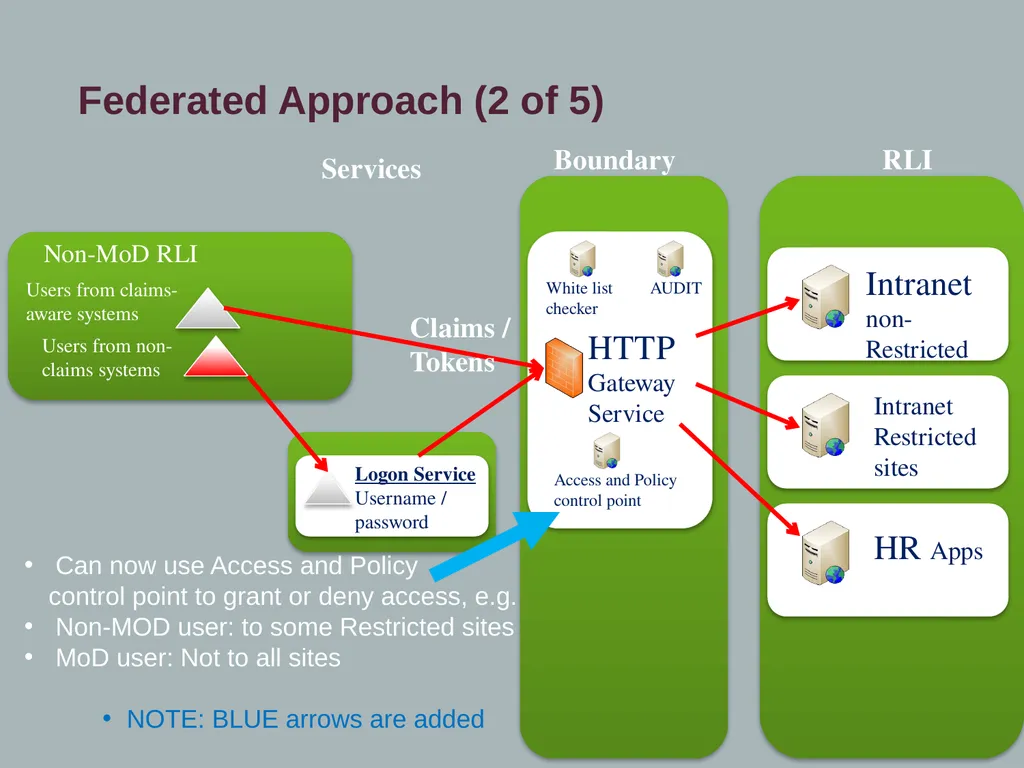
Federated Approach (2 of 5) 14 RLI Intranet non-Restricted Boundary Services Non-MoD RLI Users from claims-aware systems Users from non-claims systems Claims / Tokens Can now use Access and Policy
control point to grant or deny access, e.g.
Non-MOD user: to some Restricted sites
MoD user: Not to all sites
NOTE: BLUE arrows are added Intranet Restricted sites Intranet non-Restricted HTTP Gateway Service White list checker AUDIT Access and Policy control point Logon Service Username / password HR Apps<br>
Non-MOD user: to some Restricted sites
MoD user: Not to all sites
NOTE: BLUE arrows are added Intranet Restricted sites Intranet non-Restricted HTTP Gateway Service White list checker AUDIT Access and Policy control point Logon Service Username / password HR Apps<br>
15
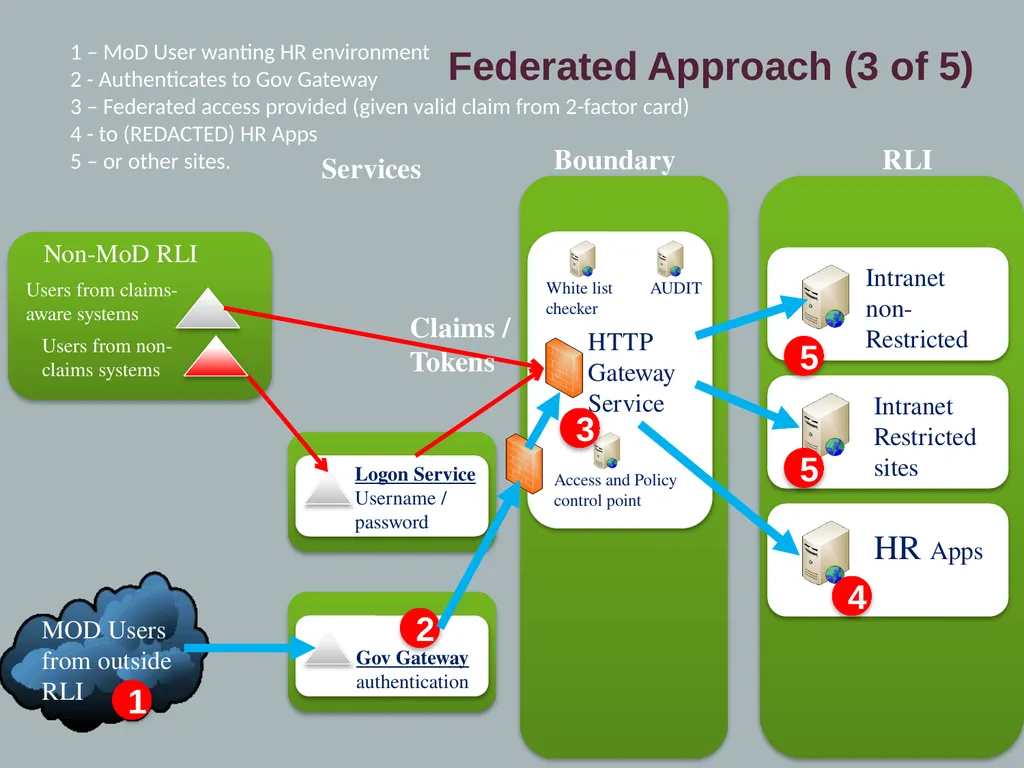
Federated Approach (3 of 5) 15 RLI Intranet non-Restricted Intranet Restricted sites HR Apps Intranet non-Restricted % Boundary HTTP
Gateway
Service White list checker AUDIT Access and Policy control point Services Logon Service
Username /
password Gov Gateway
authentication Non-MoD RLI Users from claims-aware systems Users from non-claims systems MOD Users
from outside
RLI Claims / Tokens 1 – MoD User wanting HR environment
2 - Authenticates to Gov Gateway
3 – Federated access provided (given valid claim from 2-factor card)
4 - to (REDACTED) HR Apps
5 – or other sites. 1 2 3 4 5 5<br>
2 - Authenticates to Gov Gateway
3 – Federated access provided (given valid claim from 2-factor card)
4 - to (REDACTED) HR Apps
5 – or other sites. 1 2 3 4 5 5<br>
16
Federated Approach (4 of 5) 16 RLI Intranet non-Restricted Intranet Restricted sites HR Apps Intranet non-Restricted Collaboration apps Boundary HTTP
Gateway
Service CWE
Collaboration
Service White list checker AUDIT Access and Policy control point Services Logon Service
Username /
password Gov Gateway
authentication Non-MoD RLI Users from claims-aware systems Users from non-claims systems MOD Users
from outside
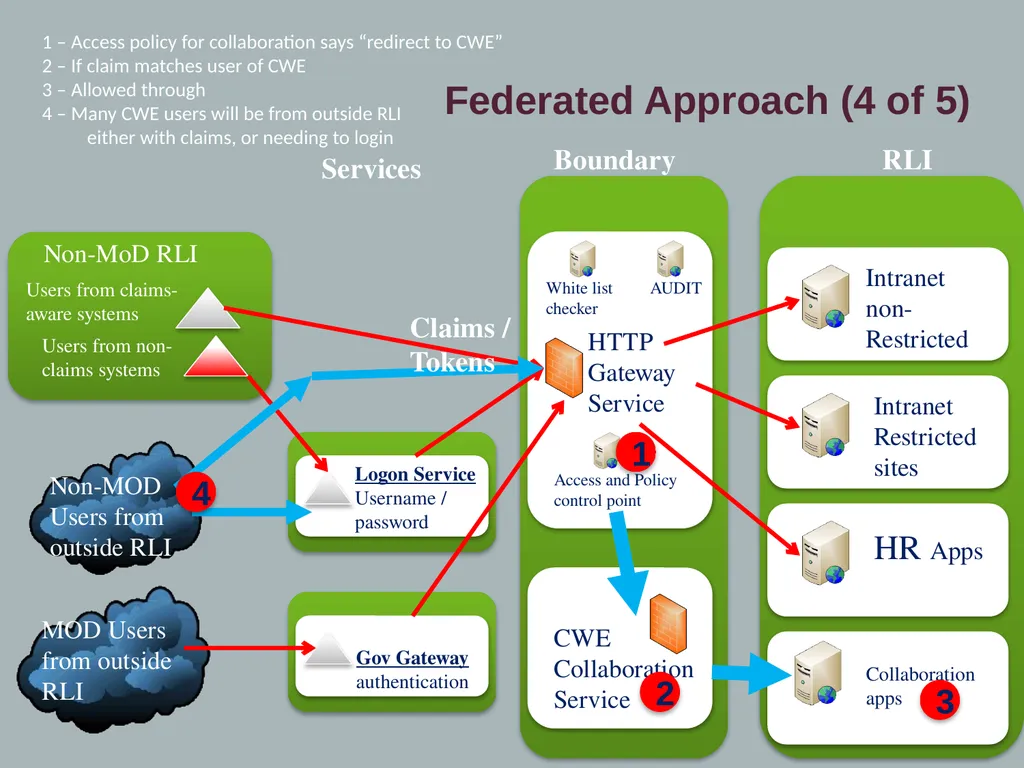
RLI Non-MOD Users from outside RLI Claims / Tokens 1 – Access policy for collaboration says “redirect to CWE”
2 – If claim matches user of CWE
3 – Allowed through
4 – Many CWE users will be from outside RLI
either with claims, or needing to login 4 1 2 3<br>
2 – If claim matches user of CWE
3 – Allowed through
4 – Many CWE users will be from outside RLI
either with claims, or needing to login 4 1 2 3<br>
17
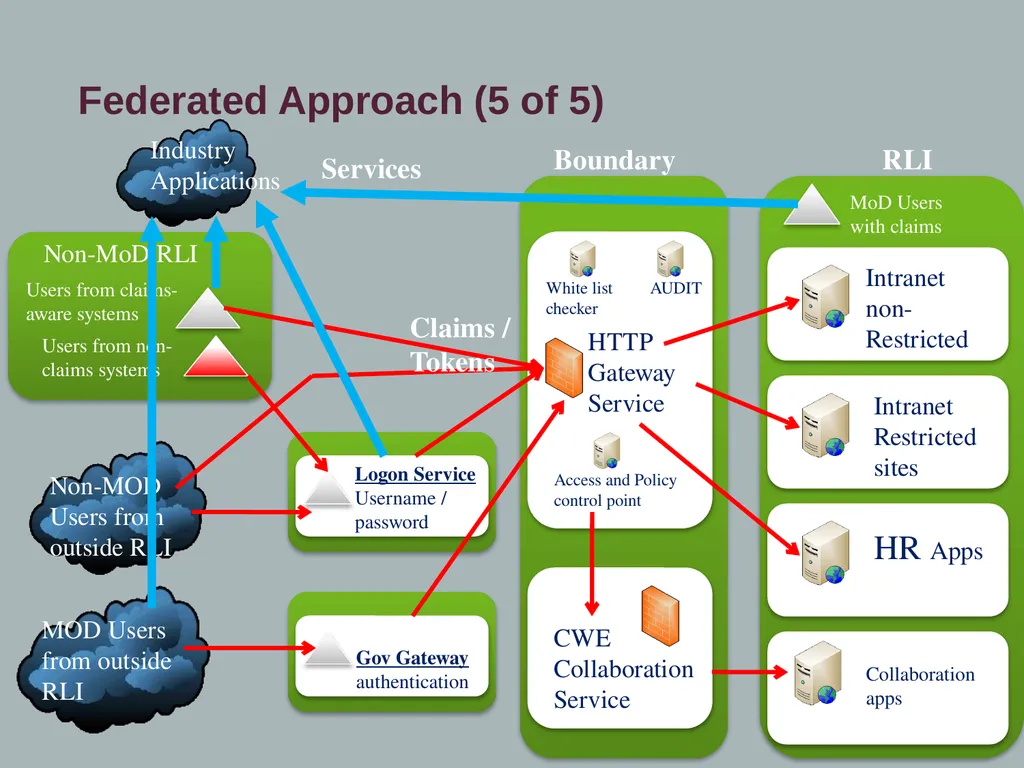
Federated Approach (5 of 5) 17 RLI Intranet non-Restricted MoD Users with claims Intranet Restricted sites HR Apps Intranet non-Restricted Collaboration apps Boundary HTTP
Gateway
Service CWE
Collaboration
Service White list checker AUDIT Access and Policy control point Services Logon Service
Username /
password Gov Gateway
authentication Non-MoD RLI Users from claims-aware systems Users from non-claims systems Industry
Applications MOD Users
from outside
RLI Non-MOD Users from outside RLI Claims / Tokens<br>
18
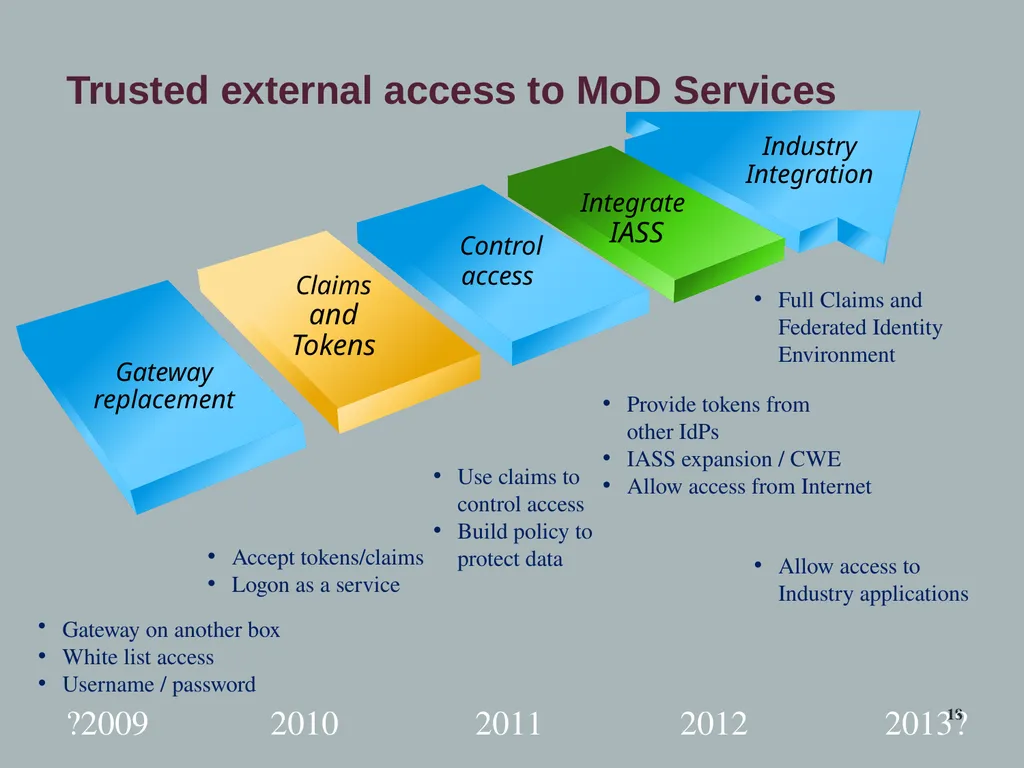
Trusted external access to MoD Services 18 Full Claims and
Federated Identity
Environment
Allow access to Industry applications Provide tokens from other IdPs
IASS expansion / CWE
Allow access from Internet Use claims to control access
Build policy to protect data Accept tokens/claims
Logon as a service Gateway on another box
White list access
Username / password ?2009 2010 2011 2012 2013?<br>
19
Internet Access Shared Service (IASS):
A Success story Implemented to enable MOD “orphans” to access online HR services
Requirements:
Only access and display certain information (sensitive HR data to be redacted)
Look like normal application (simple user training)
No changes to original applications (cost saving)
Leave no trace on the client device (no download)
2-Factor authentication (e.g. Smart card, without a PC attached reader)
Authenticate at Government Gateway 19<br>
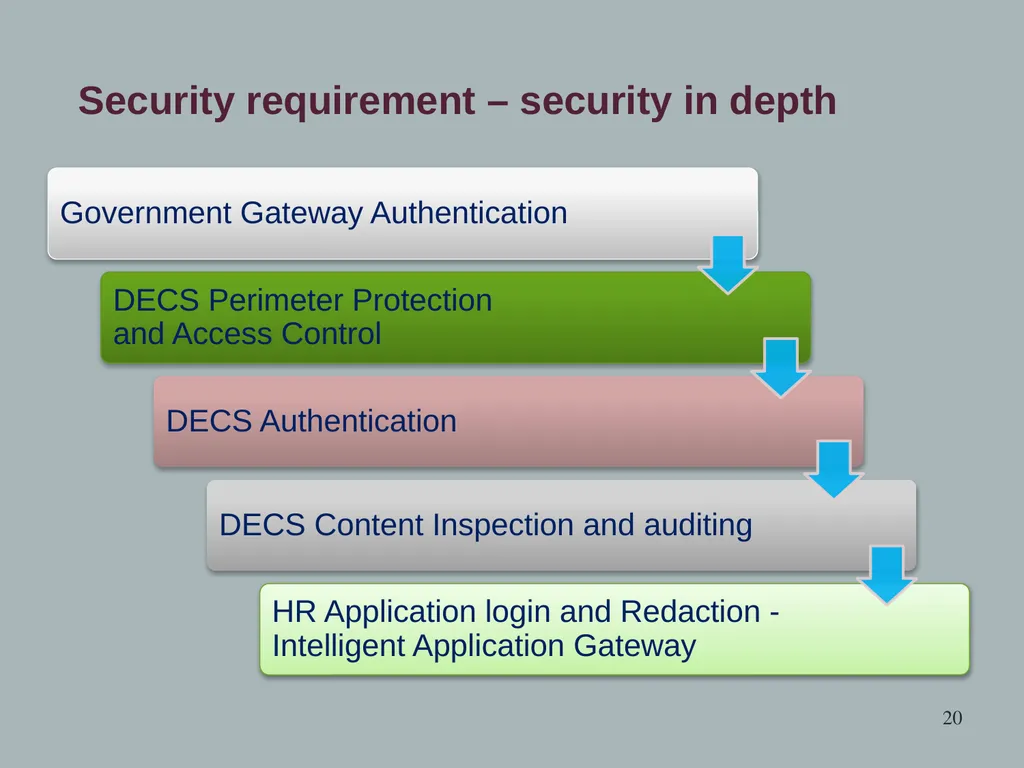
20
Security requirement – security in depth 20<br>
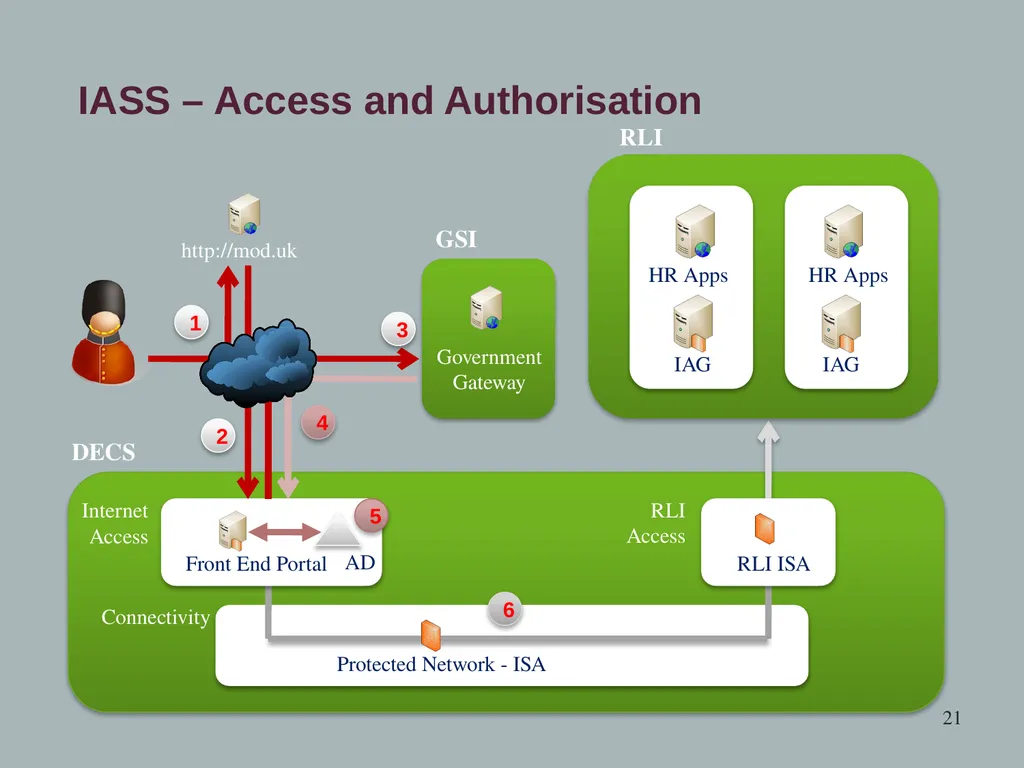
21
IASS – Access and Authorisation 21 GSI Government
Gateway http://mod.uk DECS RLI ISA RLI
Access Protected Network - ISA Connectivity Front End Portal Internet
Access AD HR Apps HR Apps RLI IAG IAG<br>
Gateway http://mod.uk DECS RLI ISA RLI
Access Protected Network - ISA Connectivity Front End Portal Internet
Access AD HR Apps HR Apps RLI IAG IAG<br>
22
Thank You Challenges facing the MoD
Similar to many other organisations
Emphasis on Security
Goals: Coherent Approach to
Federated Identity
Attribute based authentication
Enabling Capabilities
Secure authentication – Smart cards
Secure use of certificates for attributes – PKI
Secure collaboration standards - TSCP
A success story
Short term, reachable steps
Helps to demonstrate the strategy is working 22<br>